
 Do Son
Intego exposes a malicious Ledger Live app for macOS. Using weaponized Electron ASAR archives and a TLS bypass, OSX/Amos silently siphons your seed phrases.
phishing

NCSC warns high-risk individuals of Russian and Chinese state actors hijacking WhatsApp and Signal. Protect your chats with these essential 2026 defense tips.

Gen Digital warns of a reservation hijack scam using real stay dates and hotel names to steal credit cards via WhatsApp. Don't tap that link!
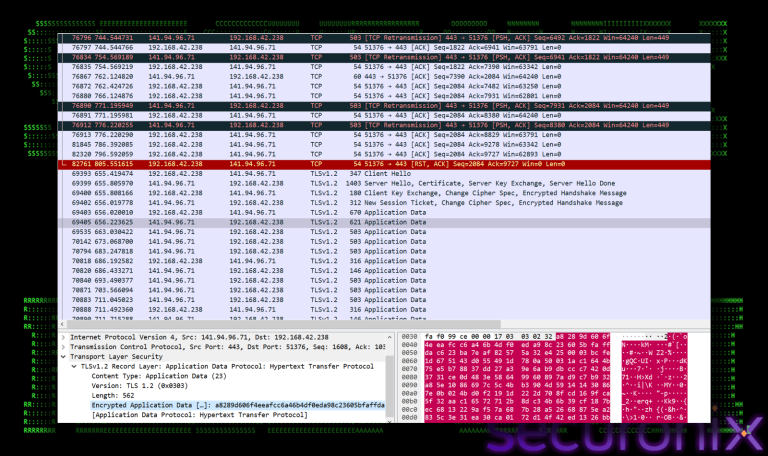
Securonix uncovers FAUX#ELEVATE, a 25-second attack using 10MB "inflated" VBScripts to steal credentials and mine crypto in French corporate environments.
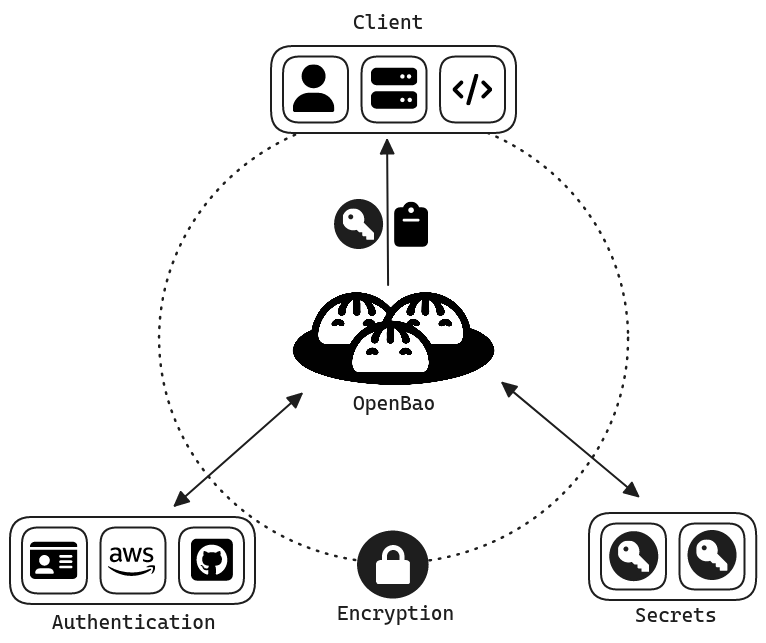
OpenBao patches critical 9.6 and 9.4 CVSS flaws in OIDC flows. Learn how "direct mode" enables session hijacking and XSS token theft. Update to 2.5.2 now.
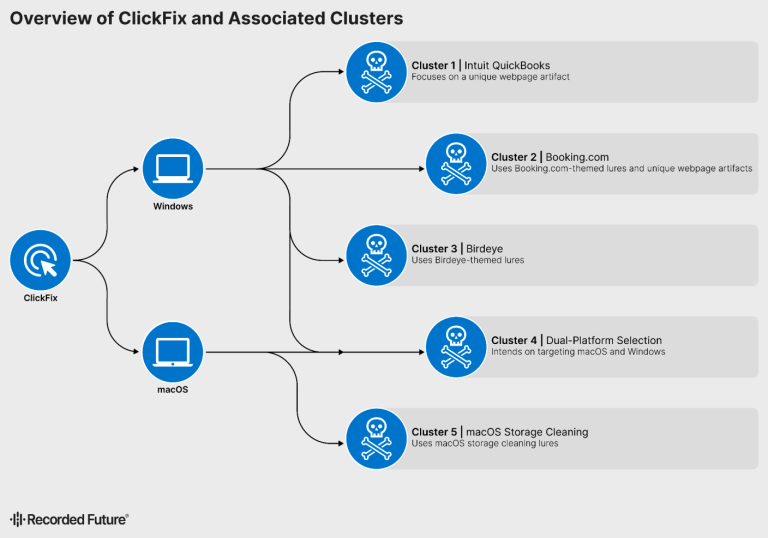
ClickFix has evolved into a high-ROI malware template used by APT28. Learn how this social engineering trick bypasses security by mimicking system errors.

Sekoia TDR reveals Silver Fox's latest tactics. From tax-themed phishing to WhatsApp clones, this China-based group combines espionage with financial theft.
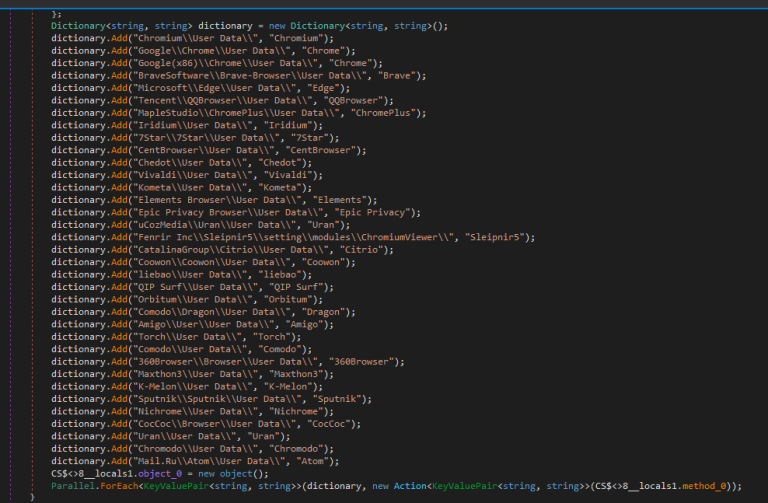
Malwarebytes uncovers a PureHVNC RAT campaign using Google Forms to bait professionals. Learn how this stealthy infection chain targets 2026 business docs.

Trend Micro uncovers a selective PureLog Stealer campaign using fake legal notices and fileless execution to target healthcare and government sectors.
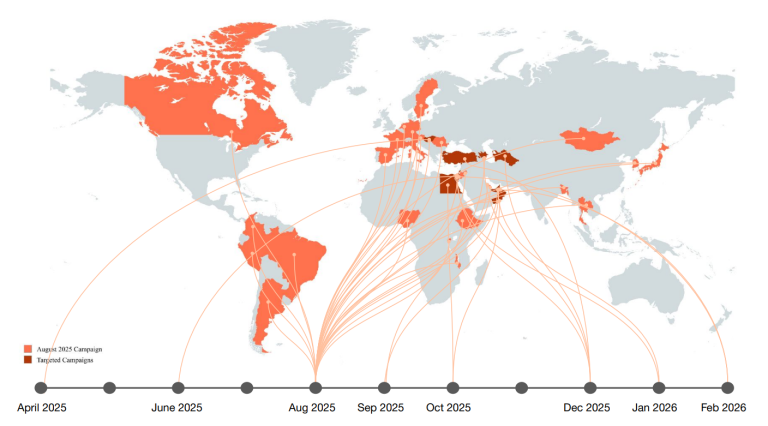
Unit 42 reveals Iranian APT Boggy Serpens is weaponizing hijacked accounts, AI-generated code, and Rust malware to infiltrate critical infrastructure.
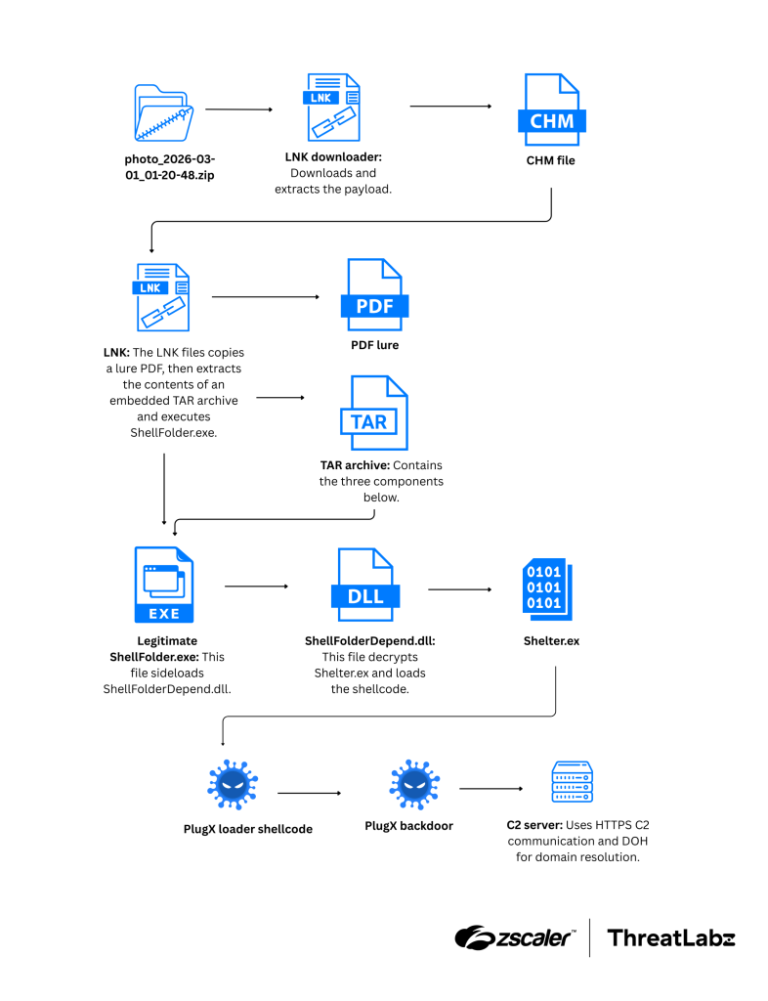
ThreatLabz reveals how China-nexus actor Mustang Panda weaponized Middle East conflict lures to deploy a stealthy PlugX backdoor within 24 hours.
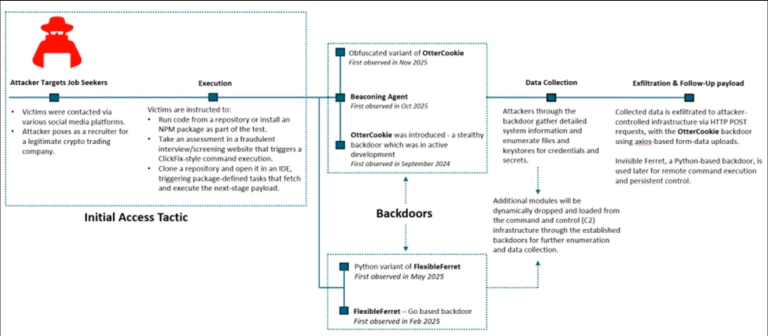
Microsoft exposes the "Contagious Interview" campaign. Fake recruiters trick developers into installing Invisible Ferret malware during coding tests.
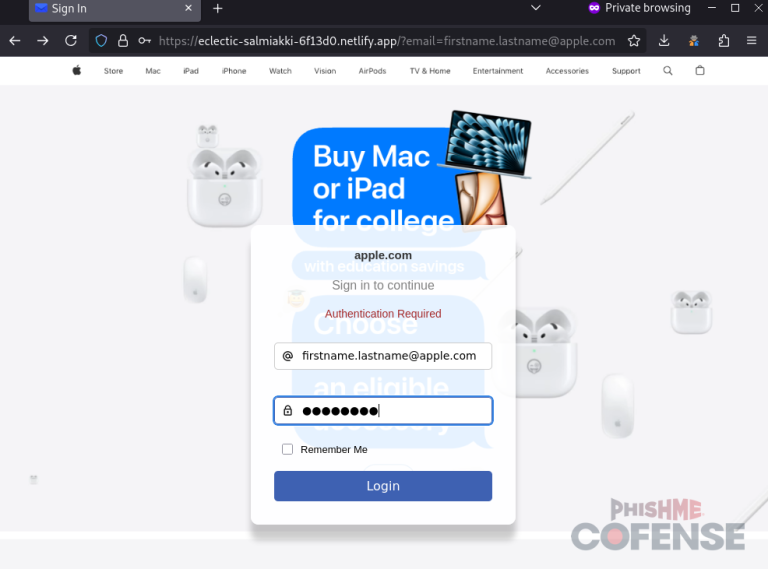
A new Cofense report reveals how hackers abuse legitimate Telegram Bot APIs to create stealthy Command and Control (C2) centers for data exfiltration.

LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.

Cybercriminals are using a fake Google security checkup (google-prism) to trick you into installing powerful PWA malware. Learn how to spot the trap.

Infoblox uncovers a novel phishing tactic abusing the .arpa TLD. Attackers hijack internet "plumbing" to bypass firewalls and deliver brand-impersonation scams.
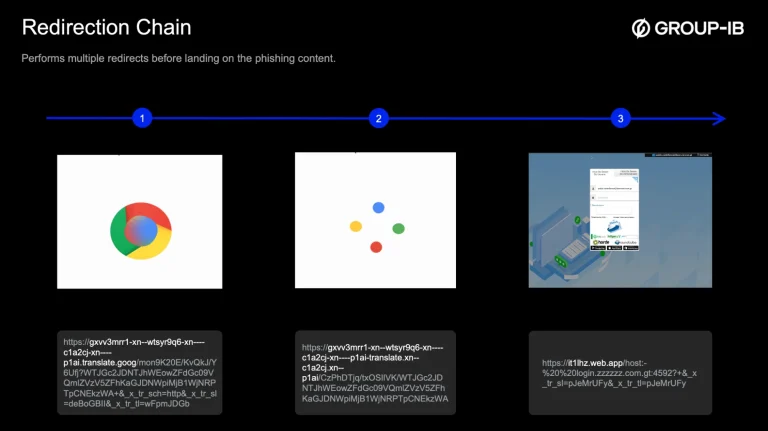
Group-IB uncovers "GTFire," a massive credential-harvesting operation abusing Google Firebase and Translate to bypass security filters in 100+ countries.

Varonis uncovers 1Campaign, a sophisticated tool by 'DuppyMeister' that helps hackers bypass Google Ads security to deliver phishing and crypto drainers.
FortiGuard Labs exposes a massive Silver Fox APT campaign targeting Taiwan. Hackers use tax-themed phishing and BYOVD attacks to deploy Winos 4.0 malware.

Malwarebytes exposes a deceptive campaign using fake Windows 11 Facebook ads to trick users into downloading stealthy info-stealing malware.
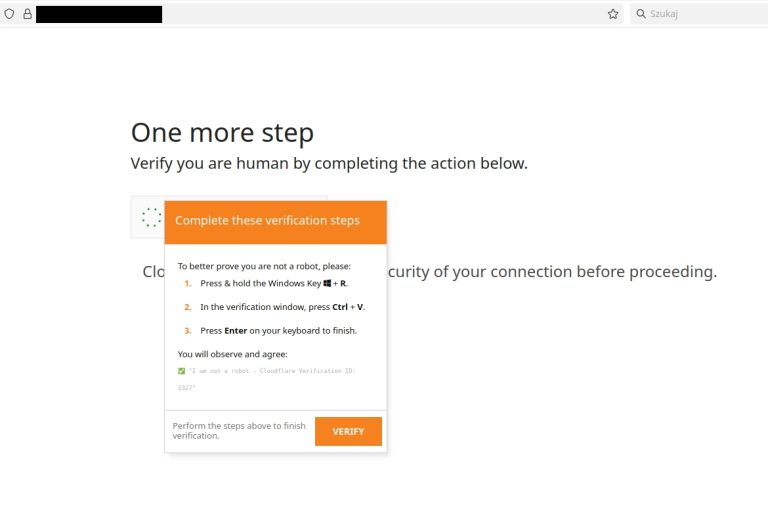
CERT Polska reveals how a fake "ClickFix" CAPTCHA campaign tricked users into deploying evasive Latrodectus and Supper malware. Protect your network now.

Bridewell warns of Russian hackers targeting Booking.com. Phishing kits steal hotel staff creds to scam guests with "I Paid Twice" messages.