
 Do Son
Trend Micro uncovers a phishing campaign abusing Kuse.ai and VEC to steal credentials via markdown notes. Don't trust a domain just because of its reputation.
phishing

Bitdefender uncovers a massive smishing campaign targeting drivers with fake toll and parking fines. Over 79,000 messages sent across 12 countries.

Citizen Lab reveals "Tall Tales," a PRC campaign using GLITTER CARP and SEQUIN CARP to hunt activists and ICIJ journalists via private contractors.
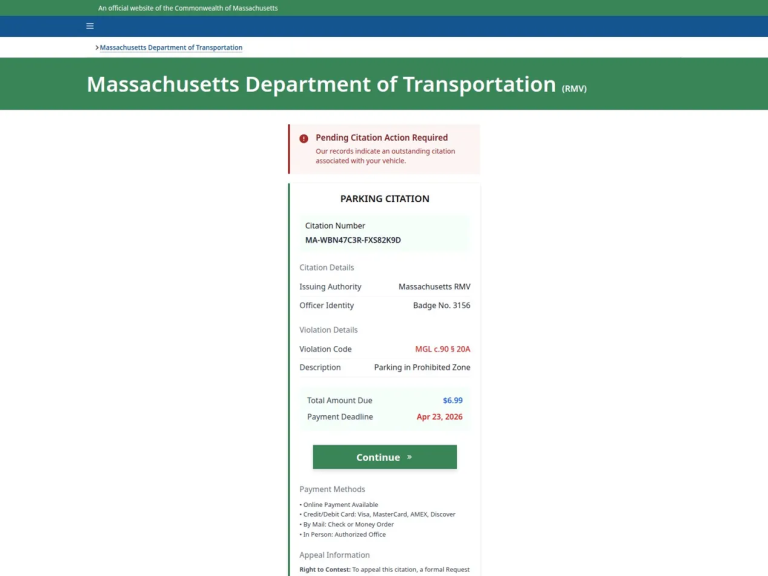
Cyble uncovers "Operation Trust Trap," a 16,800-domain network weaponizing *.gov trust to steal credentials. See how APT36 and others hijack the human eye.
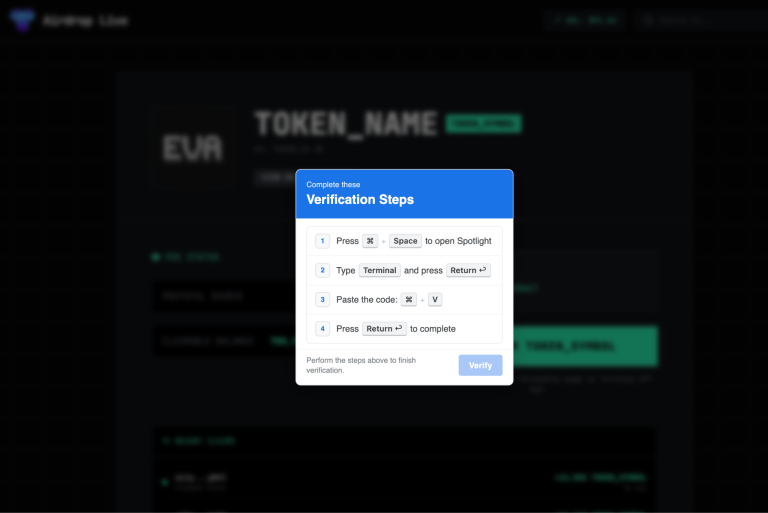
Netskope uncovers a ClickFix macOS campaign that holds the UI hostage to steal system passwords, Keychains, and 200+ browser extensions.
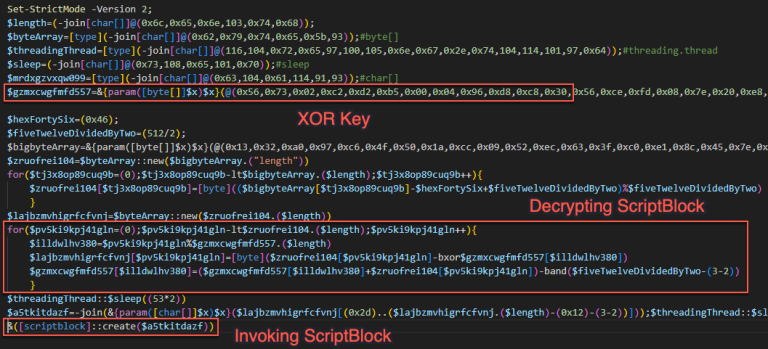
Rapid7 uncovers a fake Claude AI installer using ClickFix techniques to bypass AMSI and inject shellcode. Stay safe from this sophisticated AI-themed threat.
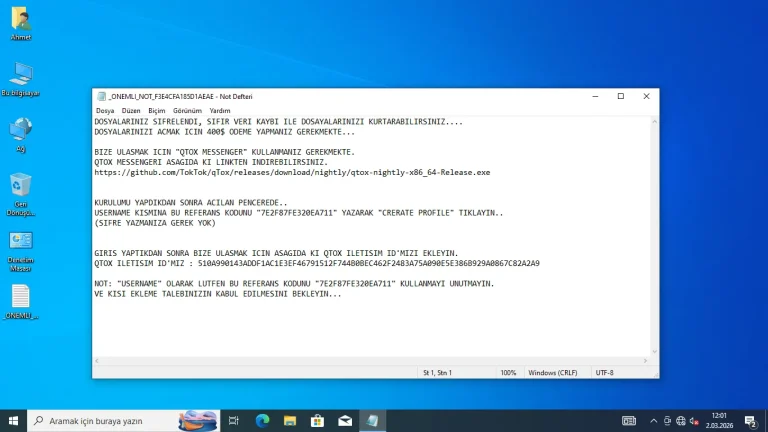
Acronis uncovers JanaWare, a persistent ransomware targeting Turkey since 2020. Discover how geofencing and polymorphism keep this threat in the shadows.

North Korea’s "graphalgo" campaign uses fake job interviews and real Florida LLCs to infect developers. Learn how to spot this sophisticated state-sponsored trap.
Booking.com confirms a data breach exposing names, emails, and itineraries. Learn how to verify official alerts and protect yourself from new phone scams.

Microsoft DART uncovers Storm-2755, a "payroll pirate" using AiTM traps and SEO poisoning to steal salaries. Protect your organization from this MFA bypass.
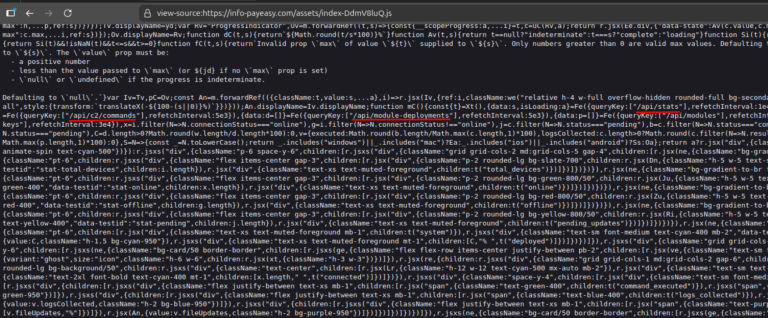
Hunt.io discovers Canis C2, an AI-assisted surveillance framework targeting all major OSs. An exposed API revealed payloads and source code. Read more here.
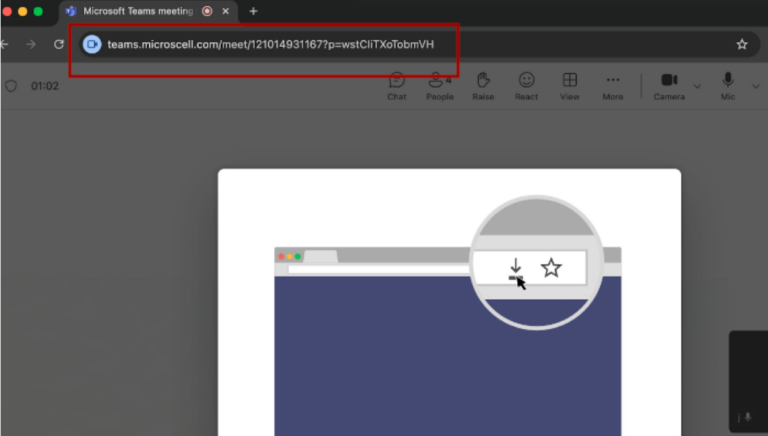
North Korean group UNC1069 (BlueNoroff) targets Web3 with fake Zoom/Teams links. 164 domains blocked. Secure your crypto assets and browser extensions now!

HPE Aruba Networking patches a critical 8.8 CVSS open redirect in its Private 5G Core. Prevent credential harvesting—update to version 1.25.3.1 immediately.
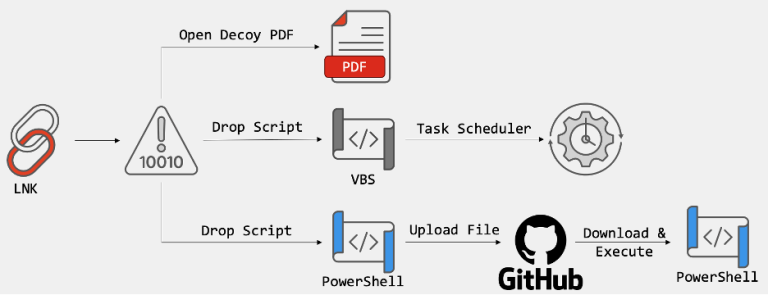
FortiGuard Labs unmasks a South Korean espionage wave abusing the GitHub API for C2 and using LNK files to stay invisible. Protect your network from LotL.

Attackers are impersonating Linux leaders on Slack to drop malware via fake Google Workspace links. Protect your dev environment—verify before acting!

Microsoft Defender warns of a 2026 WhatsApp malware campaign using VBS and renamed system tools to hijack PCs via AWS and Tencent Cloud. Stay alert!
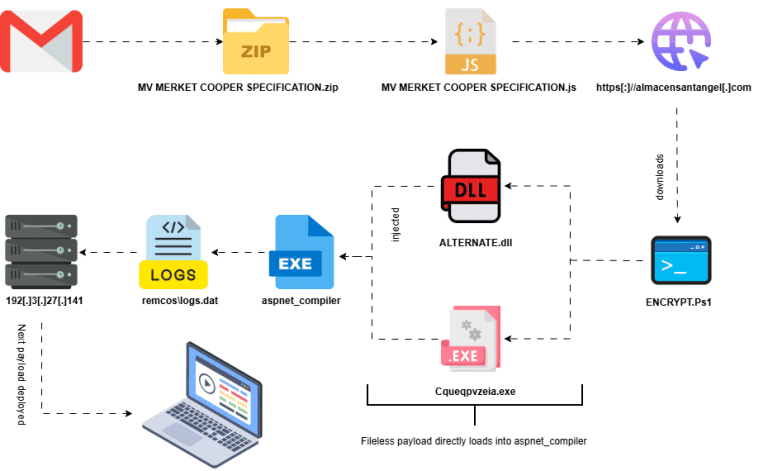
Researchers unmask a fileless Remcos RAT campaign using obfuscated JS and LOLBins to hijack systems in-memory. See the technical breakdown from Lat61.

Sophos MDR uncovers STAC6405, a phishing campaign abusing RMM tools like LogMeIn for unattended access. Learn how to spot the "Special Invitation" lure.
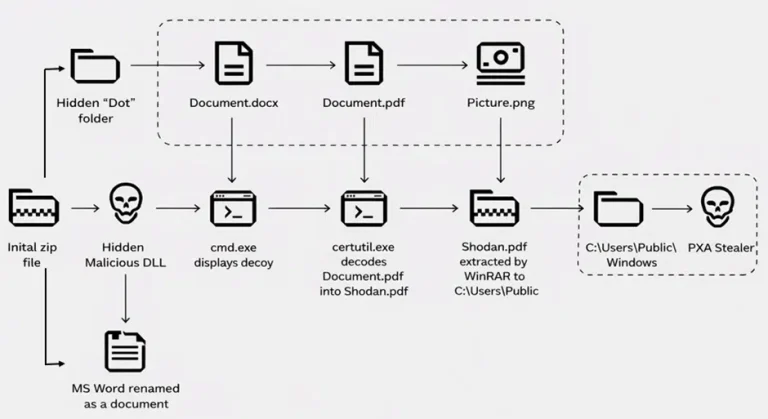
PXA Stealer activity surges in Q1 2026, targeting global finance. Learn how this Python-based malware uses Telegram and LOLBins to hijack crypto and banking data.

Proofpoint identifies a surge in 2026 tax scams using RMM tools (39%) to bypass security. Learn how TA4922 and TA2730 target your data this filing season.

The Axios npm hijack exposed millions to a RAT. Discover how North Korean-nexus actor UNC1069 used a masterful phishing ruse to bypass 2FA and steal credentials.
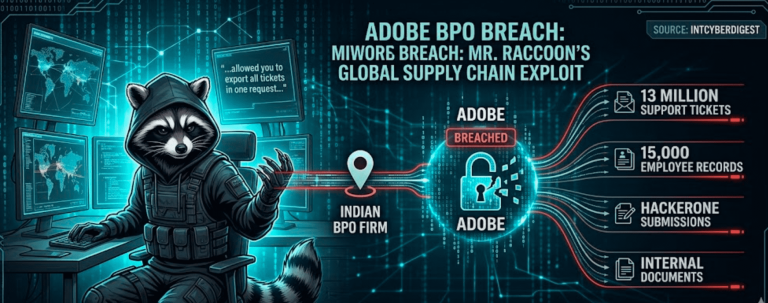
13M Adobe tickets leaked! Mr. Raccoon bypassed elite defenses by targeting a BPO partner in India. See how the "human element" cracked the supply chain.