
 Do Son
Cisco Talos discovered the JWR phishing framework, a new PhaaS variant. Read our JWR phishing framework analysis to learn about this real-time cyber threat.
phishing

A SafePal data breach exposed order information for about 39,798 customers via an order-tracking flaw. Wallet funds and keys were not affected.

Kimsuky AI operations reveal a North Korea threat actor testing local LLMs. Suspected state hackers are building new capabilities to automate phishing.

Trellix details a DCRat campaign using SVG HTML smuggling and process hollowing to deploy DarkCrystal RAT via a Colombian judicial lure.

Delta Air Lines is investigating a rogue WiFi hotspot on Flight 591 carrying DEF CON attendees, used to phish Google credentials via deauth attacks.

Researchers expose the Greatness PhaaS platform, an AiTM phishing kit sold on Telegram that steals Microsoft 365 tokens past MFA.

The SMOKE#SCREEN campaign abuses ScreenConnect RMM and Cloudflare tunnels via fake Zoom and Adobe update lures, Securonix reports.
A global phishing campaign hides a low-detection Lua loader inside fake .ttf font files to drop Remcos, XWorm, Agent Tesla, and a Snake Keylogger.

Discover the details behind the Nextcloud website hacked incident. Hackers exploited a vulnerability to redirect users to a dangerous phishing domain.
A misconfigured server exposed three AiTM phishing operators running Evilginx MFA bypass and Device Code attacks on Microsoft 365 accounts.

Clubfoot Wolf targets Russian companies with phishing that drops NetSupport Manager as a stealthy remote access tool, BI.ZONE reports.

A LNK phishing attack drops a Node.js backdoor and hides its C2 on the TON blockchain using EtherHiding, LevelBlue reports.
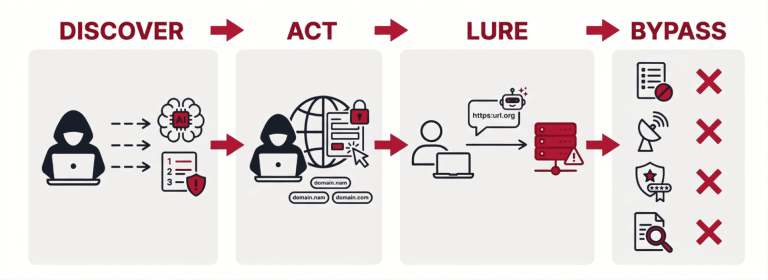
Unit 42 warns phantom squatting attacks weaponize AI hallucinated domains, with 13,229 malicious URLs and 250,000 fake domains open to registration.
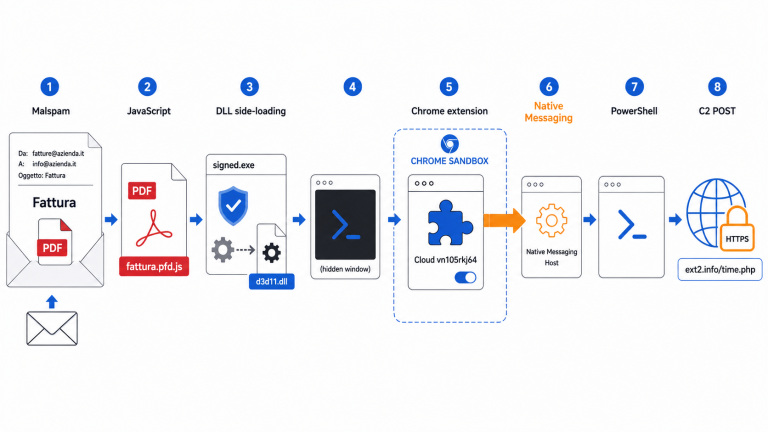
A Native Messaging backdoor pairs a malicious Chrome extension with a local host to run PowerShell, escaping the browser sandbox, says D3Lab.
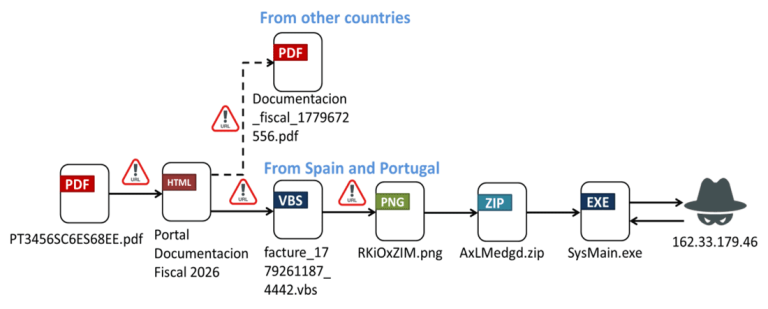
FortiGuard Labs discovered a new Ousaban banking trojan campaign. The attackers use geo-blocking to target banking users in Spain and Portugal.
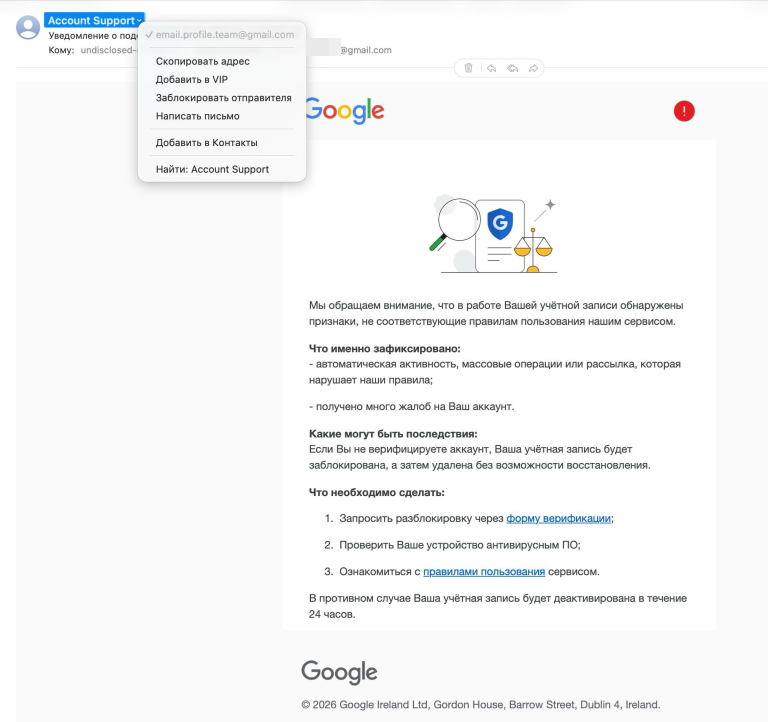
A suspected UNC1151 phishing campaign targets Belarusian politicians and Ukrainian portals to steal credentials using deceptive login pages.

An active hospitality malware campaign uses photo lures and authentication laundering to infect hotel networks with a persistent Node.js implant.

Threat actors are using RAR archive phishing to deploy Thailand healthcare malware. The campaign targets hospitals to steal credentials and sensitive data.
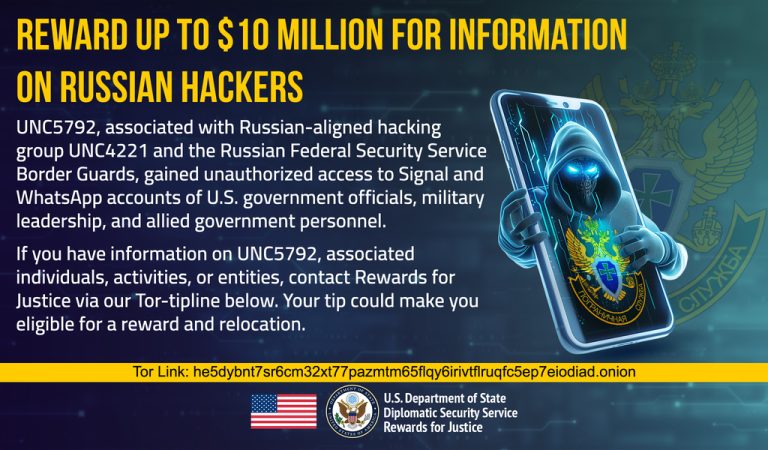
The U.S. offers a $10 million reward for UNC5792, a Russian FSB-linked group behind Signal and WhatsApp phishing of officials.
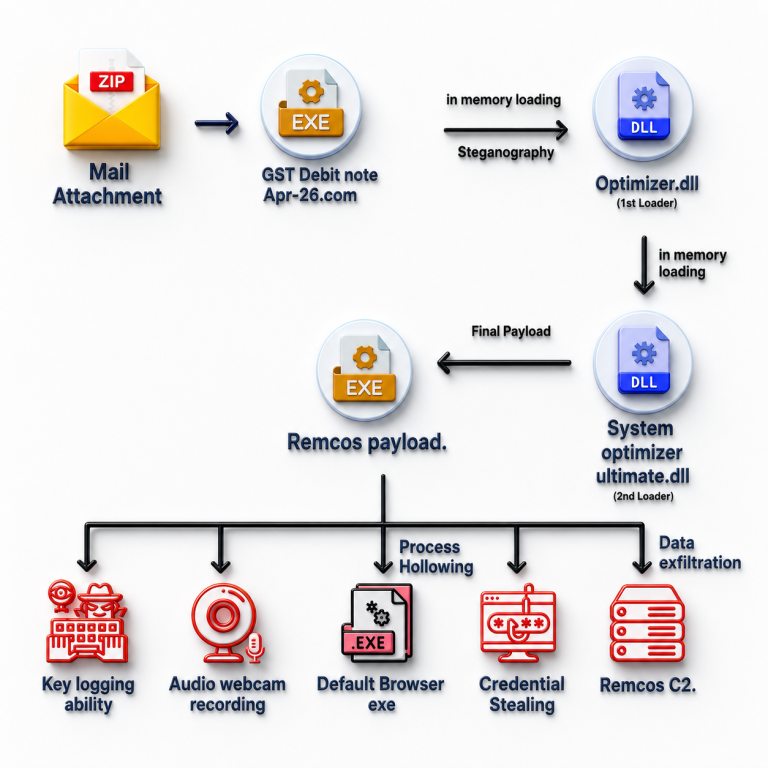
A steganographic loader hides Remcos RAT inside a bitmap and runs it in memory. K7 ties the fileless campaign to India via fake GST lures.

Cyble's Operation FanTrap uncovered a FIFA 2026 fraud ecosystem with nearly 4,000 fake domains pushing ticket scams, streaming lures, and phishing.

The GitBait phishing campaign abuses GitHub Pages and the SheetBest API to steal banking credentials from at least 12 Mexican financial institutions.