
 Do Son
Hackers abuse Atlassian Jira notifications to bypass spam filters. Trend Micro warns of scams targeting enterprise users via trusted alerts.
phishing
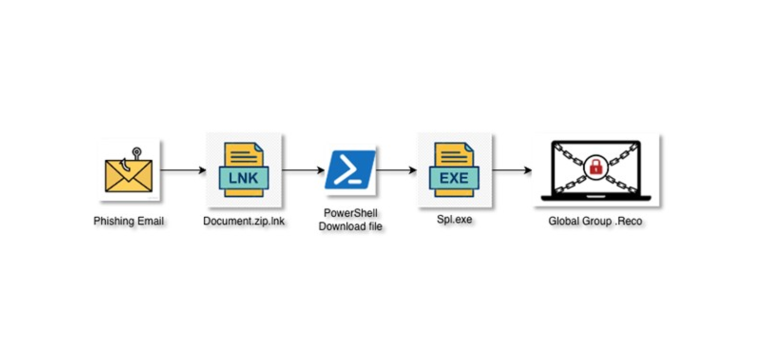
Phorpiex botnet returns in "Your Document" phishing campaign. Attackers use malicious .LNK files and hidden extensions to trick users.

Malicious Outlook add-in "AgreeTo" steals 4,000+ credentials. Attackers hijacked the abandoned tool in the official store. Uninstall immediately.

LummaStealer is back, evading takedowns with "ClickFix" tactics. Bitdefender reveals how fake CAPTCHAs trick users into running malware. Stay alert.

New Telegram phishing campaign abuses the "This is me" feature for account takeover. CYFIRMA reveals a global framework evading detection. Stay alert.

Phishing emails use malicious Excel files to deploy XWorm RAT. The fileless attack exploits CVE-2018-0802 to steal data & control systems.

Warning: 7zip [.] com has been hijacked to spread residential proxy malware. Learn how to identify this 7-Zip impersonator and protect your system.

Hackers abuse PayPal & Apple to send "perfect" phishing emails. Learn how DKIM Replay attacks bypass security filters & DMARC checks.

Darktrace finds Mac malware using a fake "Compatibility Wizard" to trick users. The AppleScript attack bypasses TCC to drop a Node.js backdoor.

Stan Ghouls group targets Uzbekistan via fake court emails and malicious Java loaders. Learn how they deploy NetSupport RAT to spy on victims.

Sophisticated phishing abuses Vercel Blob & PDFs to bypass filters. Stolen credentials are exfiltrated via Telegram bots. Learn how to spot this attack.

"ConsentFix" phishing tricks users into pasting OAuth codes from Azure CLI, bypassing MFA and Conditional Access. Detect this "fix" scam now.

New AI-generated malware campaign targets job seekers. Vietnamese actor "Huna" uses fake job offers to deliver PureRAT via Dropbox.

Microsoft patches zero-day CVE-2026-21509, actively exploited in the wild. The flaw bypasses OLE security in Office 2016/2019. Update to Build 16.0.10417+.

DPRK spies weaponize Visual Studio Code tunnels to bypass security. Darktrace reveals a campaign targeting South Korea with government decoys.

Unit 42 reveals "living" phishing pages built by GenAI on the fly. These polymorphic attacks evade detection by generating unique code for every victim.

Group-IB reveals a sophisticated loan phishing campaign in Peru. Scammers use the Luhn algorithm to validate stolen credit cards via fake ads.

Scammers target PNB MetLife users via mobile phishing. Attackers use Telegram bots to steal data & manipulate clipboards for UPI fraud.

New PURELOGS campaign uses Archive.org images to hide malware. For just $150, this MaaS steals crypto & passwords via fileless attacks. Spot the signs.

Nomad Leopard targets Afghan officials with fake ministry docs. SEQRITE reveals how the "afghanking777000" OPSEC fail exposed the spies.

Genians reveals "Operation Poseidon": Konni APT exploits Google & Naver ad redirects to bypass defenses and deploy EndRAT.

New fileless Remcos RAT campaign uses a "[virus detected]" shipping lure to inject malware into memory via process hollowing. See how to spot it.