 Do Son
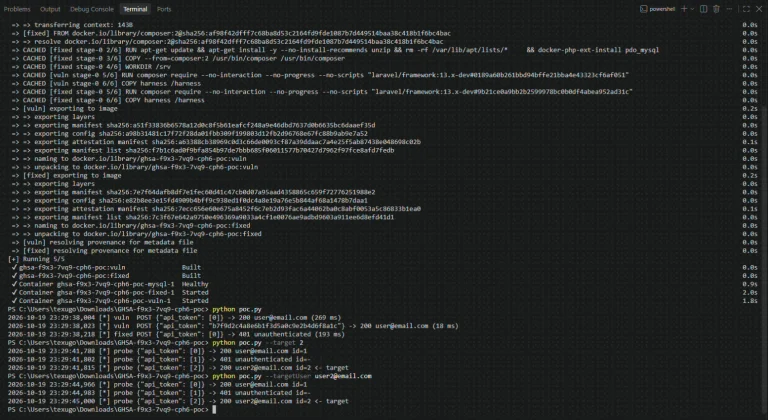
A public PoC is out for CVE-2026-114509, a Laravel authentication bypass in TokenGuard enabling account takeover. Upgrade to 12.68.0 or 13.29.0.
Account Takeover
A critical Laravel authentication bypass (CVSS 9.2) in TokenGuard enables account takeover without a token. Upgrade to 13.29.0 or 12.68.0.
Kiteworks vulnerabilities fixed in 9.5.1 include CVE-2026-102115, a 9.8 password reset flaw that enables admin account takeover. Patch now.

A new AiTM phishing campaign targets healthcare. Learn how this healthcare AiTM phishing campaign chains compromised accounts to bypass MFA.
A Dropbox Lenovo ID SSO flaw let attackers take over accounts with just an email address, no password needed. Dropbox has revoked sessions and hardened login.
Attackers exploit CVE-2026-71362, an unauthenticated Adobe Commerce account takeover flaw (CVSS 9.1). Details and PoC are public. Patch now.
A critical TranslatePress vulnerability (CVE-2026-19632) lets attackers steal admin reset links and take over 400,000 WordPress sites. Update to 3.3.2 now.
A critical EverShop account takeover flaw, CVE-2026-72843, exposes systems to an eCommerce platform vulnerability. Update to version 2.2.1 immediately.
A Keycloak account takeover flaw, CVE-2026-18963, lets attackers reset any user's password with no email verification. Update to 26.7.2 now.

CVE-2026-68067 (CVSS 9.8) lets attackers control user accounts on the Mira Hormone Monitor by bypassing the cloud login. Eight flaws total.

WSO2 patched four critical account takeover flaws, including CVE-2026-5430 at CVSS 10 via JWT auth bypass. Details and fixes inside.

CVE-2026-18577 is being exploited in the wild for N-central account takeover. An incomplete patch let attackers gain admin access. Update to 2026.3.1.7.

Kimai vulnerability CVE-2026-52824 (CVSS 9.1) lets attackers forge cookies for account takeover via a default Docker APP_SECRET. Update to 2.58.0 now.
Zoom vulnerability CVE-2026-53412 (CVSS 9.8) allows unauthenticated account takeover over the network. Update Zoom Workplace for Windows to 7.0.0 now.
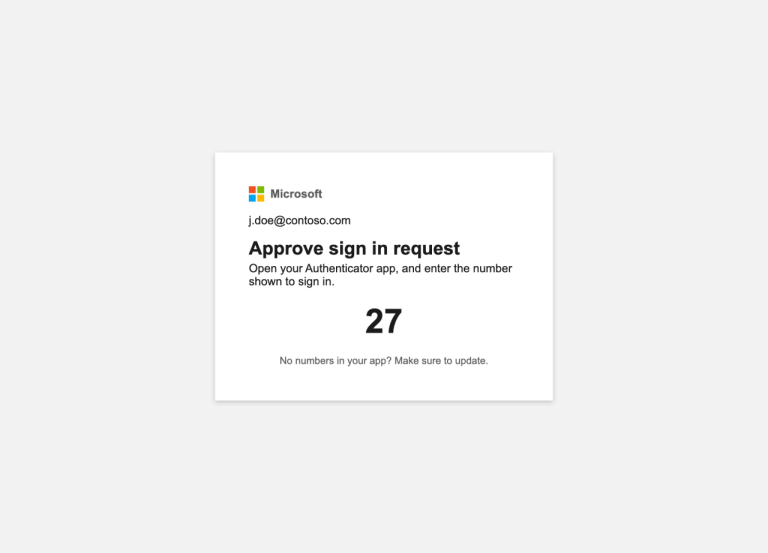
A vishing attack tricks Microsoft 365 users into passkey phishing, letting O-UNC-066 enroll its own passkey and hijack Entra accounts for extortion.
CVE-2026-53513 is a Better Auth SSRF flaw (CVSS 9.6) in the SSO plugin. It exposes cloud metadata and enables account takeover. Patch to 1.6.11 now.

A critical Ghost cache poisoning bug lets an unauthenticated x-ghost-preview header hijack staff accounts. Update to Ghost v6.37.0 now.
A critical Poweradmin host header injection flaw (CVE-2026-54588) lets attackers hijack DNS admin accounts. Update to 4.2.4 or 4.3.3 now.

A critical ManageEngine account takeover vulnerability (CVE-2026-11374) exposes AD360 integrated deployments to unauthenticated attacks. Update systems now.

A new device code phishing campaign abuses Microsoft's OAuth flow to hijack Microsoft 365 accounts, no password stealing needed. How to spot it.

A critical phpBB authentication bypass (CVE-2026-48611) lets attackers hijack any account on thousands of forums. Update to 3.3.17 now.
Budibase patches a critical 9.9 CVSS SCIM authorization bypass (CVE-2026-46425). Basic users can delete admins and hijack accounts. Update now!