 Do Son
Sentry reveals a critical 9.1 CVSS flaw (CVE-2026-42354) in SAML SSO. Multi-org instances are at risk of account takeover via identity linking. Patch now!
Account Takeover
A critical 9.9 CVSS IDOR flaw in Comet Backup allows complete cross-tenant account takeovers. Self-hosted administrators must patch servers immediately!
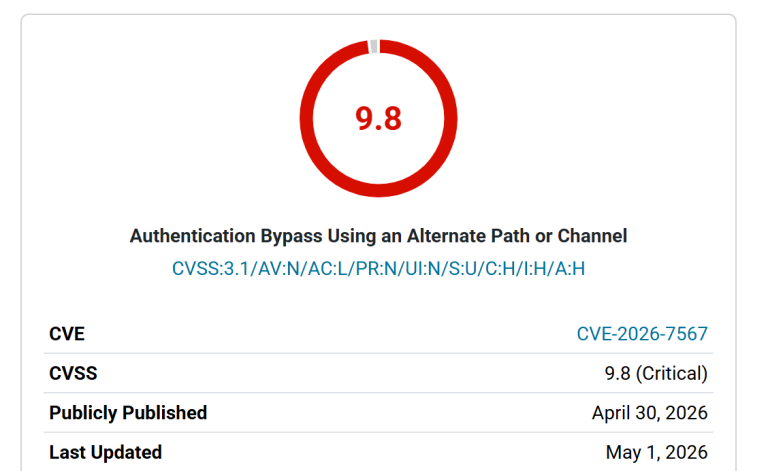
A critical 9.8 CVSS vulnerability in the Temporary Login plugin puts 40,000+ WordPress sites at risk of account takeover. Patch to version 1.1.0 now!
AVideo’s YPTSocket plugin faces a critical CVSS 10 vulnerability. Unauthenticated attackers can hijack every active session at once. No patch is available.
Proofpoint warns that 10% of M365 account takeovers use malicious mailbox rules to steal data and hide alerts. Secure your cloud identity—check your rules!

Cisco patches a critical 9.8 CVSS flaw (CVE-2026-20093) in IMC. Unauthenticated attackers can change admin passwords and seize full control. Update now!

Dutch intelligence (MIVD/AIVD) warns of a global campaign using social engineering to silently hijack Signal and WhatsApp accounts of high-profile targets.

A critical 9.3 CVSS XSS vulnerability (CVE-2026-29191) in ZITADEL's SAML endpoint allows unauthenticated 1-click account takeover. Upgrade immediately.

Vikunja v2.0.1 patches critical flaws (CVE-2026-27575 & 28268) where "immortal" reset tokens and persistent sessions allow attackers to hijack accounts forever.

RustFS patches a critical 9.1 CVSS XSS flaw (CVE-2026-27822). Attackers can steal S3 credentials via a malicious file preview. Update to 1.0.0-alpha.83 now!

Parse Server patches a critical 9.1 CVSS vulnerability (CVE-2026-27804). Attackers can forge Google tokens using "alg: none" to hijack any linked user account.
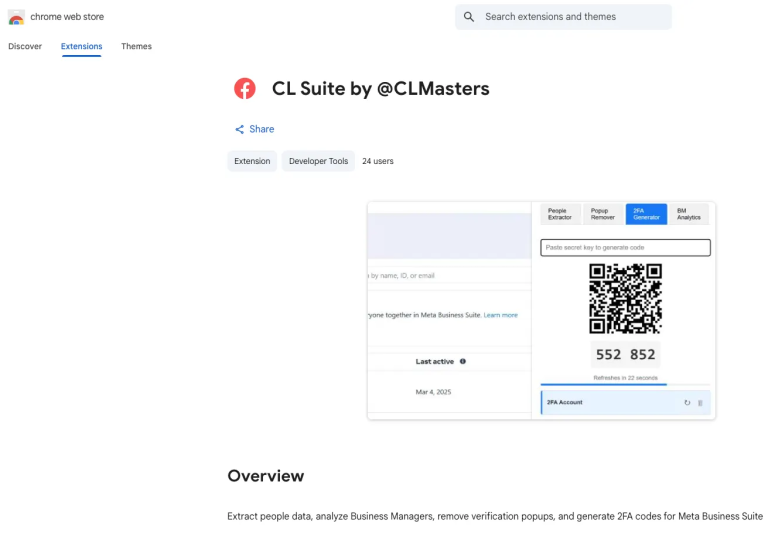
"CL Suite" Chrome extension steals Meta Business 2FA seeds & data. Attackers bypass security even after uninstall. Reset 2FA immediately.

New Telegram phishing campaign abuses the "This is me" feature for account takeover. CYFIRMA reveals a global framework evading detection. Stay alert.

TP-Link fixes critical IDOR (CVE-2025-9520) in Omada Controller allowing admins to hijack Owner accounts. Update now to prevent total network takeover.

Critical Academy LMS flaw CVE-2025-15521 (CVSS 9.8) is being exploited. Unauthenticated attackers can reset admin passwords. Update now to secure your site.

Critical Cal.com flaw (CVE-2026-23478) allows full account takeover via a single API call. CVSS 10.0. Update self-hosted instances to v6.0.7 immediately.

Critical Appsmith flaw CVE-2026-22794 (CVSS 9.7) allows account takeover via Host Header Injection. Update to v1.93 immediately to secure your data.

PrestaShop patches a 9.1 critical flaw (CVE-2025-61922) in the Checkout module. Attackers can hijack accounts via email. PoC available.

The DOJ seized web3adspanels.org, disrupting a $14M bank takeover scheme that used fake Google and Bing ads to steal thousands of credentials.

Proofpoint warns of a surge in device code phishing where attackers abuse Microsoft 365 OAuth flows to hijack accounts and bypass MFA.

China's RedDrip exposed APT zero-day exploitation of Android email clients, achieving 1-click RCE via the ZipperDown flaw to steal account tokens and compromise targets around the Korean Peninsula.

Urgent patch for Post SMTP plugin. A CVSS 9.8 flaw lets unauthenticated attackers read email logs and steal password reset links to take over accounts.