Skip to content
November 20, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Vulnerability News
  • CVE-2025-59934: Critical Flaw in Formbricks Allows Unauthorized Password Resets via Forged JWT Tokens
  • Vulnerability News

CVE-2025-59934: Critical Flaw in Formbricks Allows Unauthorized Password Resets via Forged JWT Tokens

Do Son September 27, 2025 2 minutes read
0
Formbricks Auth Bypass, CVE-2025-59934

The Formbricks project, an open-source platform for building in-app and website surveys, has released an urgent patch addressing a critical authentication vulnerability. Tracked as CVE-2025-59934 with a CVSS score of 9.4 (Critical), the flaw allows attackers to bypass JSON Web Token (JWT) verification and reset user passwords without authorization.

Track every CVE that hits your stack the moment it's exploited.
Get free email alerts →

The issue stems from improper token validation logic. According to the advisory, “This vulnerability stems from a token validation routine that only decodes JWTs (jwt.decode) without verifying their signatures. Both the email verification token login path and the password reset server action use the same validator, which does not check the token’s signature, expiration, issuer, or audience.”

An attacker who learns a victim’s user.id could craft a malicious JWT with an alg: “none” header and authenticate as the victim or reset their password.

The advisory explains: “If an attacker learns the victim’s actual user.id, they can craft an arbitrary JWT with an alg: ‘none’ header and use it to authenticate and reset the victim’s password.”

The report provides a working proof-of-concept (PoC):

  1. Leak the victim’s user.id (e.g., cmfuc8pk60000vxfjud7bcl2w).
  2. Forge a JWT with {“id”:”<victim_user.id>”} and header alg:”none”.
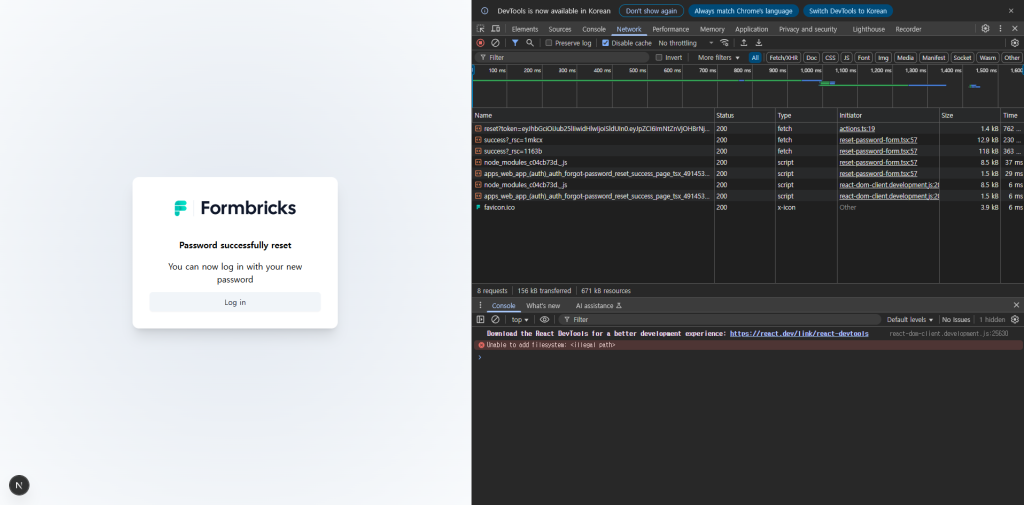
  3. Submit it via /auth/forgot-password/reset?token=<forged_JWT>.
  4. The server accepts the token, queries the database for the user, and resets the password.

As the advisory notes, “verifyToken parses the payload using jwt.decode instead of jwt.verify (no signature or expiry checks).”

This vulnerability enables full account takeover if the attacker obtains a user’s ID string. Because Formbricks exposed both the email verification and password reset flows to this weakness, an attacker could effectively lock users out of their accounts by resetting credentials at will.

The advisory warns: “Knowing the victim’s actual user.id is enough to arbitrarily change their password.”

Formbricks users should immediately upgrade to version 4.0.1 or later. Until patching is complete, organizations should:

  • Restrict access to password reset endpoints.
  • Monitor for unusual password reset requests.
  • Rotate user credentials if compromise is suspected.

Related Posts:

  • Hacker forged Windows 11 upgrade website to trick users to download the virus
  • Account Takeover Vulnerability Found in Better Auth Library
  • UK Forges Strategic AI Alliance with OpenAI to Boost Infrastructure and Safety Research
  • Researcher releases a PoC for PHP RCE vulnerability
  • CISA Warns of Credential Risks Tied to Oracle Cloud Breach
Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • Mitel OpenScape 4000 Critical Command Injection Fixed in V11 R2.14
  • Fortinet Critical Alert: 9.1 Severity Flaws in FortiSandbox and FortiAuthenticator Risk Remote Takeover
  • Two RCE Vulnerabilities Found in Open-Source BI Tool DataEase
  • Critical Tapo C325WB Vulnerabilities Expose Smart Cameras
  • CVE-2025-41715 (CVSS 9.8): Unauthenticated Flaw Exposes WAGO Industrial Databases
  • ABB Patches Critical T-MAC Plus Terminal System Flaws
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Account Takeover Authentication Bypass CVE-2025-59934 Formbricks JWT open-source security vulnerability

Leave a Reply Cancel reply

You must be logged in to post a comment.

🚨 Active Exploits in the Wild

  • CVE-2026-123890CVSS 9.8
    VMware vCenter contains an authentication bypass vulnerability in the VMware Directory Service. Affected versions: 9.1.x (fixed in 9.1.1.0200);...
    Watchtower Verified📅 Updated: Nov 19, 2026
  • CVE-2026-114938CVSS 8.1
    Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java...
    Admin intel📅 Updated: Nov 19, 2026
  • CVE-2010-20126CVSS 5.1
    Virtual Keyboard plugin for SquirrelMail through 0.9.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20007CVSS 9.3
    ThinkPHP 2.0 through 2.2 and 3.0 Lite mode contains an eval injection vulnerability in the Dispatcher PATH_INFO parsing,...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20008CVSS 8.7
    openSIS 5.1 before 9.0 contains a local file inclusion vulnerability that allows authenticated users to include arbitrary files...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2026-119618CVSS 8.1
    Concurrent Execution using Shared Resource with Improper Synchronization vulnerability in Apache HTTP Server's mod_http2 in assign_headers() can lead...
    Admin intel📅 Updated: Nov 18, 2026
  • CVE-2024-10441CVSS 9.8
    Improper encoding or escaping of output vulnerability in the system plugin daemon in Synology BeeStation OS (BSM) before...
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-40217CVSS 8.8
    LiteLLM through 2026-04-08 allows remote attackers to execute arbitrary code via bytecode rewriting at the /guardrails/test_custom_code URI.
    CISA KEV📅 Added to KEV: Nov 18, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-124749CVSS 9.8
    pam-MySQL (libpam-mysql, src:pam-mysql) inverts PAM_DISALLOW_NULL_AUTHTOK at both pam_sm_authenticate call sites, so an application that asks PAM to refuse...
    📅 Updated: Nov 20, 2026
  • CVE-2026-120681CVSS 9.1
    The Mang Board plugin for WordPress is vulnerable to authorization bypass in all versions up to, and including,...
    📅 Updated: Nov 20, 2026
  • CVE-2026-53431CVSS 9.1
    Authentication Bypass by Capture-replay vulnerability in malach-it Boruta allows an attacker who has obtained a previously valid JWT...
    📅 Updated: Nov 20, 2026
  • CVE-2026-49757CVSS 9.2
    Authentication Bypass by Spoofing vulnerability in team-alembic AshAuthentication allows account takeover of local users via OAuth2/OIDC sign-in. AshAuthentication's...
    📅 Updated: Nov 20, 2026
  • CVE-2026-133501CVSS 9.4
    A security flaw has been discovered in Gladys Assistant up to 4.71.0. This impacts an unknown function of...
    📅 Updated: Nov 20, 2026
  • CVE-2026-97196CVSS 9.1
    Improper Validation of Unsafe Equivalence in Input vulnerability in Liquid Web / StellarWP GiveWP give allows Authentication Bypass.This...
    📅 Updated: Nov 20, 2026
  • CVE-2026-129056CVSS 9.8
    Incorrect Privilege Assignment vulnerability in Paul Ryan Authorizer authorizer allows Privilege Escalation.This issue affects Authorizer: from n/a before...
    📅 Updated: Nov 20, 2026
  • CVE-2026-133500CVSS 9.4
    A vulnerability was identified in Gladys Assistant up to 4.71.0. This affects an unknown function of the file...
    📅 Updated: Nov 20, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.