
 Do Son
Cursor AI editor found storing API keys and tokens in an unprotected SQLite database, allowing extensions to steal credentials silently. CVSS 8.2. No patch yet.
security vulnerability

Microsoft’s sudden suspension of VeraCrypt and WireGuard accounts reveals the dangers of automated bureaucracy in the critical path of security software.

Hobby coder Sammy Azdoufal used Claude Code to mod his DJI Romo vacuum and accidentally gained control of 7,000 units. Is your smart home watching you?

New flaws found in React Server Components risk a Server-Crashing DoS (CVSS 7.5) via infinite loop and Source Code Disclosure (CVE-2025-55183). Update to v19.0.3/19.1.4/19.2.3 immediately.

A critical flaw (CVE-2025-10725) in Red Hat OpenShift AI allows low-privileged users to escalate to full cluster admin privileges, risking complete platform compromise.
A public PoC has been released for CVE-2025-24085, a zero-day flaw in Apple's Core Media framework that allows a malicious app to elevate its privileges. Update now.
Formbricks has a critical auth flaw (CVSS 9.4) in its JWT validation. Attackers can forge tokens to reset user passwords and achieve full account takeover.

Apache Airflow 3.0.3 has a bug (CVE-2025-54831) exposing sensitive connection details, including passwords, to all users with only READ permissions. Update immediately.

A year after its discovery, the XZ backdoor remains in multiple Docker Hub images, posing a risk to developers and the software supply chain.

Zoom has released security updates addressing two significant vulnerabilities in its Windows-based clients—CVE-2025-49456 and CVE-2025-49457—that could enable...

Critical FortiSIEM flaw (CVE-2025-25256) allows remote unauthenticated command injection. Exploit code active in the wild—patch immediately.

Two Windows Kernel vulnerabilities allow SYSTEM-level privilege escalation. PoC exploit code is publicly available.

A patched Google flaw allowed researchers to extract linked phone numbers without user notification. The vulnerability is now fixed, and no exploits were detected.

Go 1.24.4 and 1.23.10 fix flaws in net/http, os, and crypto/x509, addressing data leaks, file inconsistencies, and certificate validation bypasses. Update now!

Symantec found over 21 million Chrome extension users at risk due to hardcoded API keys and secrets, potentially leading to data manipulation and financial loss.

A study reveals widespread path traversal (CWE-22) in open-source projects, exacerbated by LLMs generating insecure code. Automated detection and patching are critical.
A WordPress vulnerability puts private information at risk for nearly a billion websites. Can your site's draft titles be stolen?
ARMO researchers reveal how io_uring blinds Linux security tools like Falco, Tetragon, and Defender, exposing systems to undetected rootkit attacks.

A critical vulnerability in Bubble.io allows attackers to bypass restrictions and extract all user data from Elasticsearch. The flaw remains unpatched.

Hitachi Vantara addresses a critical resource injection vulnerability (CVE-2025-0756) in Pentaho Data Integration & Analytics, enabling RCE.
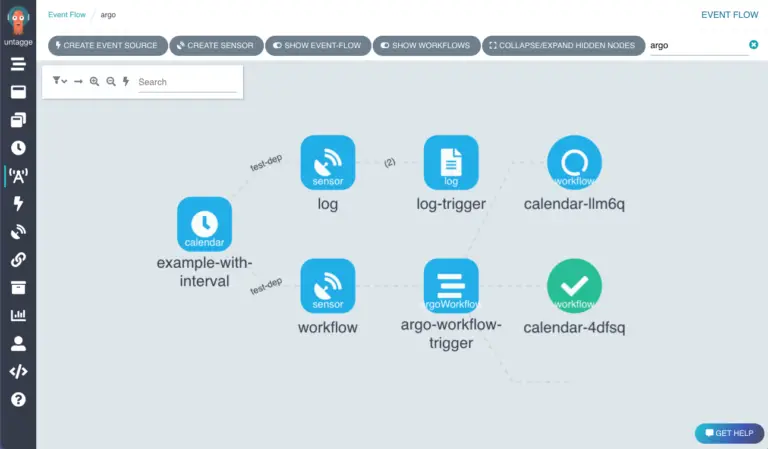
A critical vulnerability (CVE-2025-32445) in Argo Events allows users to gain privileged access to Kubernetes clusters. Upgrade to v1.9.6 to patch.

A critical vulnerability (CVE-2025-3248) in Langflow allows unauthenticated remote attackers to fully compromise servers. Users are urged to upgrade to version 1.3.0 or restrict network access