
 Do Son
Discover critical Gitea security flaws exposing servers to account takeovers and SSRF attacks. Read about CVE-2026-20896 and CVE-2026-22874 patches today.
Authentication Bypass

Three Webmin vulnerabilities, including a critical authentication bypass (CVE-2026-56020), expose servers. Update to Webmin 2.641 to stay safe.

A 27-year-old OpenBSD authentication bypass (CVE-2026-55706) is now public, with full details and a working PoC exploit for the PPP PAP flaw.
A critical LiteLLM authentication bypass (CVE-2026-49468) lets crafted Host Header Injection reach protected AI Gateway routes. Patch in 1.84.0.

Rockwell Automation vulnerabilities affect FactoryTalk Historian and FLEX I/O adapters, including a critical unauthenticated password-change flaw.

A critical Apache Shiro LDAP Injection vulnerability in DefaultLdapRealm, CVE-2026-49268, allows authentication bypass. Update your framework immediately.

A Cloud Foundry UAA vulnerability (CVE-2026-41005) enables SAML authentication bypass, letting attackers forge trusted assertions. Upgrade now.

A critical phpBB authentication bypass (CVE-2026-48611) lets attackers hijack any account on thousands of forums. Update to 3.3.17 now.
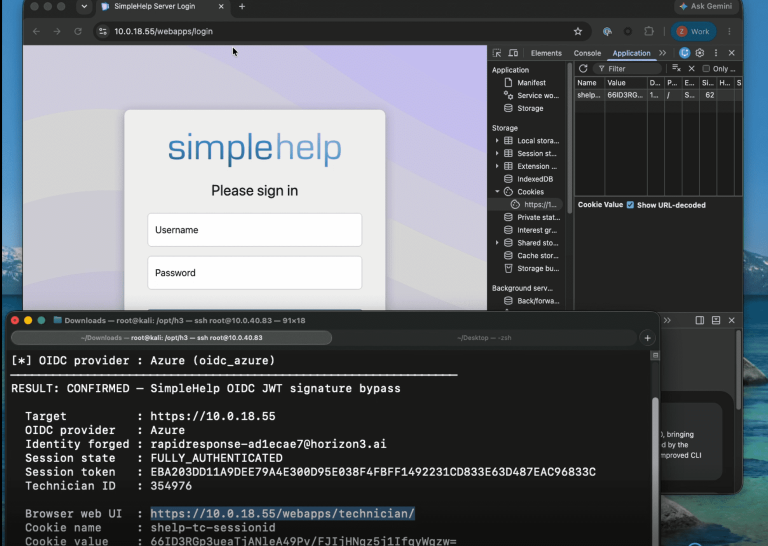
A critical SimpleHelp authentication bypass flaw leaves servers open. Attackers exploit the OIDC authentication flow to gain technician control.
A critical UpdraftPlus CVE-2026-10795 vulnerability threatens 3 million sites. Hackers are exploiting this UpdraftPlus authentication bypass in the wild.
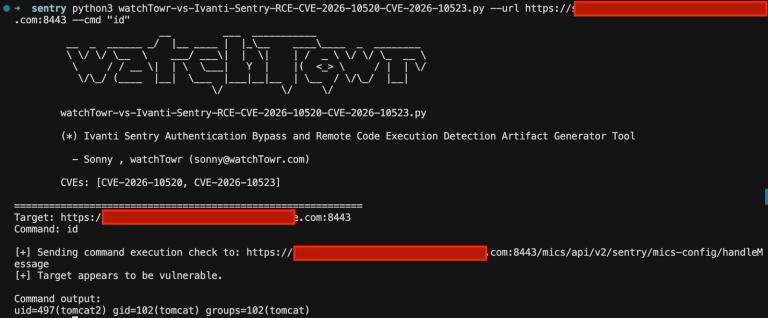
Critical Ivanti Sentry RCE details and a publicly disclosed PoC exploit are out. Patch the CVSS 10 and 9.9 flaws immediately to secure your network.

New updates address multiple Spring framework security vulnerabilities, resolving a critical authentication bypass threat and several denial of service bugs.

A critical Check Point VPN vulnerability is actively exploited in the wild, allowing unauthenticated attackers to bypass user login requirements.
Severe IBM WebSphere execution flaws expose servers to RCE. Apply the new WebSphere security bulletin patches immediately to secure your network.
Fix the critical SystemLink authentication bypass today. This severe privilege escalation bug allows unauthenticated attackers to steal enterprise dashboard data.

A high-severity Apache Solr default credentials vulnerability is exposed. Learn the critical CVE-2026-44825 workaround to secure your clusters.

Critical Casdoor authentication bypass flaws allow cross organization privilege escalation. Learn how to secure your identity infrastructure today.
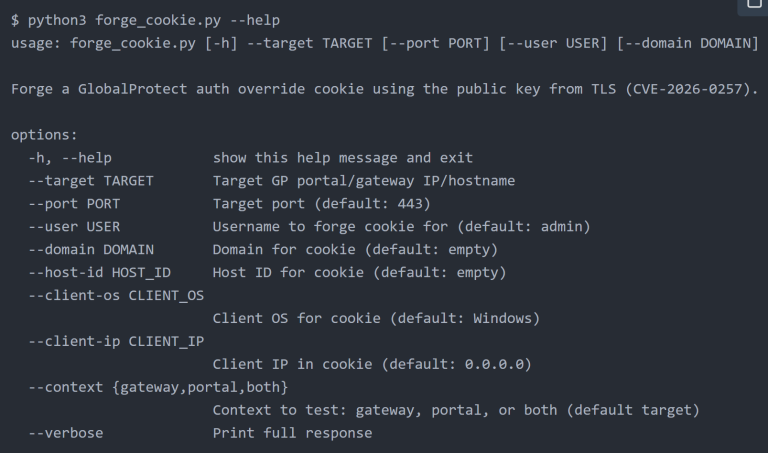
The PAN-OS authentication bypass flaw is actively exploited in the wild. Learn how to secure your GlobalProtect VPN gateways today.
IBM patched a critical IBM Jazz Foundation vulnerability (CVE-2026-3660) with a 9.8 CVSS score. Learn how to secure your property files now.

Apache OFBiz releases version 24.09.06 to patch severe RCE flaws, token forgery, and a critical password-reset authentication bypass. Upgrade now!
ZKTeco patches a critical 9.1 CVSS flaw (CVE-2026-8598) in CCTV cameras leaking admin credentials without authentication. Upgrade your firmware now!
NVIDIA patches a critical 9.8 CVSS authentication bypass (CVE-2026-24207) in Triton Inference Server. Update to r26.03 to secure AI workloads!