 Do Son
Four Apache Impala vulnerabilities expose systems to remote code execution and authentication bypass. Upgrade to Impala 4.5.2 to secure your clusters now.
Authentication Bypass
Two critical Siemens vulnerabilities (CVE-2026-18963, CVE-2026-50093) allow account takeover and root access. See affected versions and fixes.
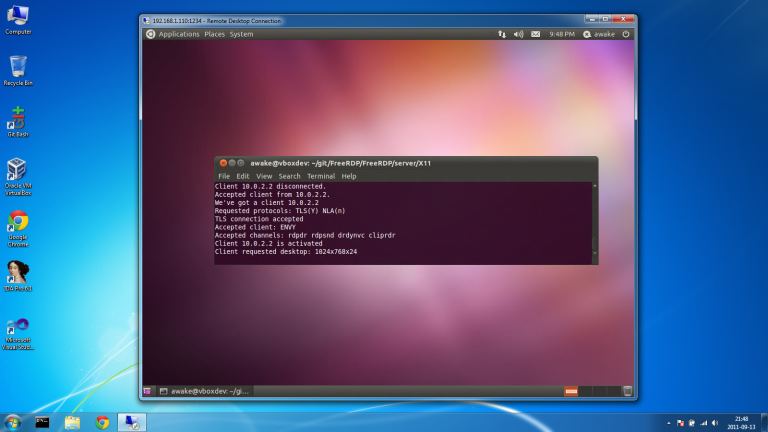
FreeRDP 3.31.0 patches 5 server-role flaws, including a pre-auth remote code execution chain affecting GNOME Remote Desktop and KDE krdp.
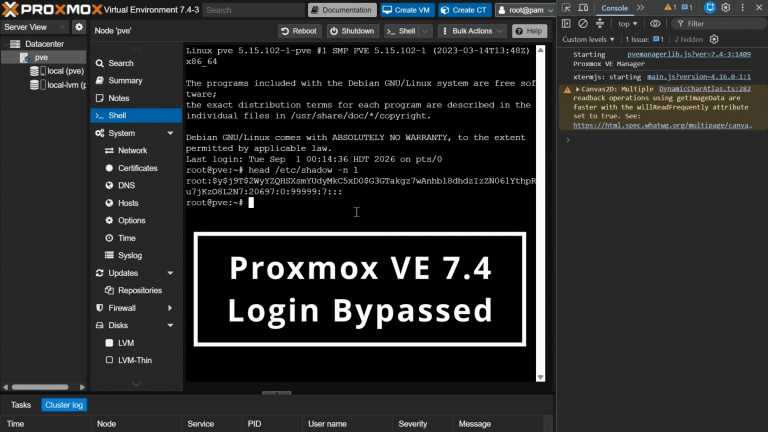
A public PoC now targets a Proxmox VE authentication bypass in EOL 7.x releases, and the pre-auth flaw is exploited in the wild for root access.
A critical Artifactory authentication bypass flaw (CVE-2026-82329) is exploited in the wild, letting attackers obtain administrative privileges.
Apache Tomcat fixed 11 vulnerabilities on August 25, 2026, including auth bypass (CVE-2026-68569) and HTTP/2 DoS flaws. Update to 11.0.25 now.
CISA warns of 11 Ebyte NE2-D11 vulnerabilities, four rated 9.8, that allow full device takeover. No patch is confirmed available yet.
Five RDK-B WebUI vulnerabilities let attackers bypass authentication and gain admin access on broadband gateways. No patch is available yet.
CVE-2026-20315 & CVE-2026-20317: Cisco Secure Workload Auth Bypass, Privilege Escalation Hit CVSS 10

CVE-2026-20315 & CVE-2026-20317: Cisco Secure Workload Auth Bypass, Privilege Escalation Hit CVSS 10
Cisco patches Secure Workload flaws CVE-2026-20315 and CVE-2026-20317, an authentication bypass and privilege escalation pair scoring CVSS 10. Upgrade now.

CVE-2026-19490 (CVSS 9.3) is a critical NetScaler authentication bypass in NetScaler Gateway and ADC. Patch now to block unauthenticated access.

IBM patches an IBM Db2 Mirror RCE flaw, CVE-2026-17186, rated CVSS 9.9, plus 17 more bugs in Db2 Mirror for i. Patch now.

CVE-2026-15826 (CVSS 9.8) is a User Profile Builder vulnerability letting attackers log in as WordPress admin. Over 40,000 sites affected; update to 3.16.5

TP-Link patched 5 TP-Link router vulnerabilities in ISP-managed mesh, router, and modem lines, including auth bypass and command injection.

CVE-2026-63455 and CVE-2026-63456 let attackers bypass web authentication on HPE EdgeConnect Orchestrator. CVSS 9.8. Patch now.

PoC exploit code is public for CVE-2026-61515, an unauthenticated command injection in Puwell IP Camera firmware. CVSS 9.3. Details inside.

Rapid7 published full details and a PoC for CVE-2026-55040, a critical SharePoint authentication bypass that forges JWT tokens. Patch now.

Progress patched 10 MarkLogic Server vulnerabilities, including auth bypass and privilege escalation flaws rated up to CVSS 9.9. Details inside.

CVE-2026-5423 is a Neo4j GraphQL authentication bypass letting unauthenticated clients forge JWT claims and read subscription data.

WSO2 patched four critical account takeover flaws, including CVE-2026-5430 at CVSS 10 via JWT auth bypass. Details and fixes inside.

CVE-2026-18577 is being exploited in the wild for N-central account takeover. An incomplete patch let attackers gain admin access. Update to 2026.3.1.7.

CVE-2026-18574 is a Check Point authentication bypass rated CVSS 9.3, letting attackers run commands as admin. Patch via the latest Jumbo Hotfix.
The Arris BGW210-700 vulnerability, CVE-2026-16771, is an authentication bypass in AT&T's gateway. A LAN user can read the WiFi password.