 Do Son
A SolarWinds Web Help Desk SAML authentication bypass, CVE-2026-28323, scores a critical CVSS 9.8. Update to 2026.2.1 to stay protected.
Authentication Bypass
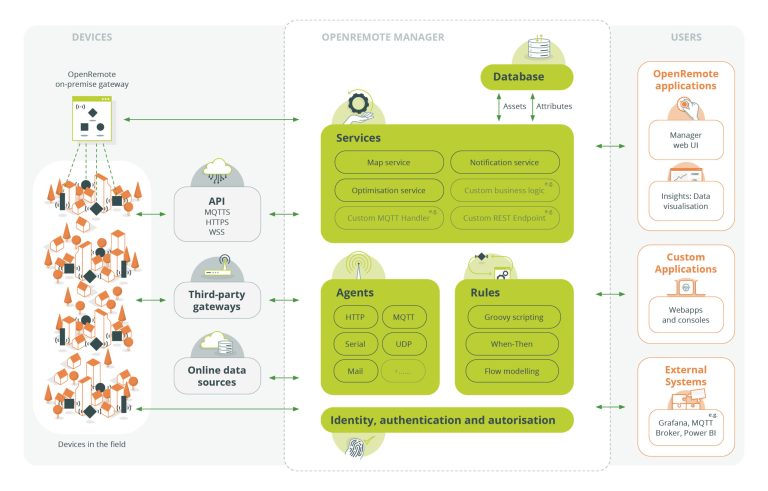
An OpenRemote vulnerability, CVE-2026-66013 (CVSS 9.3), enables unauthenticated asset takeover. Full advisory details are now public. Patch to 1.26.2.

CVE-2026-16232 is a SmartConsole authentication bypass in Check Point Security Management. Exploited in the wild, with a public PoC now available.

A Konnectivity vulnerability (CVE-2026-16242, CVSS 9.4) lets unauthenticated attackers proxy and modify control-plane traffic. See the fix and mitigation.
CVE-2026-61884 is a Tycon authentication bypass rated CVSS 9.8 in TPDIN-Monitor-WEB2. No vendor fix exists, so isolate the devices now.

ManageEngine fixed an ADAudit Plus vulnerability, CVE-2026-6516, a CVSS 10 unauthenticated remote code execution flaw. Update to build 8606 now.

Check Point confirms CVE-2026-16232, a SmartConsole authentication bypass, is exploited in the wild. Apply the July 22 jumbo hotfix now.
Arctic Wolf links Qilin ransomware attacks to CVE-2026-0257, a Palo Alto GlobalProtect auth bypass used for initial access. Patch PAN-OS now.

Siemens Opcenter X authentication bypass (CVE-2026-56451, CVSS 10) lets attackers forge JWTs for full unauthorized access. Update to V2604 now.
VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch

VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch
VMware Avi Load Balancer patches CVE-2026-47865 (CVSS 9.8), a critical authentication bypass, plus six more flaws. Upgrade the Avi Controller now.
Three Apache IoTDB vulnerabilities include a critical path traversal (CVE-2026-24014) and an authentication bypass. Upgrade to 2.0.8 now.
Four Apache Camel vulnerabilities allow header injection, server-side request forgery, secret disclosure, and an authentication bypass. Patch to 4.21.0 now.
A Kafka authentication bypass lets attackers replay expired JWTs against 4.0.x brokers. The OAUTHBEARER path checks nbf but not exp. No fix yet.

APISIX authentication bypass CVE-2026-39999 lets attackers forge JWTs via algorithm confusion. APISIX 3.16.0 is affected; upgrade to 3.16.1.

A NetComm authentication bypass (CVE-2026-35019, CVSS 9.2) uses a hardcoded AES key to forge admin session cookies. Update to firmware R6B032 now.

JetBrains patched a CVSS 10 authentication bypass and two more flaws (CVE-2026-50242). Its tools reach 15M developers. Update JetBrains Hub now.

Seven Apache Tomcat vulnerabilities are patched, including an authentication bypass (CVE-2026-55957). Update to a fixed Tomcat release now.

WSO2 patched seven flaws across API Manager and gateways, led by a CVSS 10 JWT auth bypass (CVE-2026-5430). Update WSO2 API Manager now.
CVE-2026-48558, a SimpleHelp authentication bypass, is exploited in the wild to deploy TaskWeaver and Djinn Stealer. CISA added it to KEV. Patch now.

Python fixed a python.org authentication bypass in its release metadata API. The flaw, dormant since 2014, let attackers alter download URLs.

A critical Langflow RCE vulnerability (CVE-2026-10561) scores CVSS 10 and enables unauthenticated remote code execution. Upgrade to 1.9.4 now.