
 Do Son
Fortinet issues a critical 9.1 CVSS alert for FortiSandbox. Unauthenticated auth bypass and command injection risks. Patch to 5.0.6 or 4.4.9 immediately.
Authentication Bypass

OpenStack Keystone vulnerability allows disabled LDAP users to authenticate. Logic flaw in attribute mapping affects releases up to 2026.1. Patch now!
LiteLLM patches critical 9.4 CVSS flaws, including OIDC cache collisions and pass-the-hash attacks. Secure your AI infrastructure—upgrade to v1.83.0 now!
Laravel Passport patches a 7.1 CVSS authentication bypass where machine tokens masquerade as human users. Protect your app—upgrade to v13.7.1 now!

IBM patches critical flaws in Verify Identity Access, including a 9.3 CVSS root escalation and 8.1 auth bypass. Secure your identity gateway—update now!

CVE-2026-34950: A critical 9.1 CVSS flaw in fast-jwt allows authentication bypass via leading whitespace. Learn how a regex error leads to algorithm confusion.

TP-Link warns of high-severity flaws (CVSS 8.7) in Tapo C520WS cameras. Attackers can bypass auth or blind your security. Update to firmware 1.2.4 now!

CISA alerts to a 9.8 CVSS flaw in Anritsu Spectrum Monitors (CVE-2026-3356). No patch is coming for this authentication bypass. Secure your network now!

Cisco patches a critical 9.8 CVSS flaw (CVE-2026-20093) in IMC. Unauthenticated attackers can change admin passwords and seize full control. Update now!

MantisBT patches a critical 9.3 CVSS auth bypass (CVE-2026-30849) and high-severity XSS flaws. Learn how MySQL type conversion opens the door. Update now!
Two high-severity flaws (CVE-2026-22731 & CVE-2026-22733) in Spring Boot Actuators allow authentication bypass. Update your framework today to stay secure.

Arctic Wolf warns that hackers are actively exploiting a critical Quest KACE vulnerability (CVE-2025-32975) to completely take over enterprise networks.
A critical 9.8 CVSS vulnerability (CVE-2026-32136) in AdGuard Home lets unauthenticated attackers hijack network DNS settings. Update to v0.107.73 now.

HPE Aruba patches a critical 9.8 CVSS bypass in AOS-CX switches that allows unauthenticated password resets. Upgrade to 10.17.1001+ to secure your network now.
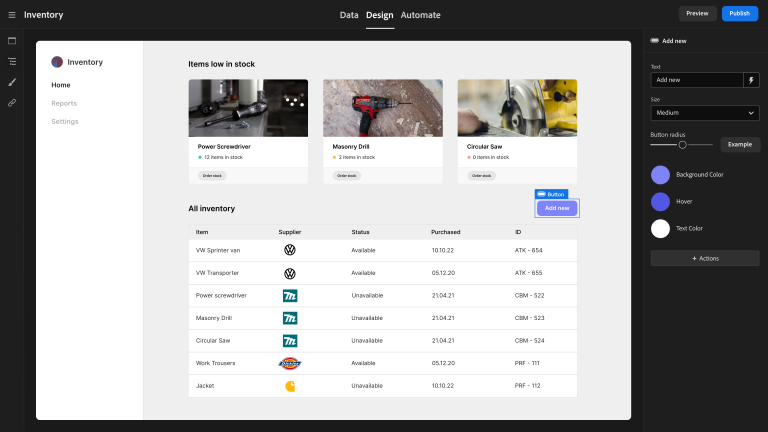
Two critical flaws in Budibase (CVE-2026-31816, CVE-2026-30240) allow unauthenticated API access and secret exfiltration via path traversal. Patch immediately.

A critical 9.8 CVSS authentication bypass (CVE-2026-0953) in Tutor LMS Pro is being actively exploited in the wild. Update to version 3.9.6 immediately.

A critical 10.0 CVSS flaw (CVE-2026-20127) in Cisco Catalyst SD-WAN is actively exploited in the wild. A public PoC is now available. Patch immediately!
A critical 10.0 CVSS flaw (CVE-2026-29000) in the pac4j-jwt library allows attackers to forge JWTs and bypass authentication. Patch immediately.

HPE warns of a critical CVSS 10.0 vulnerability (CVE-2026-23600) in AutoPass License Server. Remote attackers can bypass authentication. Patch to 9.19 now!

Cisco Talos warns of CVE-2026-20127, a CVSS 10 flaw in Catalyst SD-WAN exploited since 2023. UAT-8616 bypassed authentication to hijack global network fabrics.

CISA warns of critical flaws in EOL USR-W610 IoT servers. CVE-2026-25715 allows full admin control via blank passwords. No patches planned; isolate now.