 Do Son
Quest KACE SMA CVE-2025-32975 (CVSS 10) exploited in the wild. Attackers bypass auth to seize admin control. Patch to version 14.1.101 or 14.0.341 now!
Authentication Bypass

ELECOM routers hit by critical 9.8 CVSS flaws (CVE-2026-42062). Unauthenticated attackers can execute OS commands and bypass auth. Update firmware now!

200,000+ sites hit by CVE-2026-8181. A 9.8 CVSS Burst Statistics flaw allows RCE via auth bypass. 5,000+ attacks blocked. Update to 3.4.2 immediately!
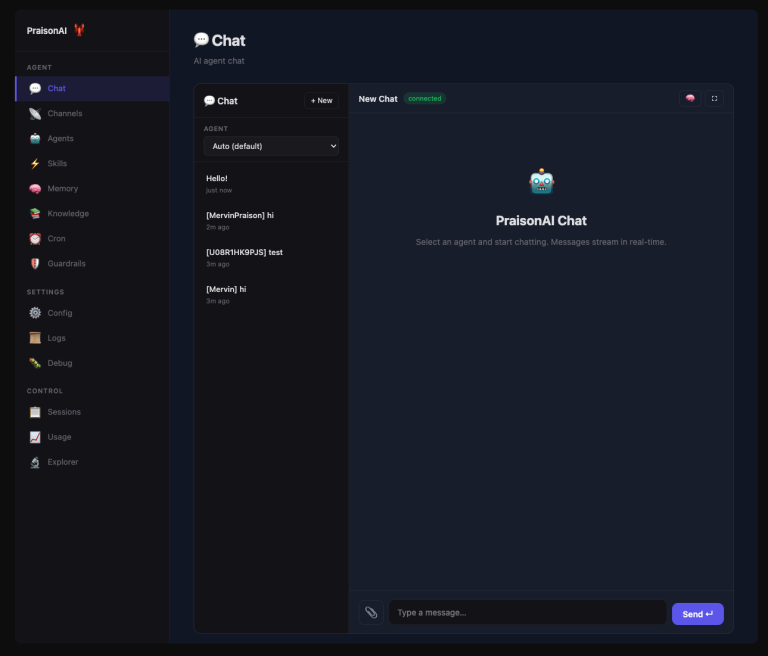
Sysdig warns: PraisonAI (CVE-2026-44338) exploited in under 4 hours. Attackers bypassed auth to hijack agents and drain API quotas. Update to 4.6.34 now!
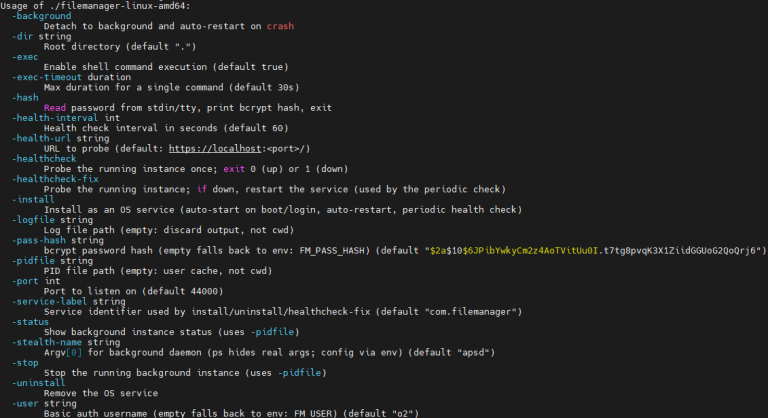
Urgent: cPanel & WHM hit by global 9.8 CVSS auth bypass. Over 2,000 IPs are actively hijacking servers for data theft and ransomware. Patch immediately!

Kaspersky reports a record surge in CVEs for Q1 2026. Discover how AI-driven exploits, authentication bypasses, and new C2 trends are reshaping cyber defense.

A critical 9.1 CVSS flaw in a Go auth library causes a Patreon "identity collision," merging all users into one account. Upgrade to v2.1.2 immediately!

MOVEit Automation faces a critical 9.8 CVSS flaw (CVE-2026-4670). Attackers can bypass auth to seize admin control and expose data. Patch immediately.

Snyk warns of active in-the-wild exploitation of the Qinglong platform. Two authentication bypass flaws grant attackers RCE to deploy .fullgc cryptominers.
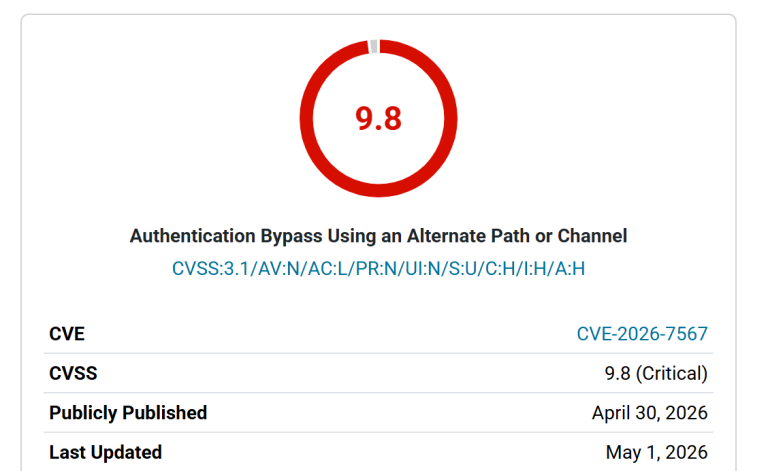
A critical 9.8 CVSS vulnerability in the Temporary Login plugin puts 40,000+ WordPress sites at risk of account takeover. Patch to version 1.1.0 now!
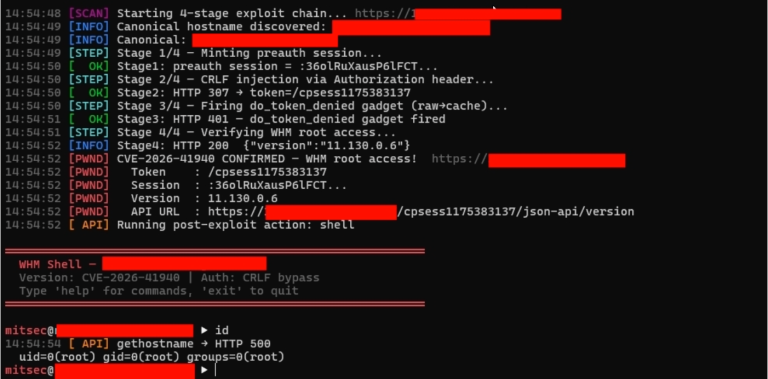
CISA warns of cPanel CVE-2026-41940 (CVSS 9.8). 44,000 IPs compromised via authentication bypass, fueling ransomware and botnets. Patch by May 3rd!
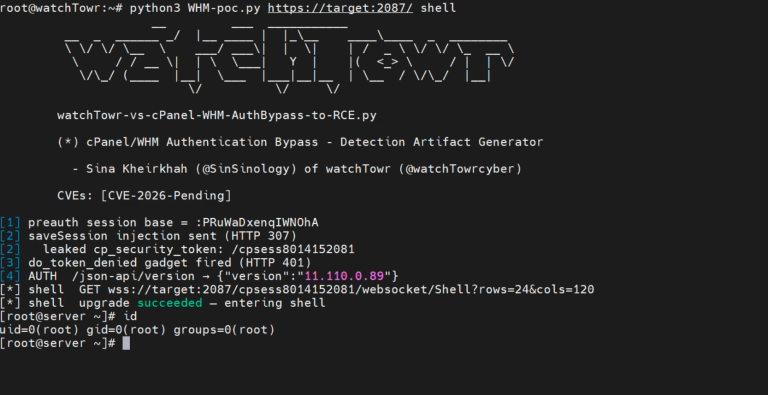
cPanel issues emergency patches for a critical authentication vulnerability affecting all supported versions. Run /scripts/upcp --force immediately to patch.

Critical 9.0 CVSS RCE in Nginx UI (CVE-2026-42238) exploits a 10-minute unauthenticated window. Attackers can seize root control. Patch to the latest version now.

Carlson VASCO-B GNSS receivers face a critical 9.4 CVSS flaw with zero authentication. Stop remote attackers from drifting your location data. Update to v1.4.0.

Critical 9.8 CVSS flaw (CVE-2026-6074) in Intrado 911 Gateway allows unauthenticated access to management tools. Protect emergency services and patch today.

Critical 9.8 CVSS auth bypass hits Xiongmai IP cameras. Public PoC is live with NO patch available. Secure your live feeds and isolate your devices now!
Microsoft's OOB update for .NET 10 (CVE-2026-40372) hits Linux/macOS users. Authentication is at risk. Stop the bypass and rotate your keys today.

Clerk reveals a critical 9.1 CVSS flaw in createRouteMatcher. Crafted requests can bypass middleware gating in Next.js, Nuxt, and Astro. Patch your apps now!
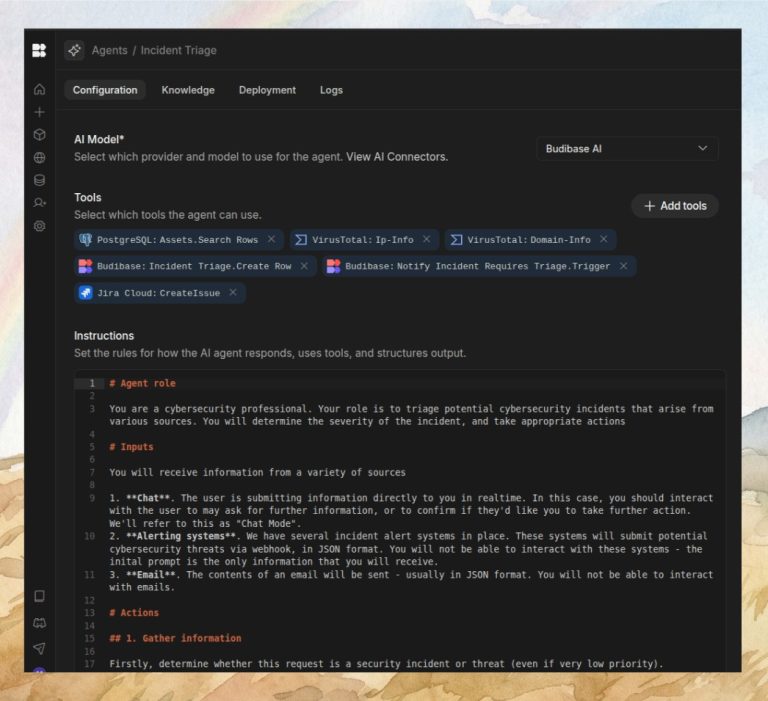
A critical 9.1 CVSS flaw in Budibase lets attackers bypass auth via unanchored regex. Protect your user database—update to version 3.35.4 immediately.

Apache Kafka faces a critical OAUTHBEARER bypass (CVE-2026-33557) and sensitive logging leaks. Secure your data pipelines—patch to v4.1.2 or v4.2.0 today.

A critical 9.1 CVSS flaw in OAuth2 Proxy allows unauthenticated users to bypass security via User-Agent spoofing. Secure your upstream apps—patch v7.15.2 today.
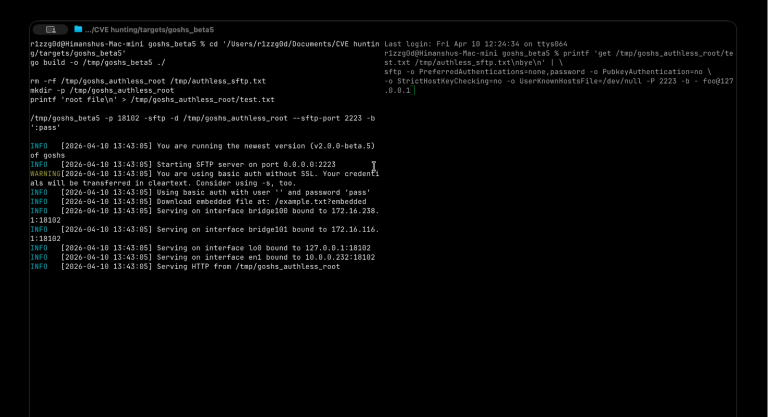
Critical 9.8 flaw in goshs (CVE-2026-40884) allows unauthenticated SFTP access when using specific auth syntax. Secure your files—upgrade to v2.0.0-beta.6 now!