 Do Son
OpenMage fixes 34 OpenMage vulnerabilities in Magento LTS, including a critical CSRF flaw that hands out API tokens. Upgrade to 20.19.0 or 20.18.2.
OAuth
Security researchers uncovered a new GhostCode phishing kit. Learn how the GhostCode phishing kit bypasses MFA to hijack enterprise Microsoft 365 accounts.

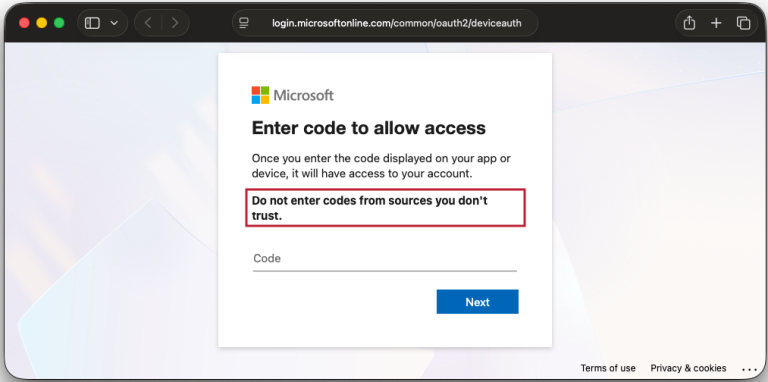
A new device code phishing campaign abuses Microsoft's OAuth flow to hijack Microsoft 365 accounts, no password stealing needed. How to spot it.

A critical phpBB authentication bypass (CVE-2026-48611) lets attackers hijack any account on thousands of forums. Update to 3.3.17 now.

A critical 9.1 CVSS flaw in a Go auth library causes a Patreon "identity collision," merging all users into one account. Upgrade to v2.1.2 immediately!
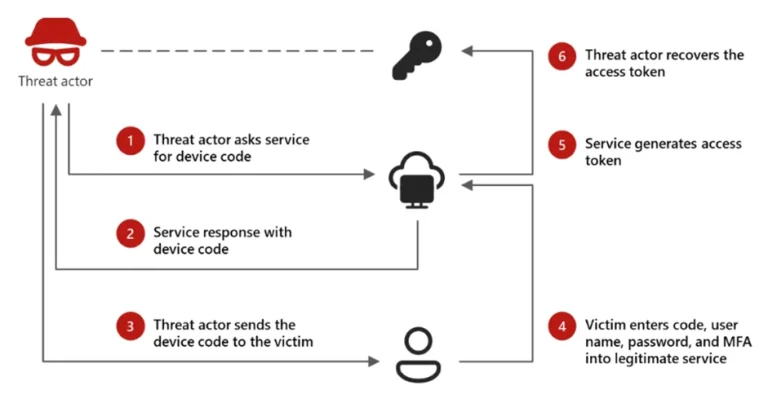
Microsoft uncovers EvilToken, an AI-powered PhaaS toolkit using Dynamic Device Code Generation to bypass MFA and breach high-value accounts. Patch now!

Three critical flaws in Authlib (including CVSS 9.1 CVE-2026-27962) allow JWT forgery and padding oracle attacks. Update to version 1.6.9 immediately.

A high-severity vulnerability (CVE-2025-9636) in pgAdmin could allow attackers to hijack OAuth flows, leading to account takeover and data breaches.

A new security advisory reveals two high-severity flaws in FreePBX, including a stored XSS and a shared OAuth key that could allow for API token forgery and admin compromise.

Cloudflare confirms it was hit by the Salesforce supply chain attack, exposing customer support data. The company is urging users to rotate credentials.

A new report reveals a dangerous misconfiguration: exposed appsettings.json files can contain Azure AD credentials, giving attackers full access to a company's cloud kingdom.

A new report reveals a widespread data theft campaign targeting Salesforce instances. Attackers used compromised OAuth tokens from a third-party app to steal data and credentials.

Proofpoint reveals an AiTM phishing campaign using fake OAuth apps and the Tycoon platform to bypass MFA, hijack Microsoft 365 accounts, and steal credentials.

A flaw (CVE-2025-4679) in Synology ABM leaked a static client_secret, allowing unauthenticated attackers read-only access to all Microsoft 365 tenants with ABM installed.

TeamFiltration is being actively exploited in UNK_SneakyStrike, targeting over 80,000 Microsoft Entra ID accounts with password spraying and data exfiltration.

Volexity uncovers Russian threat actors abusing Microsoft 365 OAuth flows via phishing, impersonation, and device registration to access email accounts.

Stay informed about the OAuth vulnerability that could put your website and users at risk. Understand the implications of this flaw and take steps to secure your website.