 Do Son
The Binance hack hit USD 6.34B via a fake job interview, an abused AI tool and EIP-7702 delegation. The FBI points to North Korea.
social engineering
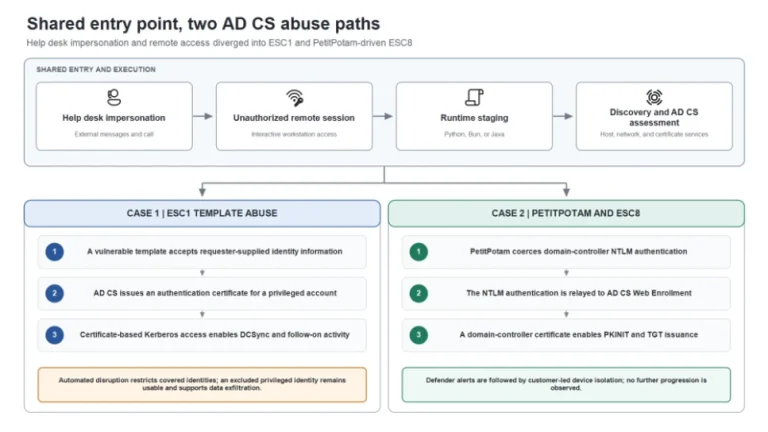
Microsoft details help desk impersonation on Teams that led to AD CS abuse via ESC1 and ESC8, giving attackers privileged certificates.
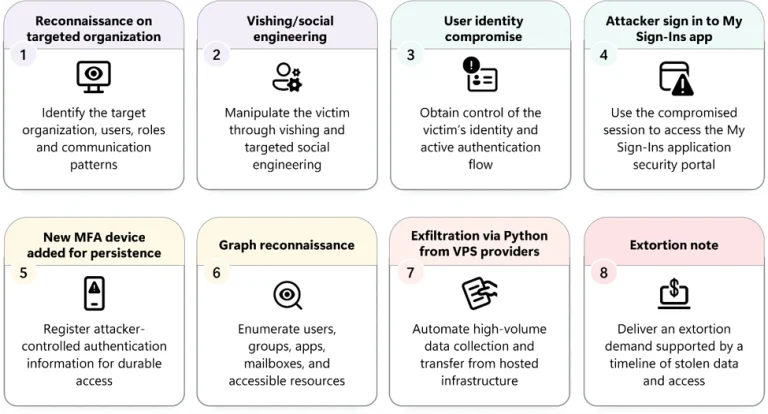
Microsoft warned of passkey social engineering attacks hitting tenants. Learn how passkey social engineering targets enterprise cloud identities.
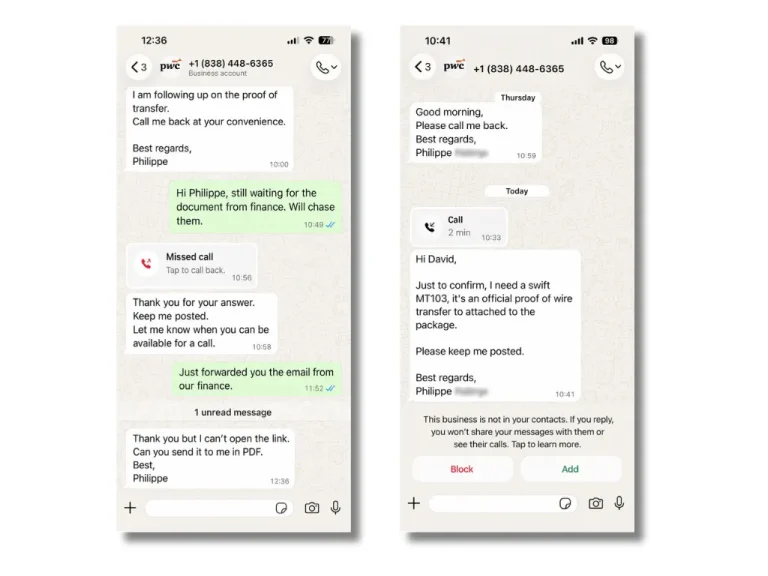
The Phantom Deal campaign uses fake acquisition documents to target executives. Gen exposed the Phantom Deal fraud after tracking bogus payment demands.
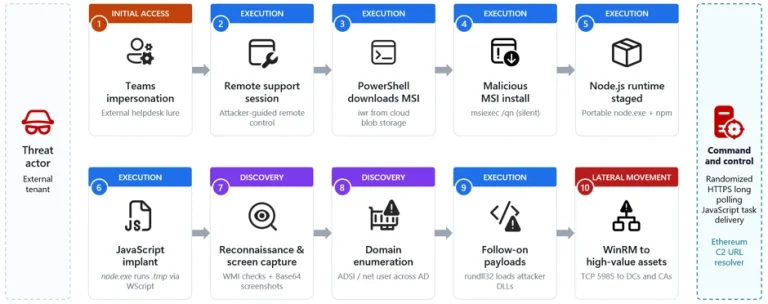
Microsoft Teams IT support impersonation lets attackers plant a Node.js implant and pivot to domain controllers over WinRM. See how to defend.
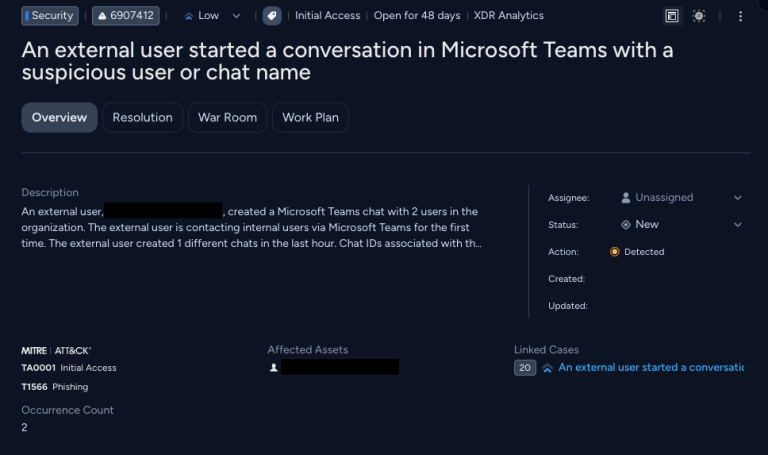
Discover how the Spring Ring vishing campaign uses Microsoft Teams phishing tactics to trick employees into installing malware and giving up remote access.

A Microsoft Teams vishing campaign tracked as STAC4749 hit dozens of North American firms and deployed Chaos ransomware in under 17 hours.

North Korea's ClickFake Interview campaign targets crypto pros with fake skill tests, dropping the PylangGhost RAT on Windows and GolangGhost on macOS.

The active DriveSurge threat cluster is compromising thousands of websites. Discover how its customized Traffic Distribution System redirects victims.
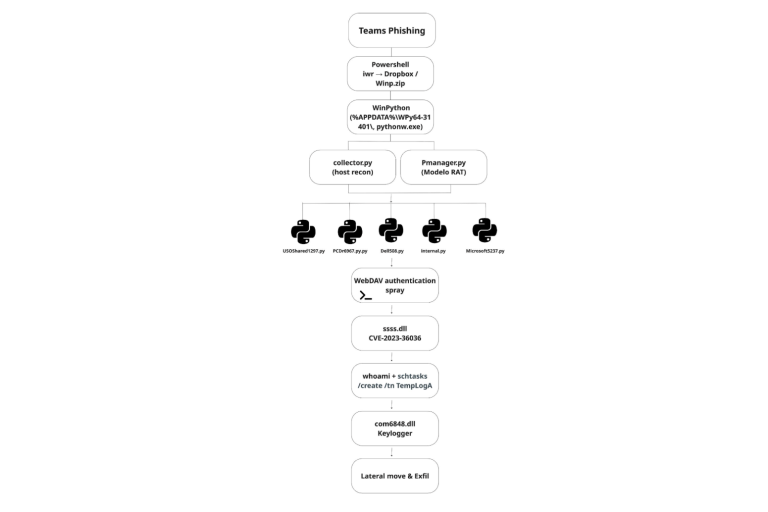
Rapid7 Labs exposes how attackers are abusing Microsoft Teams external access and Dumpit memory scrapers to breach corporate networks. Protect your team!
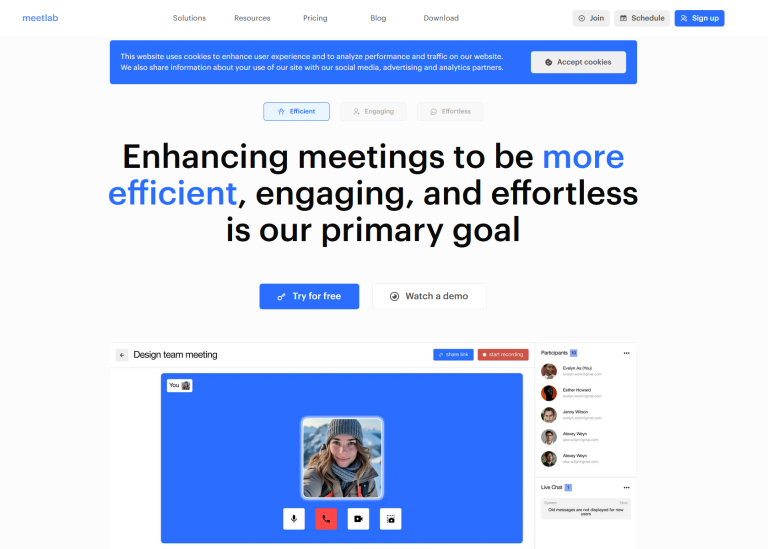
Job seekers beware: The JobStealer trojan poses as video meeting apps to hijack 300+ crypto wallets and Telegram data. Learn how to spot this 2026 threat.

Rapid7 unmasks Iranian APT MuddyWater using a Chaos ransomware "false flag" to hide state-sponsored espionage. See how they bypassed MFA via MS Teams.
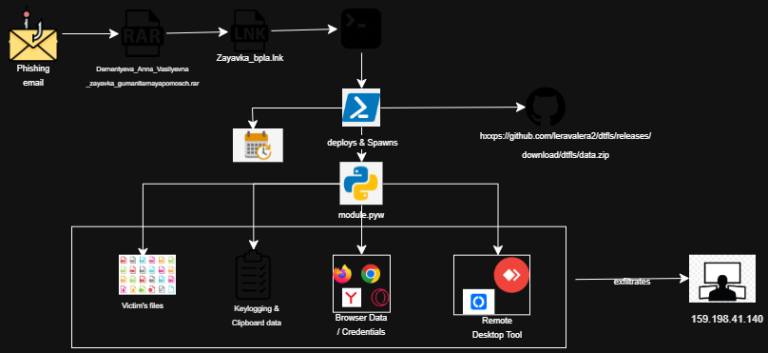
CRIL exposes a cyberespionage campaign using fake humanitarian aid forms to deploy fileless Python malware via GitHub for full-spectrum surveillance.
Securonix exposes an 80+ organization breach using "self-healing" RMM tools and Safe Mode persistence. Standard antivirus is blind—learn how to hunt it!
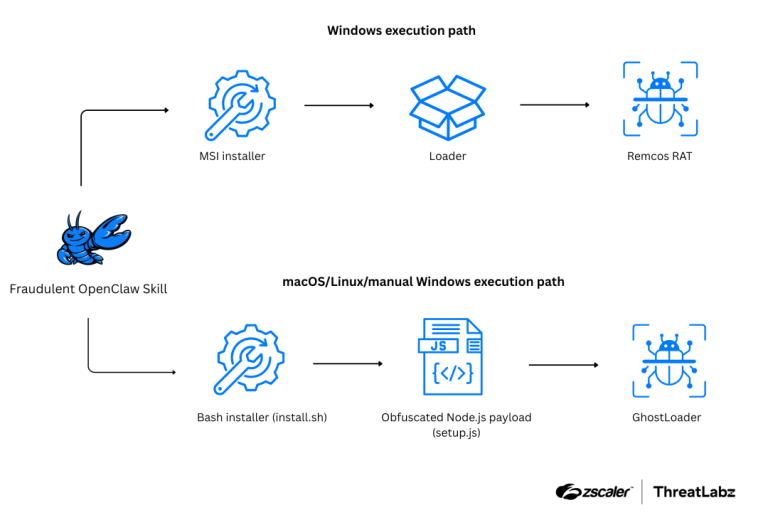
Zscaler ThreatLabz exposes DeepSeek-Claw, a malicious AI skill targeting the OpenClaw framework to deploy GhostLoader and Remcos RAT. Secure your agents now!

Google AppSheet is being abused by "AccountDumpling" to steal 30,000 Facebook accounts. Learn how this Vietnamese-linked group bypasses SPF/DKIM filters.

Varonis uncovers Bluekit, a new phishing-as-a-service kit using AI and 40+ templates to automate session hijacking and credential theft. See how it works.
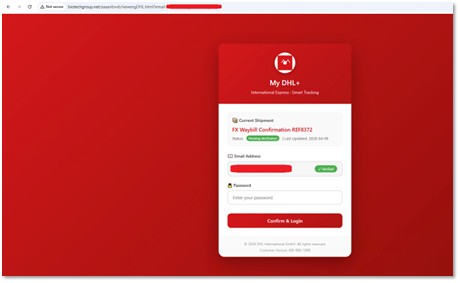
Forcepoint X-Labs uncovers a clever 11-step DHL phishing scam using a fake OTP interface to build trust and steal passwords. See how the trick works.

Citizen Lab reveals "Tall Tales," a PRC campaign using GLITTER CARP and SEQUIN CARP to hunt activists and ICIJ journalists via private contractors.

BlueNoroff uses a "self-reinforcing" deepfake pipeline to target crypto CEOs. Fake Zoom meetings and stolen footage lead to a 5-minute system compromise.
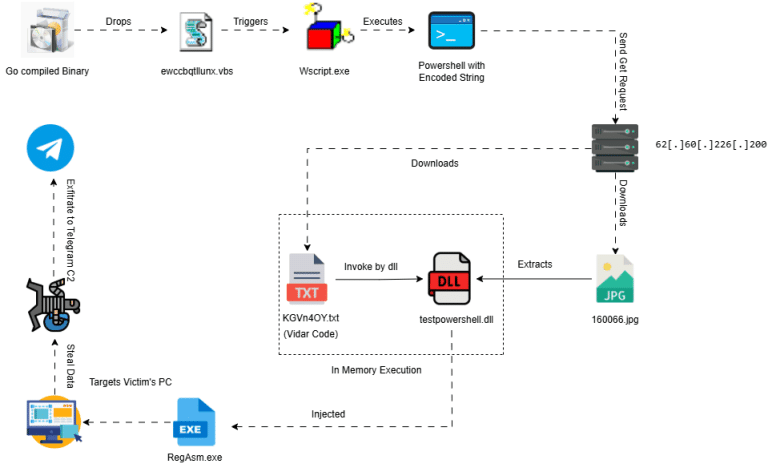
Vidar infostealer evolves into a fileless 2026 threat. From fake CAPTCHAs to "Claude Code" leaks, see how it steals crypto and passwords via Telegram C2.
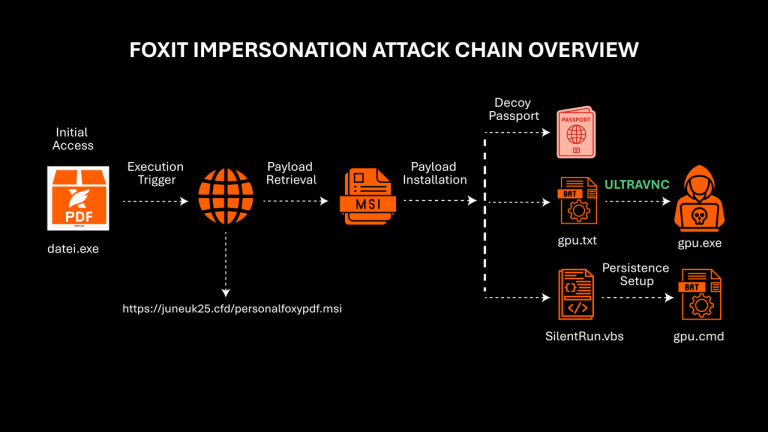
G DATA warns Foxit PDF users of a global malware campaign using fake installers and Danish passport decoys to deploy hidden UltraVNC remote access tools.