 Do Son
Cybercriminals are using fake DocuSign emails and the JWrapper framework to stealthily deploy SimpleHelp remote access tools. Learn how to spot the threat.
social engineering

North Korean hackers target IT pros with "Contagious Interview" malware. Fake job offers install trojanized MetaMask extensions to steal crypto.

Bridewell warns of Russian hackers targeting Booking.com. Phishing kits steal hotel staff creds to scam guests with "I Paid Twice" messages.

Hackers abuse Atlassian Jira notifications to bypass spam filters. Trend Micro warns of scams targeting enterprise users via trusted alerts.

Okta exposes North Korean IT workers using AI photos & stolen LinkedIn profiles to land remote jobs. Learn how "JJ" bypassed checks.
LevelBlue warns of StealC malware using "ClickFix" fake CAPTCHAs. Users are tricked into running fileless malware via PowerShell. Stay alert.

New "Matryoshka" Mac malware uses "ClickFix" scams to steal crypto. Intego warns of fake error fixes patching Ledger & Trezor apps. Stay alert.

LummaStealer is back, evading takedowns with "ClickFix" tactics. Bitdefender reveals how fake CAPTCHAs trick users into running malware. Stay alert.
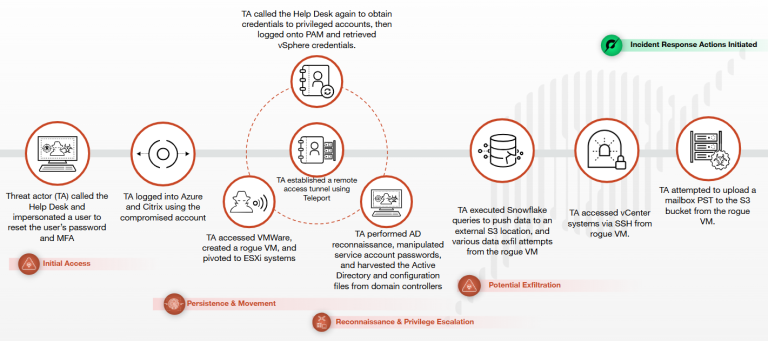
Unit 42 reveals Muddled Libra (Scattered Spider) uses rogue VMs in vSphere to persist. Learn how they bypass defenses without malware. Read more.

New Telegram phishing campaign abuses the "This is me" feature for account takeover. CYFIRMA reveals a global framework evading detection. Stay alert.
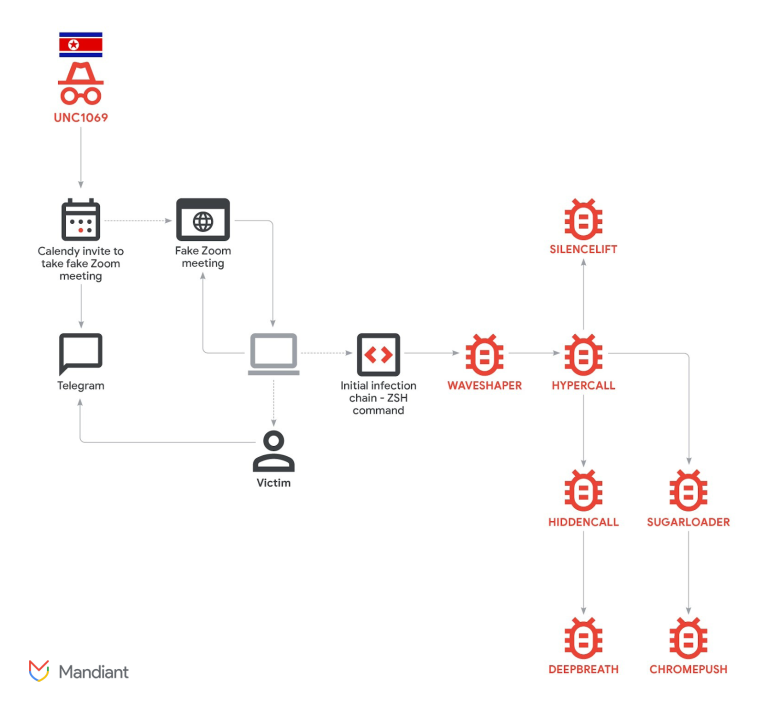
North Korean hackers (UNC1069) use AI deepfakes & "ClickFix" tactics to deploy SILENCELIFT malware. Learn how they target crypto firms via Zoom.

Hackers abuse PayPal & Apple to send "perfect" phishing emails. Learn how DKIM Replay attacks bypass security filters & DMARC checks.
Darktrace finds Mac malware using a fake "Compatibility Wizard" to trick users. The AppleScript attack bypasses TCC to drop a Node.js backdoor.

Stan Ghouls group targets Uzbekistan via fake court emails and malicious Java loaders. Learn how they deploy NetSupport RAT to spy on victims.

Rublevka Team's "scam-as-a-service" has stolen $10M+ in crypto. Their automated Solana drainers target Phantom & Solflare wallets. Don't be next.

Microsoft warns of "CrashFix": malicious extensions crash browsers to trick users into running a "fix" that installs a RAT. Beware fake ad blockers.

Sophisticated phishing abuses Vercel Blob & PDFs to bypass filters. Stolen credentials are exfiltrated via Telegram bots. Learn how to spot this attack.

BlueNoroff hackers use fake "audio issues" on Teams calls to trick macOS users. The "fix" runs terminal commands that steal Keychains. Watch out.
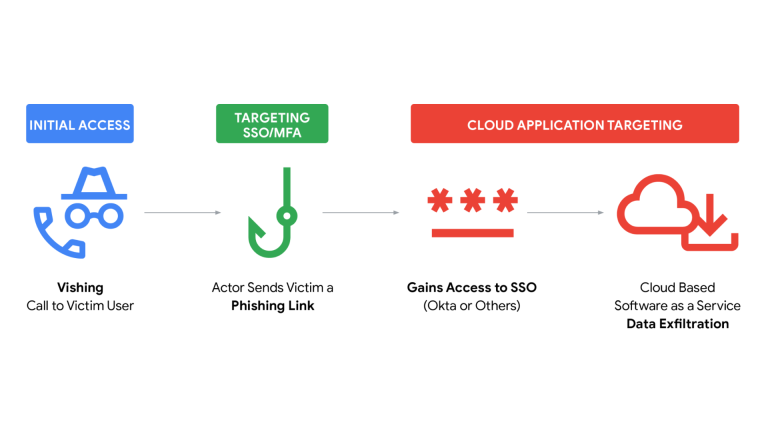
Mandiant warns of vishing rings like ShinyHunters impersonating IT support to bypass MFA and steal corporate cloud data. Verify your callers.

APT42 targets defense officials with "TAMECAT," a modular PowerShell backdoor. The malware uses social engineering and Telegram C2 to steal secrets.
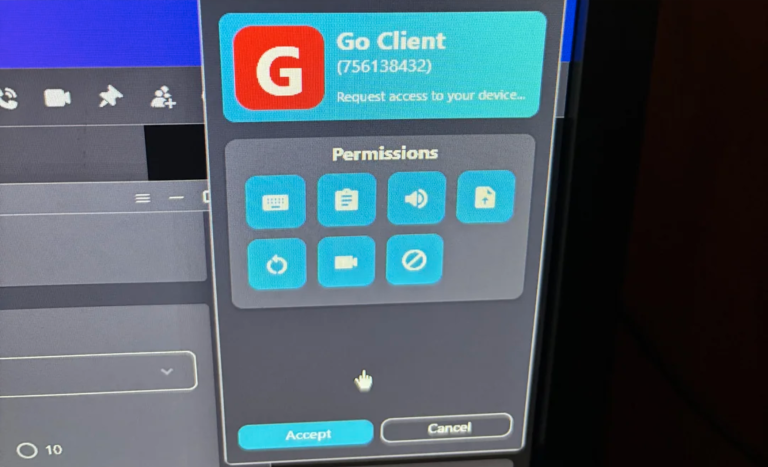
A massive botnet is targeting RustDesk users with fake "Go Client" connection requests. Learn how to lock down your ID and prevent unauthorized remote takeovers.

IClickFix malware hijacks 3,800+ WordPress sites with fake Cloudflare CAPTCHAs. This watering hole attack tricks users into running malicious PowerShell.