
 Do Son
"ConsentFix" phishing tricks users into pasting OAuth codes from Azure CLI, bypassing MFA and Conditional Access. Detect this "fix" scam now.
social engineering

New AI-generated malware campaign targets job seekers. Vietnamese actor "Huna" uses fake job offers to deliver PureRAT via Dropbox.

New Fake CAPTCHA campaign uses Google Calendar & steganography to drop Amatera Stealer. See how this attack exploits legitimate Windows tools to stay hidden.

Attackers exploit GitHub forks ("Repo Squatting") to push HijackLoader malware via official-looking URLs. Technique remains active; verify all downloads.

New ClearFake malware uses fake CAPTCHAs & "ClickFix" tactics to trick users into pasting malicious code. 150k victims infected via blockchain.
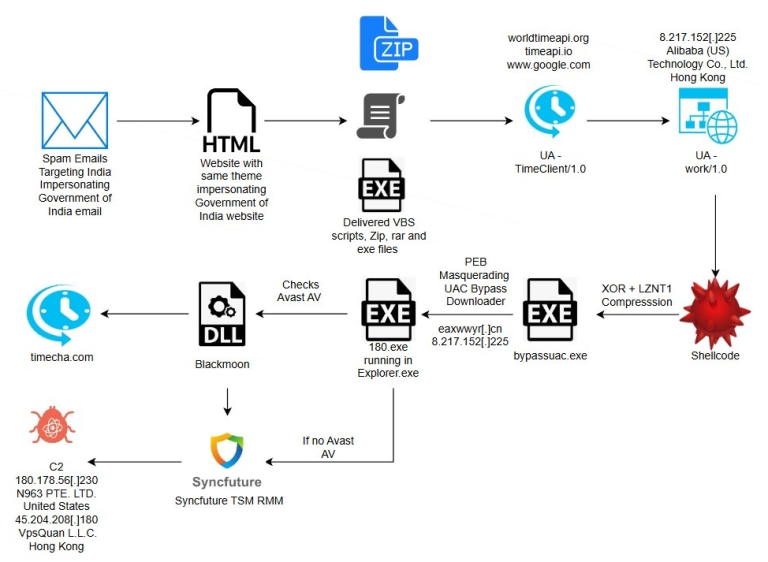
"SyncFuture" spies on Indian users via fake Income Tax emails. This advanced campaign bypasses antivirus & installs Chinese IT tools for total surveillance.

KONNI APT targets APAC developers with AI-generated malware disguised as crypto projects. The "polished" backdoor steals wallets & credentials.

Okta reveals new vishing kits that "drive" victim browsers. These real-time tools sync phone calls with phishing pages to bypass MFA number matching.

New macOS malware "MacSync" uses fake cloud installers & "ClickFix" terminal commands to steal crypto. It bypasses Gatekeeper to trojanize wallet apps.

Group-IB reveals a sophisticated loan phishing campaign in Peru. Scammers use the Luhn algorithm to validate stolen credit cards via fake ads.

Attackers abuse GitHub, Dropbox, and the "Defendnot" research tool to disable Windows Defender and deploy Amnesia RAT & ransomware in Russia.

New macOS malware "MonetaStealer" disguises itself as a Windows .exe to steal crypto & Keychain data. It currently has zero VirusTotal detection.

New malware campaign impersonates Malwarebytes installers. Hackers use DLL sideloading to deploy infostealers targeting crypto & MFA. Verify downloads now.

CloudSEK exposes "RedLineCyber," an impostor hijacking crypto clipboards on Discord. This stealthy malware drains wallets without a C2 server.

Trellix warns: "Browser-in-the-Browser" phishing creates perfect fake Facebook login pop-ups. Learn how this invisible trap steals credentials.
New Astaroth campaign "Boto Cor-de-Rosa" uses a Python worm to hijack WhatsApp Web. It auto-messages your contacts to spread banking malware globally.

New phishing campaign uses fake layoff warnings to drop Guloader and Remcos RAT. Learn how this HR-themed scam exploits workplace anxiety to steal data.

Attackers exploit complex mail routing to spoof "internal" emails using Tycoon2FA. Learn how to fix misconfigured DMARC policies and stop the breach.

PHALT#BLYX is a malware campaign using fake Booking.com alerts and BSOD screens to trick hotel staff into installing Russian-linked RATs.

Hyderabad police arrest another ex-Coinbase agent for selling user data. The TaskUs insider breach exposed 70k users and cost Coinbase up to $400 million.

North Korea's "Contagious Interview" campaign uses DriverFixer0428 to steal macOS credentials via fake prompts and Dropbox C2. Stay alert!

Genians exposes APT37's Artemis campaign, where hackers pose as Korean TV writers using fake casting calls to deliver malware via HWP documents.