 Do Son
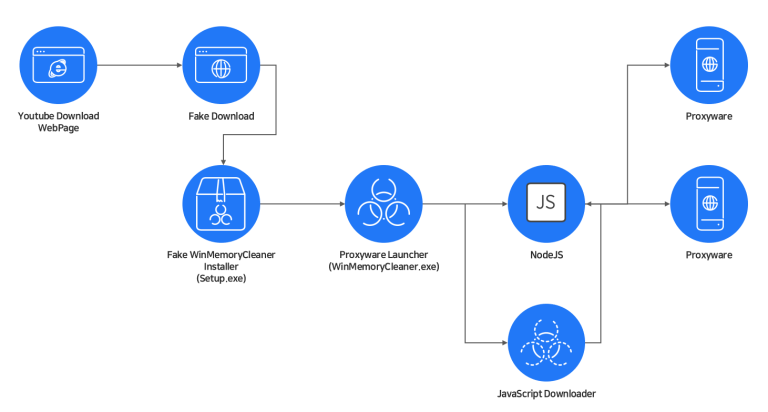
A new report reveals that malicious YouTube video downloader sites are tricking users into installing Proxyware, a type of malware that hijacks network bandwidth.
social engineering
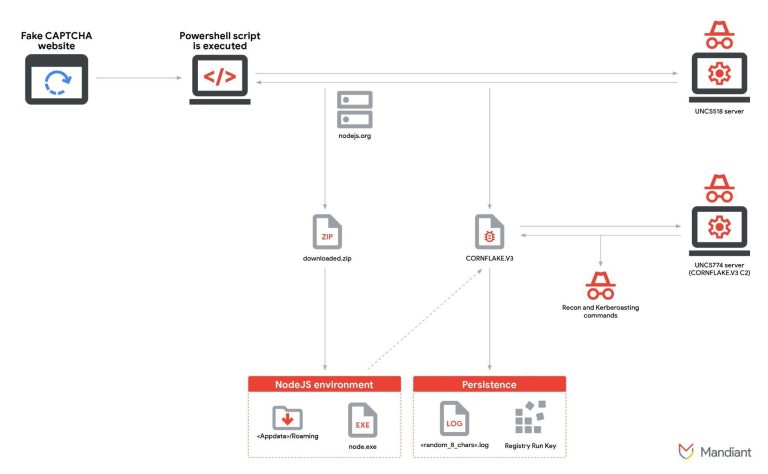
UNC5518 is using "ClickFix," a new technique that weaponizes fake CAPTCHAs to trick users into launching malware and providing access to other criminal groups.

A new report reveals a sophisticated spear-phishing campaign targeting finance executives. The attack uses social engineering and legitimate tools to evade detection.

A new report from Unit 42 reveals how cybercriminals are misusing generative AI to create realistic phishing sites, deepfake content, and fraudulent websites.
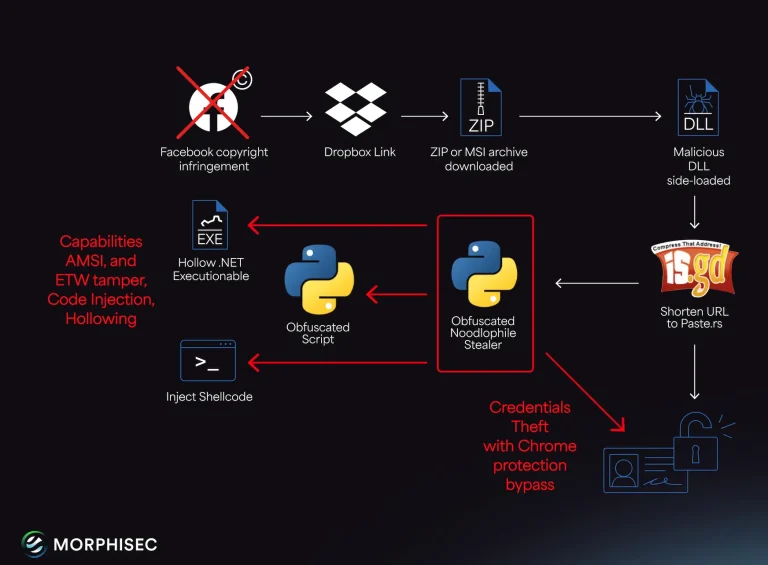
The Noodlophile infostealer has evolved from fake AI platforms to spear phishing, using fake copyright notices and DLL side-loading to target companies.
Phishing Scam Alert: McAfee Uncovers a New Android Campaign Impersonating a Government Solar Program

Phishing Scam Alert: McAfee Uncovers a New Android Campaign Impersonating a Government Solar Program
A new phishing campaign in India uses fake government solar subsidy websites to trick victims into downloading a malicious app that steals UPI PINs and other data.

A new report from Kaspersky warns that cybercriminals are now using AI, deepfakes, and sophisticated social engineering to create nearly undetectable scams.

A targeted phishing campaign against Israeli organizations uses a PowerShell-based RAT and compromised internal emails for delivery, making detection difficult.

A new large-scale malware campaign is using GitHub repositories disguised as game cheats and software cracks to distribute SmartLoader and steal user data.

Google confirms a June Salesforce breach by UNC6040 (ShinyHunters). The attack used social engineering to steal credentials, a tactic also used against Chanel and Allianz.

eSentire exposes Interlock, a new ransomware group using multi-stage payloads and the ClickFix social engineering technique to deploy ransomware and backdoors via compromised websites.

WithSecure uncovers a stealthy campaign using legitimate RMM tools embedded in PDFs to target European organizations, bypassing security with zero malware at initial entry.

A joint advisory from US, UK, Canada, and Australia warns of Scattered Spider's evolving tactics, now using DragonForce ransomware, spearphishing, SIM swapping, and MFA fatigue to compromise systems.

A new stealthy campaign uses Windows LNK files to deploy the REMCOS backdoor via multi-stage PowerShell commands, bypassing antivirus and gaining full system control.

Allianz Life confirms a data breach impacting over 1.4 million individuals after attackers used social engineering to access a cloud-based CRM system. ShinyHunters is suspected.

Unit 42 reveals homograph phishing attacks exploiting visually similar characters to bypass defenses and deceive users. AI is amplifying this threat, making malicious emails highly convincing.

Dropping Elephant is targeting Türkiye's defense industry, particularly missile manufacturers, with weaponized conference lures, VLC DLL sideloading, and custom shellcode for intelligence exfiltration.
Proofpoint reveals a surge in RFQ scams where fraudsters impersonate procurement officials to steal high-value goods by exploiting Net 15/30/45 financing terms.

LARVA-208 is targeting Web3 developers with fake AI platforms (like Norlax AI) and job lures to deploy Fickle Stealer malware, aiming to steal crypto and sensitive data.

Matanbuchus 3.0, a new sophisticated malware loader, is using social engineering via Microsoft Teams to infiltrate enterprise systems with advanced evasion tactics.

Evalian uncovers a phishing campaign spoofing Red Bull job offers using legitimate services, low-cost VPS, and "slow kill" tactics to steal credentials via fake Facebook logins.
Interlock RAT Gets PHP Makeover: New Variant Uses Steganography & ClickFix for Stealthy Infiltration

Interlock RAT Gets PHP Makeover: New Variant Uses Steganography & ClickFix for Stealthy Infiltration
The DFIR Report uncovers a new PHP-coded Interlock RAT variant, using compromised websites and ClickFix social engineering to deploy stealthy malware for recon and persistence.