
 Do Son
Google exposes a vast phishing campaign hijacking Booking.com reservation chats to steal credit card details from travelers, impacting thousands globally since Nov 2023.
social engineering

Darktrace uncovers a crypto scam using fake software startups (AI, gaming, Web3 themes) with professional online presences to distribute Electron malware (Windows) and Atomic Stealer (macOS) for crypto theft.

A malicious campaign on GitHub is distributing Lumma Stealer via fake "Free VPN for PC" and "Minecraft Skin Changer" repositories, using obfuscation and process injection for stealthy delivery.
Cybereason exposes a deceptive malware campaign using compromised WordPress sites and the "ClickFix" technique to deliver weaponized NetSupport Manager RAT clients for remote access.

North Korean APTs are using "NimDoor," a new Nim-based macOS malware, to target Web3/crypto startups via fake Zoom meetings, stealing browser, Keychain, and Telegram data with novel persistence.

Fortinet exposes a DCRat campaign impersonating a Colombian government agency, using obfuscated multi-stage infection, steganography, and AMSI bypass to deliver the RAT.

Nicholas Michael Kloster pleaded guilty to hacking organizations to promote his cybersecurity services, facing up to 5 years in prison for his illegal "self-promotion" tactics.

North Korean APT Kimsuky is evolving its ClickFix tactics, using deceptive social engineering, fake job portals, and obfuscated PowerShell to compromise targets via spear-phishing campaigns.

North Korean APTs are using 35 typosquatted npm packages and fake job offers to spread HexEval, BeaverTail, and InvisibleFerret malware, stealing crypto and data from developers.

Taiwan's BitoPro exchange confirms North Korea's Lazarus Group stole $11.5M in crypto via phishing an employee and bypassing MFA on AWS infrastructure.

Hackers are weaponizing legitimately signed ConnectWise ScreenConnect installers by using Authenticode stuffing to deploy malware and fake updates, leveraging social engineering.

CoinMarketCap suffered a client-side attack on June 20, 2025, using a fake "doodle" graphic to deliver Inferno Drainer, stealing over $43,000 from user wallets.

Red Canary uncovers Mocha Manakin, a new threat group using "paste and run" social engineering to deploy NodeInitRAT, a custom NodeJS RAT with potential ransomware links.

North Korean APT BlueNoroff (TA444) exploited deepfakes in Zoom calls to trick a crypto foundation employee into installing custom macOS malware for digital asset theft.

A Russian state-sponsored APT, UNC6293 (likely APT29), is exploiting Google Application-Specific Passwords in a sophisticated phishing campaign targeting critics of Russia
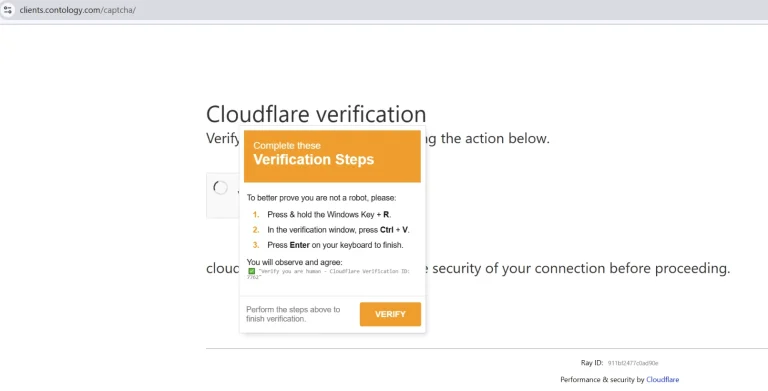
Elastic uncovers a sophisticated ClickFix campaign deploying the GHOSTPULSE loader to deliver ARECHCLIENT2 malware, leveraging social engineering for credential theft and remote access.

A fileless AsyncRAT campaign, dubbed "Clickfix," targets German-speaking users, luring them into executing obfuscated PowerShell payloads via fake verification prompts.

Water Curse is using GitHub to distribute malicious open-source projects, weaponizing 76 accounts with multi-stage malware targeting developers, red teamers, and gamers.

HijackLoader and DeerStealer are surging, using ClickFix social engineering and sophisticated evasion to bypass defenses and exfiltrate sensitive data.

HelloTDS is a sophisticated traffic direction system delivering millions to FakeCaptcha and other malware via advanced fingerprinting and evasive tactics.

CyberEye, a modular .NET RAT, offers widespread data theft and surveillance using a builder, Telegram C2, and anti-analysis features, making it a new threat.

Rapid7 reveals BlackSuit ransomware affiliates are adopting Black Basta tactics, using email bombing, fake Quick Assist scams, and evolving Java RATs.