
 Do Son
Google exposed UNC6229, a Vietnam-based group running "Fake Career" phishing on job boards. They use fake lures to compromise digital advertising accounts and corporate credentials for profit.
social engineering

Researchers from Palo Alto Networks Unit 42 have discovered a new phishing trend where attackers trick victims...

The Datzbro Android Trojan is targeting seniors via fake Facebook groups and AI content. The hybrid malware can remotely control devices and steal banking credentials.

A new report shows LAPSUS$, Scattered Spider, and ShinyHunters have formed a collaborative alliance, sharing tactics like social engineering and MFA bypass to launch global attacks.

EclecticIQ reports on how ShinyHunters is expanding with AI-driven voice phishing, supply chain compromises, and insider recruitment, blurring lines with APTs.

A new, advanced FileFix attack campaign uses social engineering and steganography to hide malware in images, bypassing traditional security defenses.

A new AI scam network is targeting Indian social media users. It uses deepfakes of celebrities and fake news sites to promote fraudulent investment schemes.

The Lazarus Group is using a new campaign to steal crypto by exploiting a vulnerability (CVE-2025-48384) with fake interviews and poisoned code repositories.
A new report reveals the AMOS infostealer is targeting macOS. The malware is spread via fake apps and malicious Terminal commands that bypass Gatekeeper.

A new report reveals that the North Korean Kimsuky APT is using social engineering on Facebook and Telegram to deliver AppleSeed malware to targets in South Korea.

A new campaign is abusing the legitimate RMM tool ScreenConnect to deliver RATs like AsyncRAT and PureHVNC, a trend that is on the rise, targeting US organizations.

A new report reveals a Lazarus Group subgroup is using a tiered arsenal of custom RATs—PondRAT, ThemeForestRAT, and RemotePE—to target the financial and crypto sectors.

A new report reveals a phishing campaign using fake ads and login pages to steal credentials from employees in the hospitality and vacation rental industry.

A new RAT, disguised as an AI assistant, is using social engineering to infiltrate a role-playing community. The malware provides attackers with full remote control over infected PCs.

A new report reveals a rise in phishing campaigns that abuse email marketing platforms and cloud services to evade detection and steal credentials from victims.
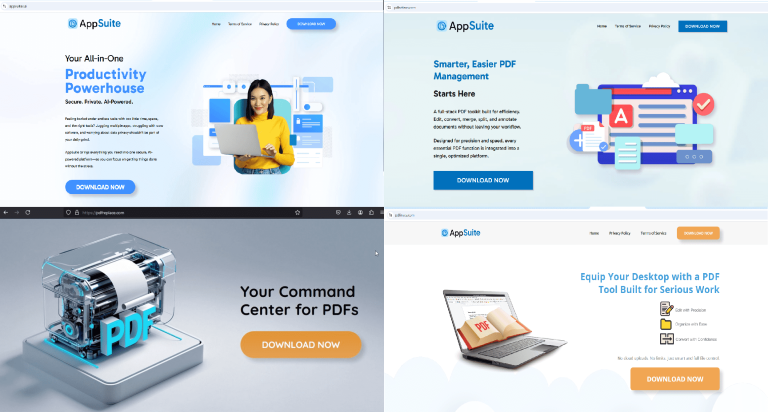
A new report reveals that the AppSuite PDF Editor is a Trojan horse that functions as a backdoor. Its developers even submitted it to AV vendors to get it whitelisted.

A new campaign is using fake AI-themed content to trick users into downloading a malicious ScreenConnect installer that secretly delivers the XWorm Remote Access Trojan.
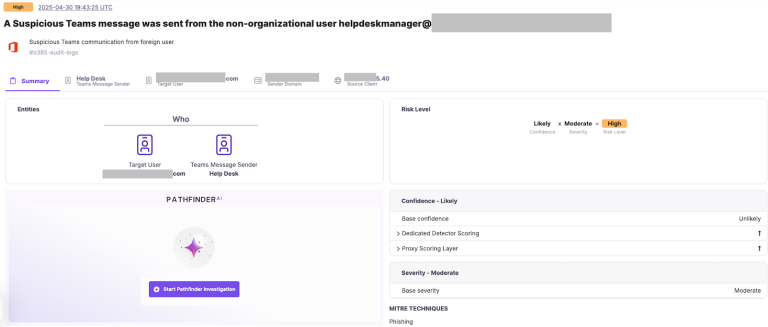
A new report reveals that attackers are abusing Microsoft Teams' collaboration features to launch phishing, vishing, and malware attacks, bypassing security warnings.

A new report reveals how scammers are exploiting the Ganesh Chaturthi festival in India with fake websites, lottery fraud, and phishing to steal money and data.

A new phishing campaign called ZipLine reverses the attack by tricking victims into initiating contact. It targets supply chains and deploys a custom in-memory implant.

A new report reveals that a phishing attack on a Salesforce vendor has led to a data breach at Farmers Insurance, exposing the data of over 1.1 million customers.
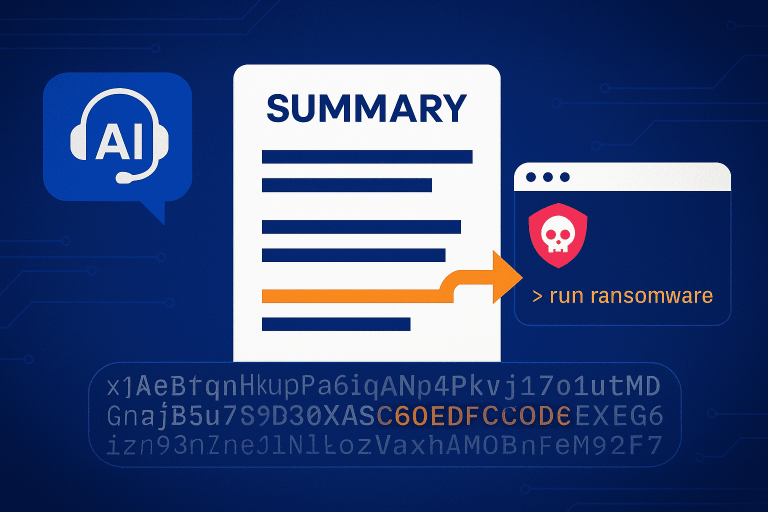
A new report reveals how attackers are using invisible text and "prompt overdose" to trick AI summarizers into delivering ransomware instructions to users.