 Do Son
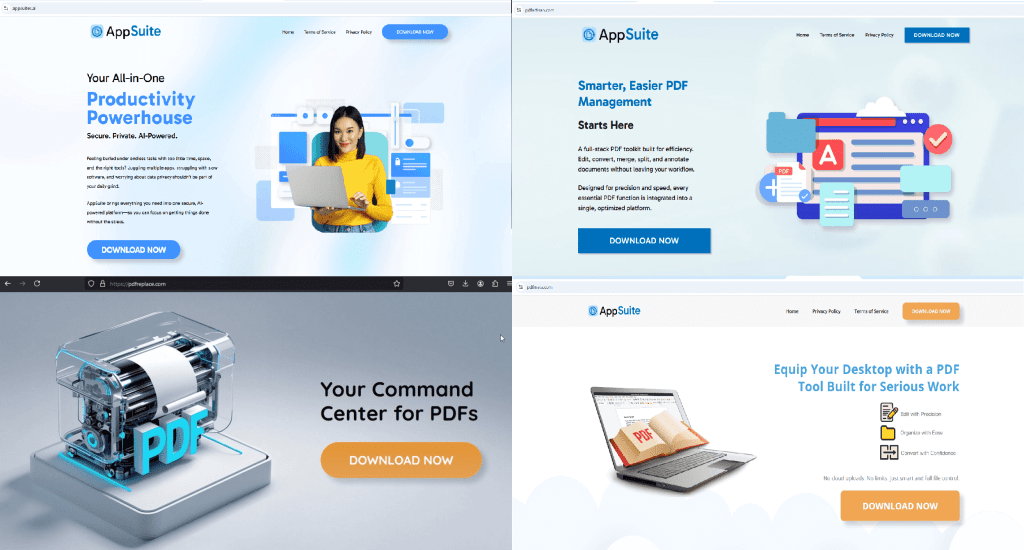
PDF editor is advertised on various websites with different designs | Image: G DATA
Security researchers at G DATA Security Lab have exposed the AppSuite PDF Editor as a malware-laden backdoor, despite the software masquerading as a legitimate productivity tool. The discovery comes after an attempt by the threat actors themselves to push antivirus vendors into whitelisting the program.
The investigation began in an unusual way. “Some threat actors are bold enough to submit their own malware as false positive to antivirus companies and demand removal of the detection. This is exactly what happened with AppSuite PDF Editor.” G DATA initially flagged the application as a potentially unwanted program (PUP), a classification often reserved for grayware bundling ads or shady installers. But deeper inspection revealed something more serious: “In the case of AppSuite, however, we found a backdoor.”
Threat actors have gone to lengths to promote AppSuite across high-ranking websites, tricking users into downloading it. According to the report, “Threat actors are leveraging websites, which have high-ranking search results, to lure users into downloading a deceptively functioning ‘productivity tool’ or ‘command center’ for PDF management.” These sites, while visually distinct, all serve the same malicious MSI installer.
Once installed, the fake PDF editor creates persistence through autorun entries and scheduled tasks, masking itself behind a partially functional Electron-based PDF editing interface. Out of 3,661 lines of code, G DATA found that “only 17 open the browser window and thus run the decoy application” —the rest powers the backdoor.
The real danger lies in the main component, pdfeditor.js, which contains heavily obfuscated JavaScript. This code interprets seemingly benign command line switches that trigger hidden backdoor routines. For example:
- The –install routine registers the application with a command-and-control (C2) server and sets up persistence tasks.
- The –ping routine encrypts system data with AES-128-CBC and sends it to attacker infrastructure for instructions.
- The –check and –reboot routines allow arbitrary commands from the C2 server, effectively granting attackers full remote control.
As G DATA notes, “To put it bluntly: This means AppSuite threat actors may execute arbitrary commands on the infected system. This is also the main reason we classify this malware as backdoor and not just as loader or stealer.”
The backdoor is capable of data exfiltration, registry manipulation, and deploying additional malware. It specifically targets browsers such as Chrome, Edge, OneLaunch, Shift, and Wave, extracting encryption keys, saved passwords, and other sensitive data. G DATA’s analysts stress that any infection where AppSuite has contacted its C2 should be considered unrecoverable: “Because of that unauthorized access, any backdoor infection that successfully contacted the command and control server should be cleaned by repaving the system, which means formatting the affected drives and re-installing the operating system.”
Instead of quietly spreading malware, they actively attempted to disguise it as a legitimate tool by appealing to antivirus vendors. As the report warns, “The boldness of AppSuite threat actors in submitting their malware as false positives is not an isolated incident. In recent weeks, we had multiple attempts by threat actors to challenge our verdicts while posing as legitimate software publishers.”
The AppSuite PDF Editor is more than just another shady freeware utility—it’s a full-fledged backdoor masquerading as a productivity app, distributed through search-optimized websites and equipped with extensive spying and persistence features.
As G DATA concludes: “There is no doubt in our view: AppSuite PDF Editor is malicious. It is a classic trojan horse with a backdoor that is currently massively downloaded.”
Users are strongly advised to avoid downloading free PDF tools from unofficial websites and to treat security vendor “false positive” disputes with skepticism—sometimes, as this case proves, malware authors are the ones filing the complaints.
Related Posts:
- APT29’s Espionage Campaign Exploits WinRAR Flaw, Targets Embassies
- Trustlook Labs found a trojan that target messenger app information
- Microsoft warned that a PDF editor was carrying a mining program after being hacked
- Information-Stealing ViperSoftX Malware Targets Cryptocurrencies and Password Managers Across the Globe
- Beware of Fake AI Photo Editors on Social Media: Malvertising Campaign Targets Credentials
Support Our Threat Intelligence
Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
