 Do Son
Microsoft will block MSIX and MSIXBundle attachments in Outlook and Exchange Online starting November 2026 to prevent malware distribution.
malware
Discover the Midnight Mimosa malware threatening cheap Android devices. Read the Bitdefender report on how OEMs pre-install this dangerous cybersecurity threat.

Chinese state hackers allegedly use Integrity Technology Group tools for botnet data theft. Protect your networks from this massive cyberespionage campaign.
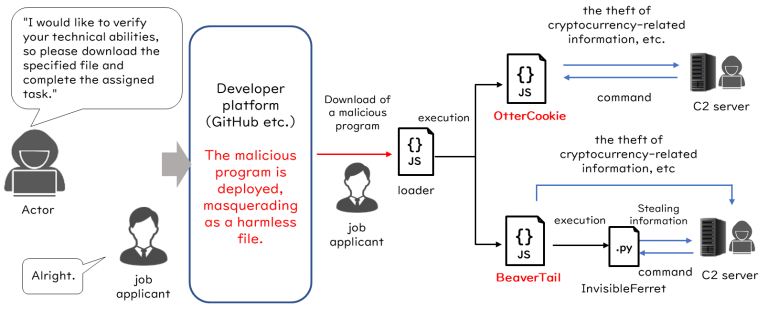
Discover how the North Korean WaterPlum cyber actor group uses fake job interviews to steal crypto and infiltrate networks globally.

The MacSync macOS stealer targets Apple users worldwide. See how MacSync macOS stealer ClickFix lures evade Gatekeeper to steal sensitive credentials.
Security teams uncovered trojanized fake macOS installers tied to North Korean campaigns that deploy OtterCookie malware on Apple devices.
Recent Node.js malware attacks target global firms. Attackers deploy Node.js malware using trusted runtimes and smart contracts to evade detection.
Researchers discovered malicious Packagist themes iOS spyware infecting unpatched iPhones. This spyware targets crypto wallets and steals device data.
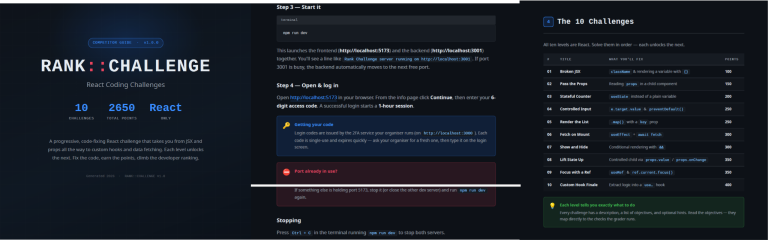
The suspected Mirage Kitten malware campaign targets developers in aviation and fintech with fake coding tests to deliver NodeRabbit and PollCat backdoors.
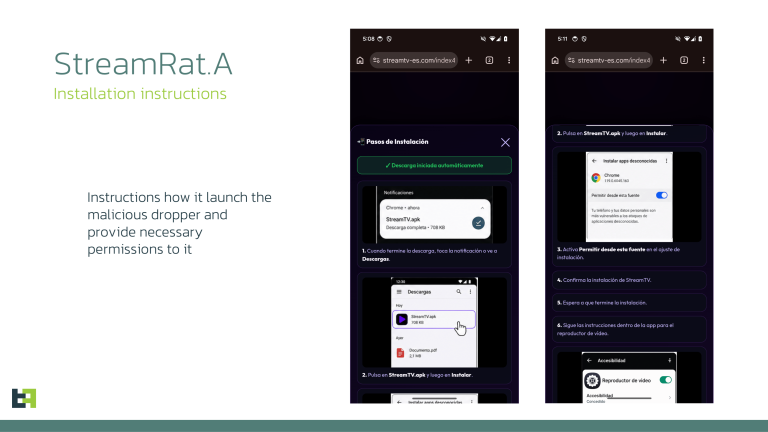
A StreamRat banking trojan campaign uses fake Meta TV-streaming ads to infect Android users. The StreamRat banking trojan enables full device takeover.
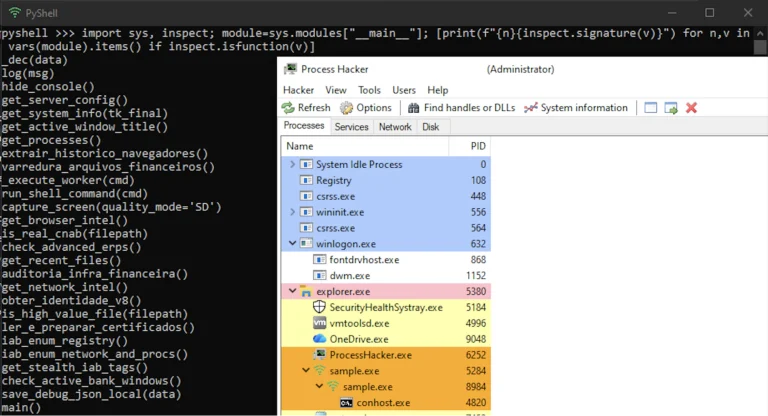
Group-IB uncovered the BraZetsu malware framework operations targeting financial systems. Learn how this tool powers initial access broker sales.

A new TerminalFix campaign uses fake CAPTCHAs to breach systems. Explore the TerminalFix attack chain and its covert reverse tunnel.
A Russian national indicted for malware faces trial. This Russian national indicted targeted 80,000 freelancers with malicious Excel attachments.
Hackers hijacked BGP routing to intercept Virtualizor updates and distribute malware. Learn how this complex supply chain attack bypassed critical security checks.
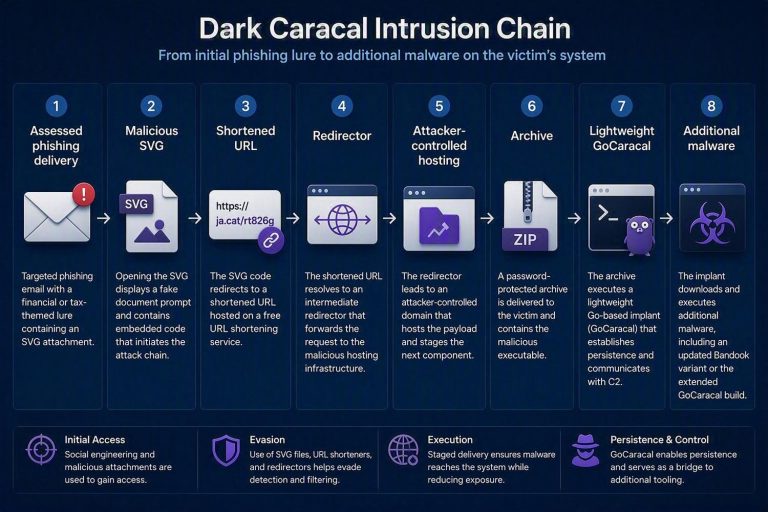
Researchers detected the Dark Caracal GoCaracal malware in South America. Learn how this GoCaracal malware uses Ethereum smart contracts.
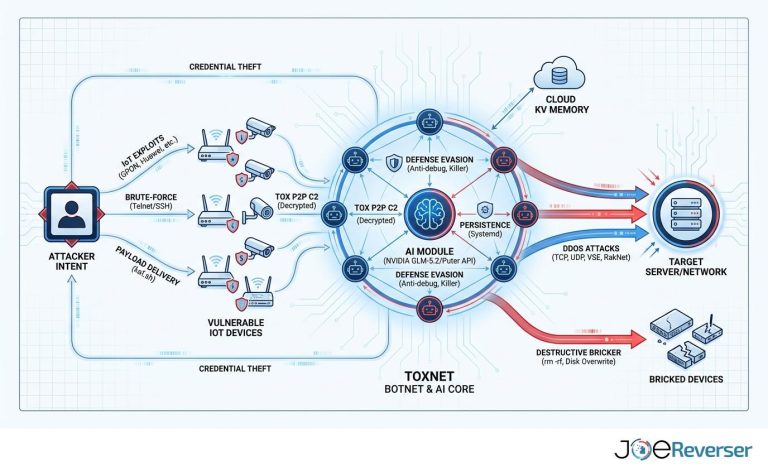
Discover how the sophisticated ToxNetV2 botnet utilizes the GLM-5.2 AI model to analyze infected systems and generate actionable malicious commands.
Kaspersky uncovered a ValleyRAT backdoor adware campaign using signed wallpaper apps to drop malware. Learn how to protect your systems.
Anthropic is sending security warnings and deleting payment methods as info-stealing malware compromises Claude user sessions. Protect your account now.
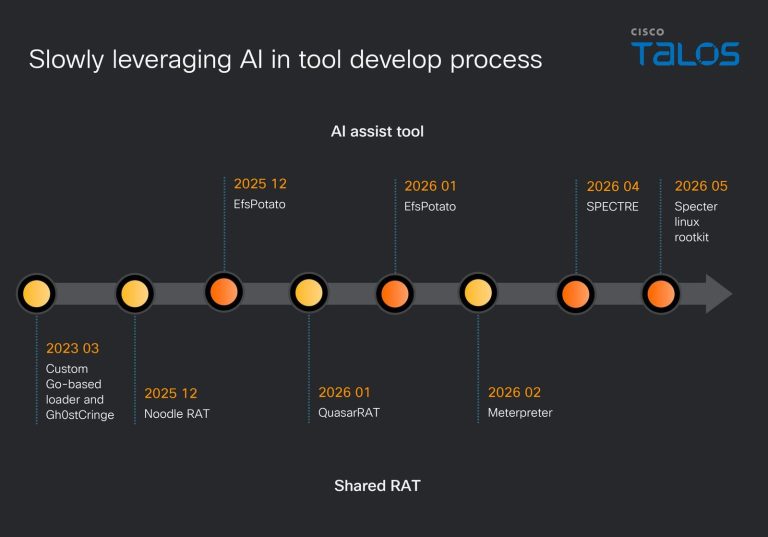
Cisco Talos reveals that Chinese-speaking threat group UAT-10147 deploys the SPECTRE cross-platform implant with Linux rootkits and BYOVD capabilities.
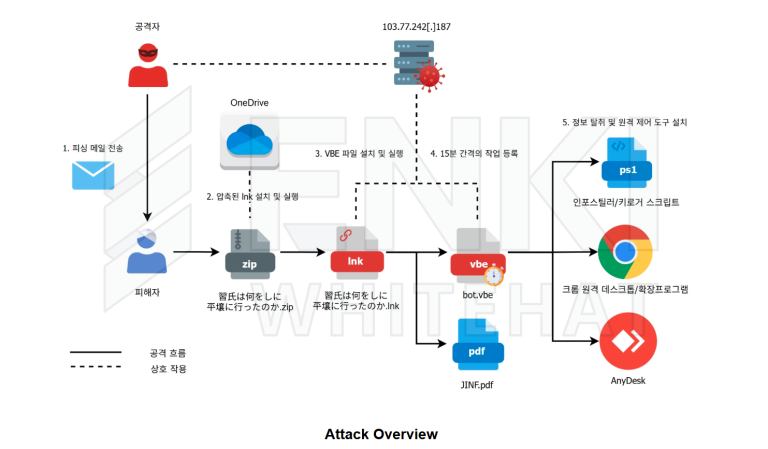
Recent Kimsuky spear phishing campaigns abuse remote control tools and AI extensions to target victims in Japan and South Korea. Read the full analysis.
Expel analyzed the SynkLoader malware attack chain. Discover how SynkLoader malware uses Teams phishing and fake lock screens to steal credentials.
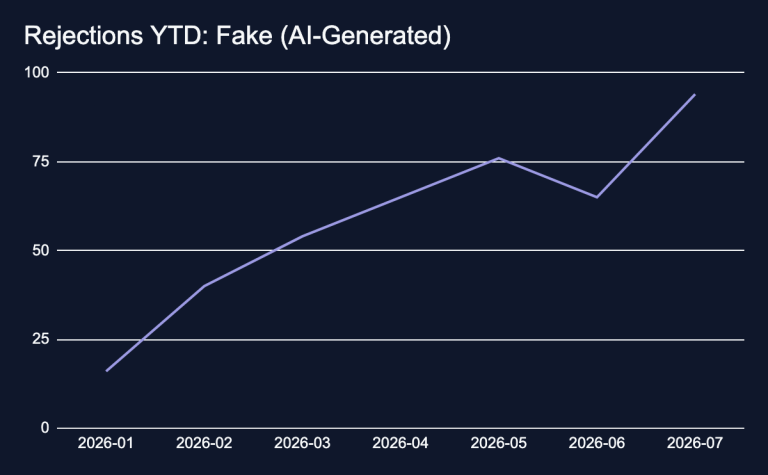
Fake AI PoCs and malicious code are taking over GitHub exploit repositories. Discover how researchers filter through the noise to find real vulnerabilities.