 Do Son
Sakura Internet disclosed a breach of its customer management system affecting 1.36 million accounts, though passwords were hashed and salted and no ransom was demanded.
malware

FortiGuard Labs discovered the Evooo1Bot Linux botnet. Read our Evooo1Bot Linux botnet analysis to learn how this malware turns devices into proxy nodes.

Zscaler ThreatLabz analysts discovered the Abyssos modular RAT. This Abyssos RAT gives attackers total remote control, stealing data and credentials.
Palo Alto Networks analyzed Kimwolf botnet malware. Read our Kimwolf botnet malware analysis to learn how it attacks Android TV boxes.

Kaspersky analyzed the Project CAV3RN framework. Read our Project CAV3RN framework analysis to see how attackers abuse DNS and Google Apps Script.
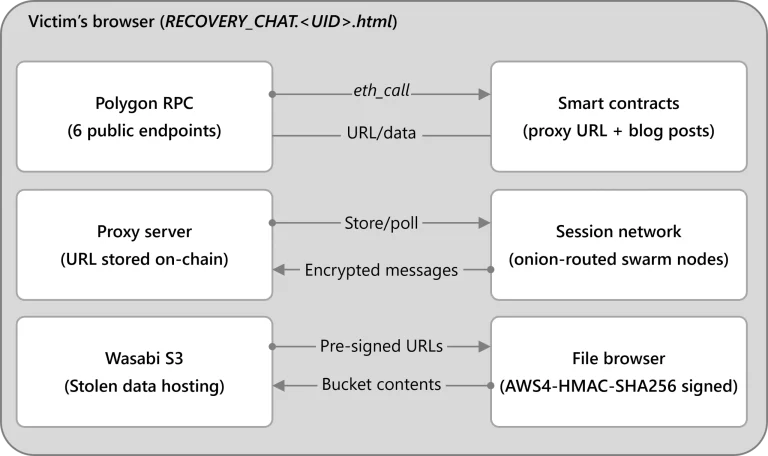
DeadLock ransomware uses blockchain nodes and Session chat. Learn how the DeadLock ransomware encryptor targets networks worldwide.

TELESHIM malware hits Middle East governments and abuses Telegram C2 to hide traffic. Zscaler ThreatLabz found the new backdoor and its tooling.

The new TAG-150 attack chain uses ClickFix to deploy DenoRAT malware and NightshadeC2. Learn how this threat targets financial sectors and crypto wallets.
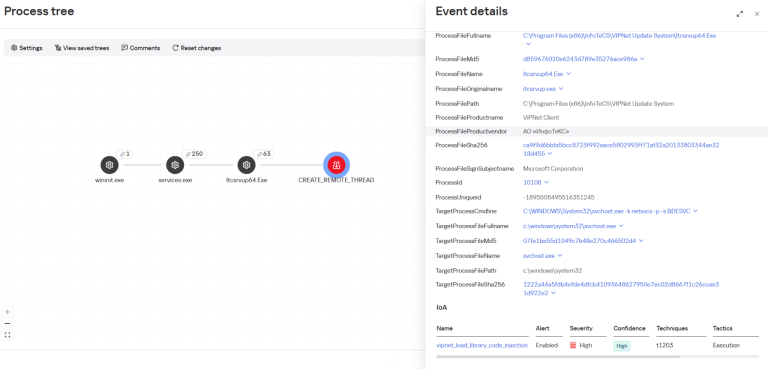
The HelloNet campaign spreads malware through the ViPNet update system, hitting Russian government and energy firms. Kaspersky suspects a China link.
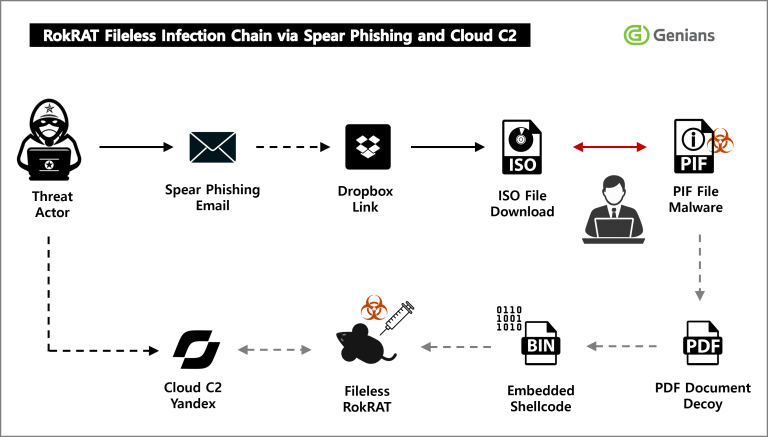
Genians exposed Operation Capsule Vault, an APT37 campaign. The RokRAT malware hides inside a fake PDF to spy on academics and researchers.

Doctor Web found a supply chain trojan targeting software developers. This developer-targeting malware steals data, crypto wallets, and mines coins.
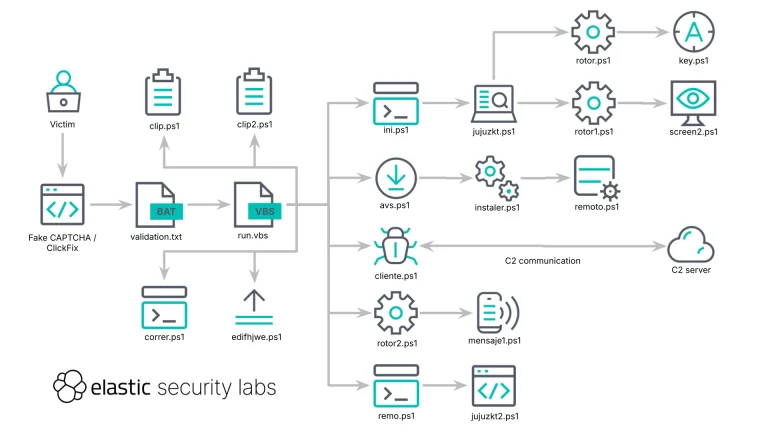
Discover how the REF6045 operation executes Mexican banking fraud. Hackers use fake CAPTCHAs and the SCMBANKER toolkit to steal financial data.
Suspected Iran-linked Cavern Manticore APT hackers deploy a new modular C2 framework to target Israeli government and IT sectors.
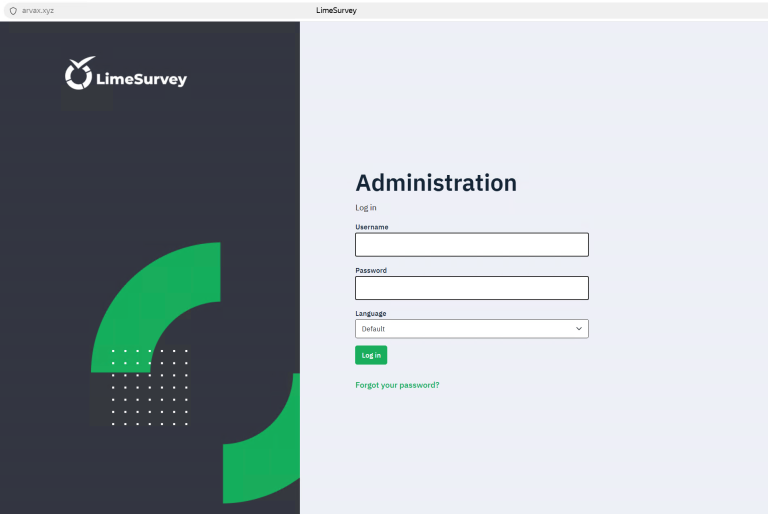
Suspected Armored Likho APT hackers deploy the new BusySnake Stealer to target government agencies and electric power sectors globally.

The FBI issued an alert about a TeamPCP supply chain attack. The group uses malicious code to conduct a software supply chain compromise against developers.
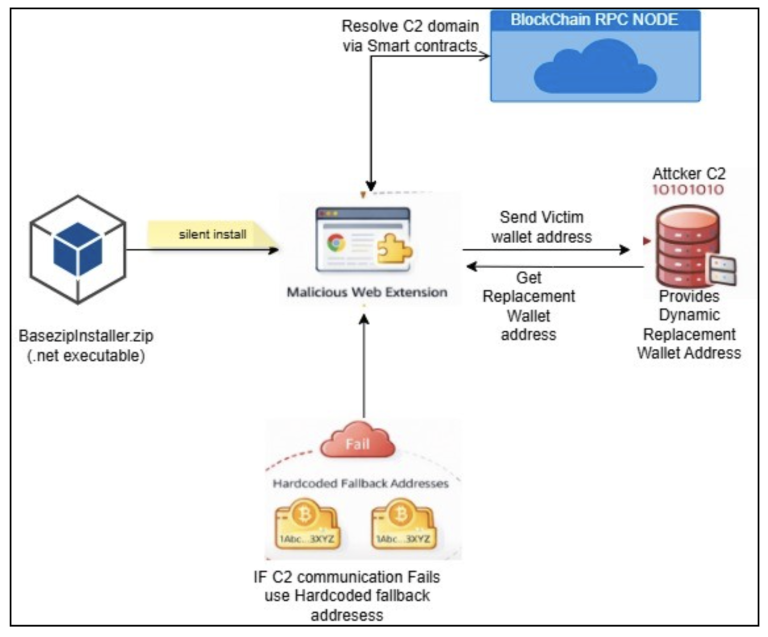
The Silent Swap crypto clipper steals digital assets via a fake Google Notes extension. Learn how this malware uses EtherHiding to drain your wallet.
An active hospitality malware campaign uses photo lures and authentication laundering to infect hotel networks with a persistent Node.js implant.
Chinese-speaking actors deploy TinyRCT backdoor attacks against Southeast Asian government and energy sectors. Discover the CL-STA-1062 cyber espionage tactics.

Threat actors are using RAR archive phishing to deploy Thailand healthcare malware. The campaign targets hospitals to steal credentials and sensitive data.
A new Mistic backdoor malware campaign linked to a ransomware access broker targets multiple sectors. Learn how this stealthy threat evades detection.
Microsoft discovered a new Windows crypto clipper malware. This Tor routed cryptocurrency stealer uses USB drives to spread and steal wallet addresses.
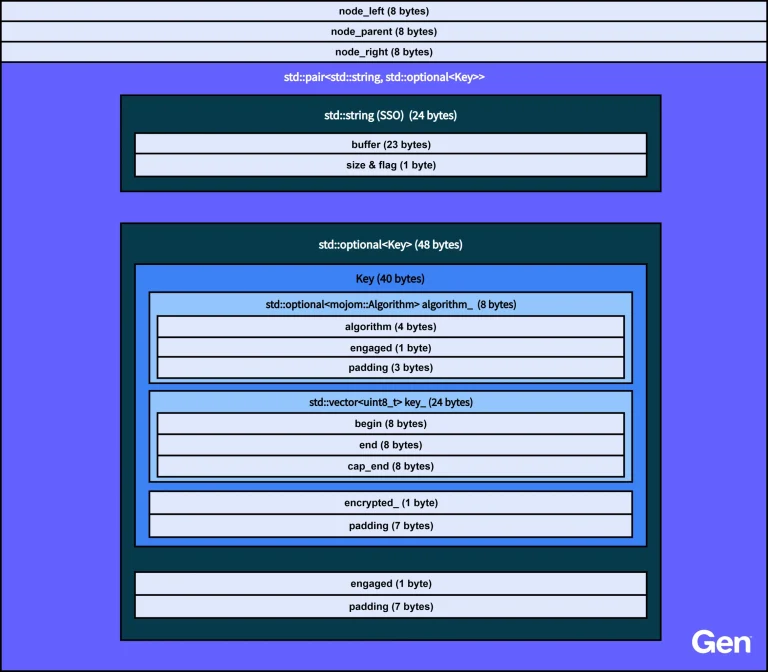
Gen Digital uncovered a new Vidar ABE bypass technique. The Vidar infostealer malware now uses memory scanning and APC injections to extract browser keys.