 Do Son
Broadcom warns of a VMware SDDC Manager vulnerability, CVE-2026-111497 (CVSS 9.8), from the Node.js Brotli vulnerability. Patches pending.
vmware
Broadcom introduces VMware monthly security updates to quickly patch flaws discovered by AI. Discover the new HyperArmor add-on for advanced virtual patching.
A VMware VMXNET3 vulnerability, CVE-2026-59346 (CVSS 9.3), allows VM escape. Full details and PoC exploit code are now public. Patch to 26H1u1.
CVE-2026-59346, a critical VMware Workstation vulnerability, lets an attacker escape a guest VM and execute code on the host. Broadcom rates it 9.3 CVSS.

HostDzire suffered a critical ransomware attack on its VMware infrastructure, encrypting virtual disks and causing total data loss for affected VPS users.
VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch

VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch
VMware Avi Load Balancer patches CVE-2026-47865 (CVSS 9.8), a critical authentication bypass, plus six more flaws. Upgrade the Avi Controller now.

New Broadcom security updates fix critical VMware stored XSS bugs. Learn how these vulnerabilities affect Cloud Foundation and how to patch now.

Broadcom unveils VMware Telco Cloud Platform 9 at MWC 2026, promising a 40% TCO reduction through AI-native architecture and sovereign cloud-ready infrastructure.

China-nexus WARP PANDA APT targets VMware/Azure with BRICKSTORM, a Golang backdoor using DoH for stealth. The group creates "ghost VMs" and conducts session replay attacks for long-term espionage.

CISA/NSA exposed BRICKSTORM, a Chinese state-sponsored backdoor targeting VMware vCenter/ESXi and ADFS servers. The self-restarting malware used DoH and nested TLS for 18 months of persistent espionage.

Broadcom is shifting VMware Workstation Pro/Fusion to year-based versioning (e.g., 25H2). The new release adds dictTool for .vmx editing, USB 3.2 support, and Hyper-V VM detection.

A zero-day flaw in VMware Tools (CVE-2025-41244) allows local attackers to gain root privileges. NVISO confirmed exploitation by a Chinese APT. A public PoC is now available.
Broadcom patches three vulnerabilities in VMware vCenter and NSX. The flaws could lead to SMTP header injection and username enumeration, increasing the risk of unauthorized access.

Broadcom has patched three flaws in VMware Aria Operations and VMware Tools. The vulnerabilities include privilege escalation and information disclosure.

GTIG reveals BRICKSTORM, a stealthy Go backdoor linked to China-nexus UNC5221, targeting US legal/SaaS firms to steal IP and establish long-term espionage access.
Tesco is suing Broadcom for £100M, alleging the company breached its perpetual license agreements for VMware, a move that could disrupt the retailer's operations.
Walmart has selected Broadcom's VMware Cloud Foundation to modernize its tech stack. The partnership will enable the retail giant to scale its private cloud and edge computing infrastructure.
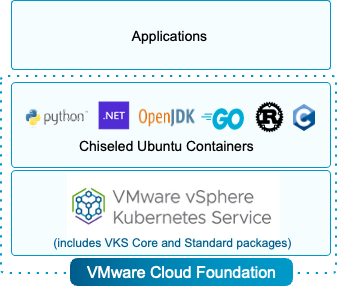
Broadcom and Canonical have partnered to integrate Ubuntu into VMware Cloud Foundation, providing streamlined, secure, and efficient AI and cloud-native application deployment.

Broadcom has unveiled new security services for VMware Cloud Foundation, focusing on compliance, Zero Trust, and post-quantum cryptography to secure AI workloads.
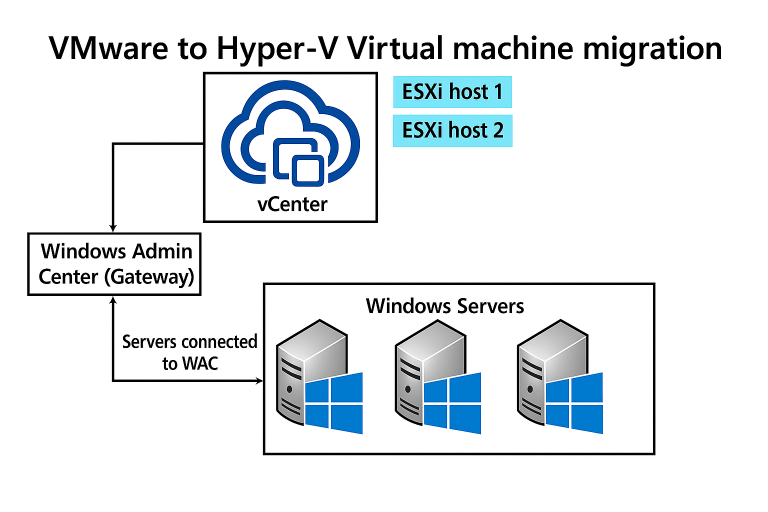
Microsoft has released a new VM Conversion utility in Windows Admin Center, allowing enterprises to seamlessly migrate their VMs from VMware to Hyper-V.

Sygnia uncovers "Fire Ant," a sophisticated cyber-espionage campaign exploiting VMware ESXi and vCenter since early 2025, using advanced techniques to evade detection and maintain persistent access.

European cloud providers (CISPE) are suing the EU Commission, alleging it failed to prevent Broadcom from abusing its market dominance after the VMware acquisition, leading to unfair competition.