 Do Son
A French blood bank cyberattack targeted EFS plasma refrigeration units, altering temperature thresholds before emergency alarms prevented product loss.
cyberattack
Ahold Delhaize cyberattack took brand sites offline in Europe and the US. Albert Heijn outage ends as the app returns; no data theft found yet.
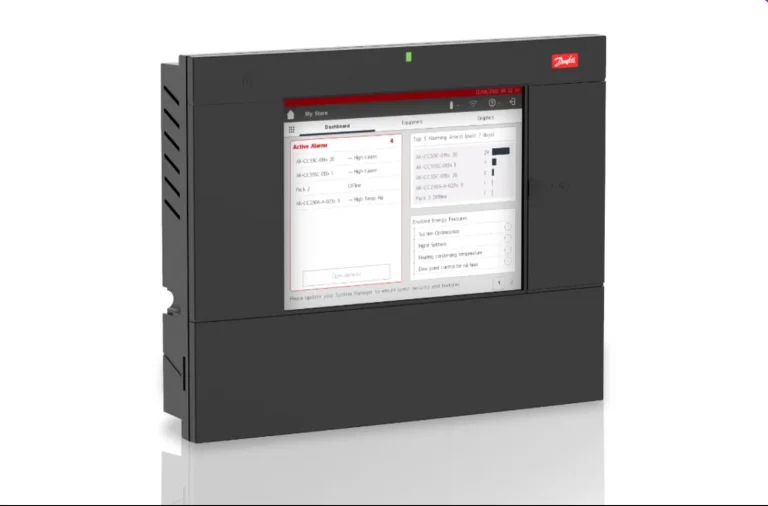
A massive French supermarket cyberattack targeted Danfoss refrigeration systems, causing catastrophic food spoilage and fires across 400 retail locations.

Discover the details behind the Nextcloud website hacked incident. Hackers exploited a vulnerability to redirect users to a dangerous phishing domain.

In a move to protect the nation’s critical infrastructure, the Cybersecurity and Infrastructure Security Agency (CISA) has...

Microsoft finds hackers using SolarWinds WHD to run hidden QEMU VMs. The attack uses DLL sideloading for full domain compromise. Patch immediately.

Ubisoft takes Rainbow Six Siege offline after a massive backend breach. Hackers gifted 2 billion credits to players and hijacked the game's ban system.

GreyNoise warns of a massive, synchronized RDP botnet using 100,000+ IPs from over 100 countries for RDP scanning and enumeration, with US infrastructure as the primary target.

A vulnerability dubbed "LNK Stomping" (CVE-2024-38217) is actively used to strip the 'Mark of the Web' from LNK files, bypassing Windows security policies.

Australian authorities issue an urgent alert on a critical SonicWall SSL VPN flaw actively exploited by Akira ransomware, urging immediate patching.
A 22-year-old Oregon man has been charged with operating the RapperBot botnet, a network of 10,000s of devices that launched over 370,000 attacks.

Pakistan's critical sectors have been hit by the Blue Locker ransomware. This sophisticated campaign is linked to the Proton malware family and exploits a recent holiday.

A new Charon ransomware campaign is targeting the Middle East's public sector and aviation with APT-level tactics, including DLL sideloading and anti-EDR.

A targeted phishing campaign against Israeli organizations uses a PowerShell-based RAT and compromised internal emails for delivery, making detection difficult.

CERT-UA uncovers a new UAC-0099 campaign targeting Ukraine's defense sector. The group uses a toolkit of MATCHBOIL, MATCHWOK, and DRAGSTARE malware for reconnaissance and data exfiltration.

A CoinDCX software engineer, Rahul Agarwal, has been arrested in connection with a $44M crypto heist after an internal probe linked the breach to his compromised work laptop.

Group-IB uncovers how UNC2891 used Linux bind mounts (MITRE T1564.013) to hide a physical ATM cyberattack, involving a Raspberry Pi and a plan to tamper with HSMs for fraudulent withdrawals.

OT-ISAC warns that China-linked APT group UNC3886 is actively targeting Singapore's critical infrastructure, exploiting zero-day vulnerabilities for stealthy, long-term access.

IBM X-Force warns that Russian-aligned Hive0156 is intensifying spear-phishing campaigns against Ukrainian government and military, delivering Remcos RAT via LNK/PowerShell files.

JPCERT/CC details a sophisticated, ongoing malware campaign exploiting Ivanti Connect Secure (CVE-2025-0282, -22457) using MDifyLoader, Cobalt Strike, vshell, and Fscan for stealthy persistent access.

LAB52 uncovers a sophisticated phishing campaign delivering DeedRAT, a modular backdoor by Chinese APTs, targeting Southeast Asian governments via vulnerable AV software.

Trellix has uncovered SquidLoader, a highly obfuscated malware targeting Hong Kong financial institutions to deploy Cobalt Strike beacons for persistent control.