
 Do Son
Google exposes a vast phishing campaign hijacking Booking.com reservation chats to steal credit card details from travelers, impacting thousands globally since Nov 2023.
cyberattack

TRM Labs' analysis of the Nobitex hack reveals Iran's crypto exchange was engineered for sanctions evasion, featuring deep fiat integration and blockchain obfuscation to defy surveillance.

Over 143,000 ICS devices in the power sector are publicly exposed to the internet, facing high/critical vulnerabilities. Urgent action is needed to secure global energy infrastructure.

Qantas Airways confirms a cyberattack on a third-party contact center platform exposed personal data of up to 6 million customers. No financial data or passwords compromised.

CISA, FBI, NSA, and DC3 warn of potential cyberattacks from Iranian-affiliated actors on vulnerable U.S. infrastructure and networks, urging vigilance despite recent ceasefires.

ASEC uncovers sophisticated attacks targeting South Korean Windows IIS and Linux systems, deploying WogRAT, MeshAgent, and SuperShell for cyber-espionage and lateral movement.

Palo Alto Networks exposes CL-CRI-1014, an IAB targeting African financial institutions. They use open-source tools like PoshC2 and Classroom Spy, disguised with forged signatures for covert network access.
Middle East Cyberwar Escalates: GPS Spoofing, Fake Alerts, Crypto Hacks, & IP Camera Spying Revealed

Middle East Cyberwar Escalates: GPS Spoofing, Fake Alerts, Crypto Hacks, & IP Camera Spying Revealed
Group-IB reveals escalating cyber operations in the Middle East, including widespread GPS spoofing, fake emergency SMS, the Nobitex crypto hack, and IP camera exploitation.

DRAT V2, a new Delphi-compiled RAT from TAG-140 (SideCopy/Transparent Tribe), is targeting Indian government entities with expanded post-exploitation and refined C2 techniques.

Pro-Iranian group Cyber Fattah leaked thousands of sensitive Saudi Games participant records, including PII and bank data, in a political information operation targeting Saudi Arabia.
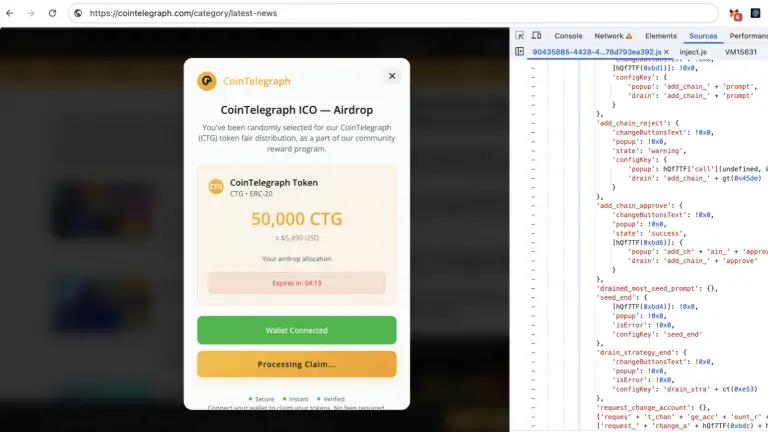
CoinTelegraph was hacked on June 22, 2025, with attackers injecting malicious JavaScript to display fake CTG airdrop pop-ups, stealing crypto by draining connected wallets.

Cloudflare successfully mitigated a record-breaking 7.3 Tbps DDoS attack in May 2025, delivering 37.4 TB in 45 seconds with no service disruption.

RapperBot botnet resurfaces with 50,000+ active bots, now demanding Monero extortion to halt DDoS attacks. The self-proclaimed "rapper" malware targets IoT devices globally.

Threat actors are actively compromising poorly managed MySQL servers, using UDFs to inject Gh0stRAT, XWorm, HpLoader, and legitimate Zoho agents for full system control and data theft.

Qilin ransomware is rapidly dominating the RaaS landscape, as rivals like RansomHub and LockBit face collapse, internal chaos, and public defacements by "XOXO from Prague."

A new wave of invoice-themed phishing emails is distributing the Sorillus RAT across Europe, leveraging legitimate platforms like OneDrive and Ngrok for stealthy delivery.
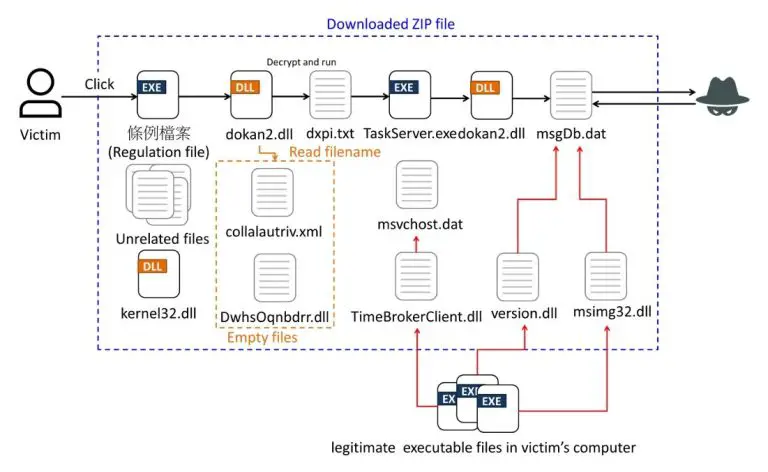
A sophisticated malware campaign is targeting Taiwan, impersonating the National Taxation Bureau to distribute Winos 4.0, HoldingHands RAT, and Gh0stCringe.

Hackers leaked 7.4 million Paraguayan citizen records on the dark web, demanding a $7.4M ransom. The breach likely stems from infostealer malware, sparking national security concerns.

GreyNoise reports a massive brute-force campaign targeting Apache Tomcat Manager interfaces, with hundreds of malicious IPs attempting to compromise services.

TeamFiltration is being actively exploited in UNK_SneakyStrike, targeting over 80,000 Microsoft Entra ID accounts with password spraying and data exfiltration.

Librarian Ghouls APT launches a new cyber-espionage and cryptojacking campaign targeting Russia and CIS, using legitimate tools for stealth.

Kimsuky's AppleSeed campaign targets Korean Facebook, email, and Telegram users with evolved social engineering and stealthy malware.