
 Do Son
The CoGUI phishing kit uses advanced evasion to target Japan with high-volume campaigns impersonating Amazon, PayPay, and more.
cyberattack
DragonForce ransomware cartel targets UK retailers with Conti-based payloads, RansomBay leaks, and phishing attacks, warns SentinelOne report.
California Man to Plead Guilty in Hack of Disney Employee, Theft of 1.1TB of Confidential Slack Data

California Man to Plead Guilty in Hack of Disney Employee, Theft of 1.1TB of Confidential Slack Data
Ryan Mitchell Kramer pleaded guilty to hacking Disney after using a fake AI art tool to steal 1.1TB of data. The attack involved malware and social engineering.

Sophos researchers detail a complex campaign using Cobalt Strike, DLL sideloading, and clever techniques like expired certificates
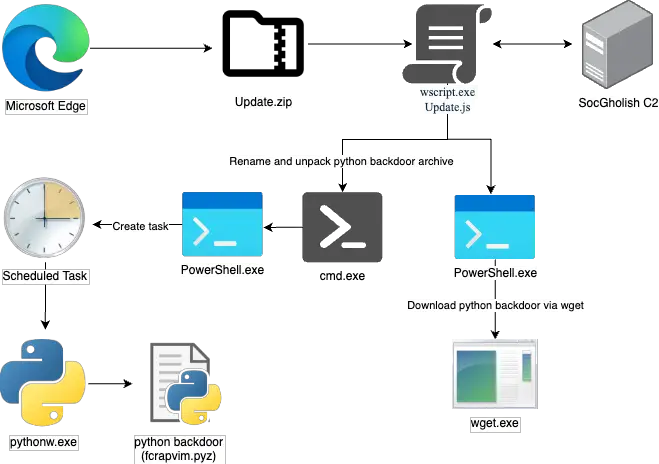
eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.

CVE-2025-31324 lets attackers exploit SAP NetWeaver to upload webshells and deploy C2 tools like Brute Ratel, affecting patched enterprise systems.

A sophisticated backdoor attack targeting ViPNet networks in Russia has been uncovered. Kaspersky Labs reports on the malware and its impact on organizations.

The Billbug group targeted Southeast Asian organizations using advanced tools & DLL sideloading. This report details their sophisticated espionage campaign.

State-sponsored hackers from North Korea, Iran, and Russia are now using ClickFix, a cybercrime-born social engineering trick.

ASEC report details Kimsuky's Larva-24005 campaign targeting South Korea and globally with RDP exploits, MySpy malware, and keyloggers.

A misconfiguration exposed APT41 tools targeting Shiseido, revealing Fortinet exploit scripts, webshells, and reconnaissance tactics.

Sekoia TDR reveals Interlock ransomware's evolving tactics, including ClickFix social engineering, to evade detection and steal data.

Anonymous claims 10TB cyberattack on Russia, exposing Kremlin-linked files, foreign assets, and data labeled “Donald Trump.”

APT29, a Russia-linked group, targets European diplomats with phishing emails disguised as wine tasting invitations, deploying GRAPELOADER malware

4chan was hit by a cyberattack resulting in the leak of source code, user data, and admin info. The forum is currently inaccessible

CrushFTP vulnerabilities CVE-2025-32102 & CVE-2025-32103 enable SSRF and directory traversal. Update now to secure your file transfer server

The Knownsec 404 team reports on the DarkHotel APT group's latest attacks, featuring upgraded frameworks and sophisticated evasion techniques.

GOFFEE APT is actively targeting Russian organizations with updated tactics, including the new PowerModul implant, sophisticated spear phishing, and lateral movement via custom Mythic agents

ViperSoftX malware is being used by Arabic-speaking attackers to target South Korea, according to ASEC. This malware uses PowerShell and spreads through torrents, delivering PureCrypter and Quasar RAT

A new report reveals Russia-linked Shuckworm's evolved cyber campaign targeting a military mission in Ukraine, featuring sophisticated malware and stealthy tactics.

Attackers are using SourceForge to distribute malware, including a ClipBanker Trojan and a cryptocurrency miner, disguised as a Microsoft Office enhancement suite.

Uncover the details of the Safe{Wallet} hack involving Bybit and how hackers accessed the cryptocurrency vault.