
 Do Son
Akamai reports active exploitation of critical Wazuh RCE (CVE-2025-24016) by multiple Mirai botnets, targeting IoT devices since March 2025.
cyberattack

A sophisticated spear-phishing campaign using Signal targeted Armenian civil society and government in March 2025, linked to threat actor UNC5792.
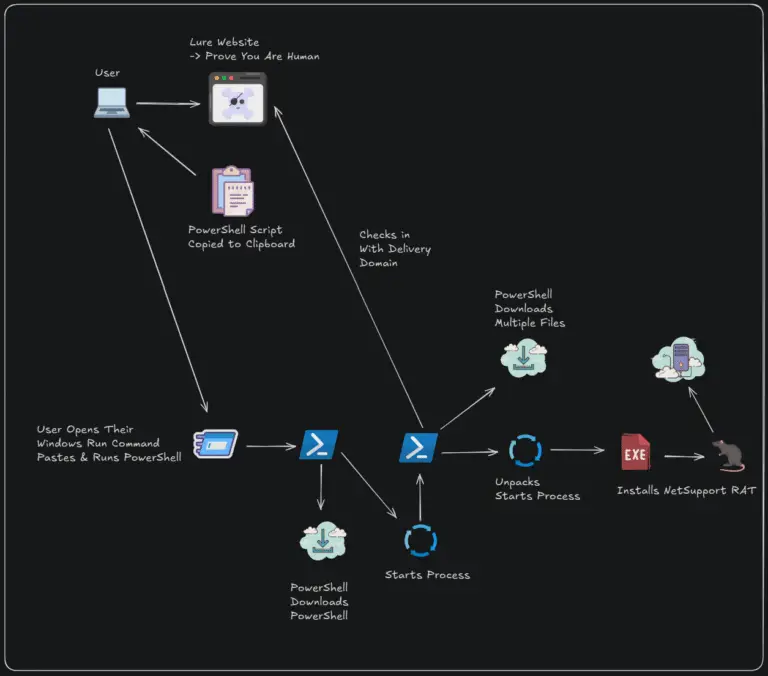
A new campaign uses fake DocuSign & Gitcodes pages to trick users into manually installing NetSupport RAT, gaining remote control.

K7 Labs details an evolved PowerShell malware, ViperSoftX 2025, featuring enhanced modularity, stealth, and persistence for advanced attacks.

A U.S. jury ordered NSO Group to pay Meta's WhatsApp $167M in damages for its 2019 Pegasus spyware attack on 1,400+ users.

BitoPro confirms $11.5M hot wallet cyberattack after investigator @zachxbt exposed the theft. User funds are safe, but initial silence raises concerns.

BitMEX security team infiltrates Lazarus Group's infrastructure after a phishing attempt, exposing their tactics and even a hacker's real location.

High-severity flaws (CVE-2025-20298 & CVE-2025-20297) impact Splunk Enterprise & Universal Forwarder. Learn how to protect your data.

A sophisticated malware campaign targets Korean Internet cafés with Gh0st RAT and CoinMiner, hijacking systems for crypto mining. ASEC urges immediate action.

Critical Chrome security update released! Patching an actively exploited zero-day vulnerability (CVE-2025-5419) and other flaws. Update now to stay safe!

AyySSHush is a new stealthy botnet backdooring ASUS routers via SSH keys, abusing legitimate features to persist across firmware updates and targeting residential networks globally.

Amidst India-Pakistan tensions, Bitter APT launched a spear phishing campaign against Pakistan Telecommunication Company, using WmRAT for espionage.

ConnectWise disclosed a targeted cyber intrusion by a sophisticated nation-state actor affecting a small subset of ScreenConnect customers. Enhanced monitoring is in place.

Attackers compromised an MSP's RMM tool (SimpleHelp) to deploy DragonForce ransomware across customer environments.

The Rhadamanthys stealer is back with targeted phishing attacks across Central and Eastern Europe, using fake copyright infringement lures.

Phishing campaign uses deceptive domains to target Kuwaiti sectors. Details on how attackers impersonate brands and steal credentials.

New report details APT37's "ToyBox Story" campaign, using spear phishing and cloud services to deploy RoKRAT malware. Fileless attacks and stealthy tactics revealed.

Sophisticated malware hides inside image files within .NET apps to secretly infect systems, targeting finance in Türkiye and logistics in Asia.

A sophisticated campaign deployed malicious IIS modules on South Korean web servers, enabling traffic control and backdoor access. Suspected Chinese actor.

DieNet, a new hacktivist group, is leveraging DDoS-as-a-service for rapid-fire attacks on critical infrastructure. NETSCOUT reports on their tactics and targets.

Agenda ransomware (Qilin) is back, now using the advanced NETXLOADER and SmokeLoader to enhance infiltration and evade detection. Targets global sectors.
A sophisticated phishing campaign, possibly by APT36, spoofs Indian government sites and uses ClickFix tactics to target Windows and Linux users.