Nobitex Hack Unveils Iran’s Crypto Blueprint: Sanctions Evasion & Surveillance Defiance Exposed
 Do Son
Hacker man using laptop and computer with Bitcoin green binary graphic and cryptocurrency candlestick graph price on monitor screen. Cyber crime digital currency laundering concept
Last month, Iranian crypto giant Nobitex fell victim to a cyberattack of unprecedented scale. While most headlines focused on the USD $90 million drained from its hot wallets, the true story is far more intricate—and politically charged. According to a new analysis from TRM Labs, the breach, attributed to the hacktivist group Predatory Sparrow, reveals a blueprint for how a cryptocurrency exchange in a sanctioned state can operate with global reach, regulatory defiance, and military-grade obfuscation.
“This is not just a postmortem on a hack—it is a forensic map of an exchange designed to operate in defiance of sanctions, surveillance, and regulatory oversight,” TRM Labs emphasized in its report.
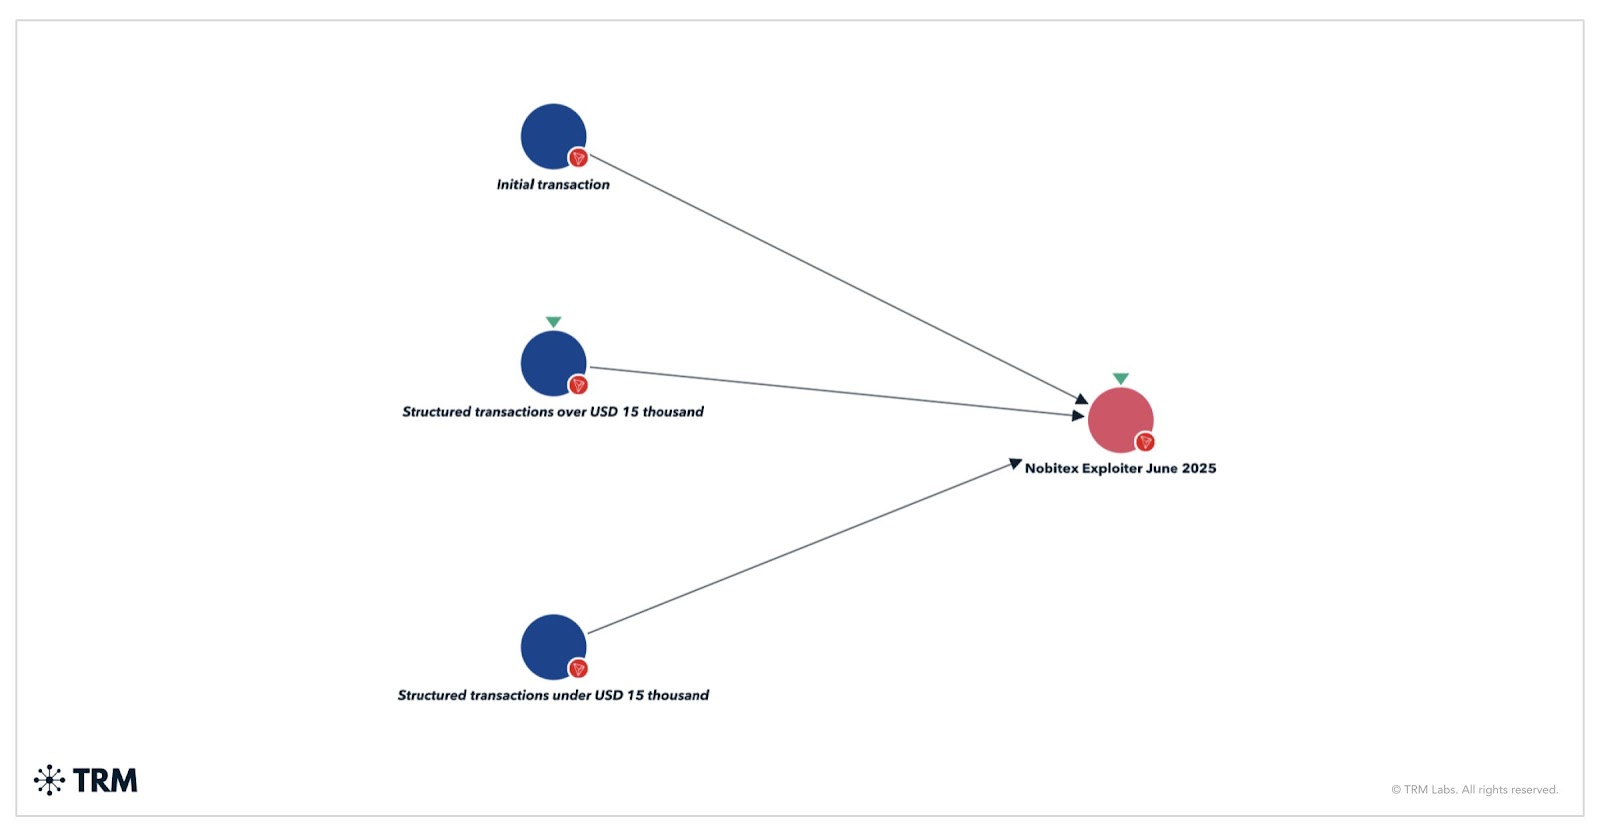
The initial strike looked like a financial raid. Nearly $90 million was drained from Nobitex’s hot wallets and funneled into crypto addresses etched with anti-regime slogans—signaling a motive beyond mere profit. But the attackers didn’t stop there.
Just 48 hours later, Nobitex’s entire source code, internal privacy R&D, and infrastructure documentation were leaked online. This included architectural diagrams, custom wallet systems, privileged user logic, and even API keys hard-coded into the exchange’s systems.
TRM Labs’ review paints Nobitex not as a mere marketplace, but as an intricately engineered financial bridge between Iran’s sanctioned economy and the global crypto ecosystem.
The leaked source code exposed a layered wallet architecture with discrete modules for cold and hot wallets. Servers like coldui.nxbo.ir and wallet.nobitex1.ir managed transaction lifecycles and introduced parameters like LOAD_LEVEL for dynamic routing.
However, once breached, the IP-based routing allowed lateral movement—mirroring flaws seen in mainstream exchanges. “The architecture resembled that of large global exchanges,” TRM noted, “suggesting that the same risks—and attack surfaces—apply broadly.”
Nobitex had deep hooks into Iran’s fiat economy, featuring live API integrations with platforms like Shetab, PAY.IR, Vandar, and IDPay. These integrations were not abstracted but hard-coded—enabling instant crypto-to-Rial conversions and account verification inside Iran’s isolated financial system.
“This wasn’t just an exchange—it was a full-service financial bridge,” TRM concluded. “Users could move funds between Iranian Rials/Toman and crypto seamlessly, bypassing the international banking system.”
What truly sets this breach apart is Nobitex’s deliberate effort to evade blockchain surveillance. The leaked code and internal documents reveal a suite of obfuscation tools—including modules named owshen, zpk, and incentivized_mixer.
These tools enabled stealth address generation, transaction batching, output splitting, and endpoint switching—techniques designed to render blockchain analytics tools like those used by FinCEN or Chainalysis ineffective.
“The design of this privacy stack was adversarial by nature—meant not merely to protect user data, but to frustrate regulators and analytics providers at scale,” the report explains.
Even more concerning, VIP users were routed through privileged logic that bypassed compliance checks, shielding politically sensitive individuals and potentially sanctioned actors from oversight.
Nobitex supported over 25 blockchain networks—from Bitcoin and Ethereum to emerging ecosystems like Aptos, NEAR, and Cosmos. Integration with explorers like Etherscan and Toncenter allowed cross-chain activity to be obfuscated further.
“A single user or VIP pathway could touch multiple ecosystems, making it harder for compliance teams to detect patterns,” TRM Labs observed.
Despite using encryption extensively and integrating error monitoring tools like Sentry.io, Nobitex’s development environments exposed plaintext secrets, Telegram bot tokens, and even master encryption keys in environment variables. These operational security failures likely enabled the full compromise.
Perhaps the most dangerous takeaway is how modular and duplicable Nobitex’s architecture is. Wallet modules, fiat APIs, and even privacy stacks were neatly separated into plug-and-play components. This makes the entire system easily forkable by other rogue states or operators looking to replicate Iran’s model of sanctioned financial autonomy.
“This raises the risk of code proliferation… extending Iran’s financial influence and creating additional blind spots in the global crypto economy,” warns TRM Labs.
Related Posts:
- A report says Iran may launch cyber attacks against sanctions
- Iran’s Phishing Pandemic: 245 Fake Banking Apps Target Citizens
- Following Russian, Iran also issued a signal to ban Telegram
- Iran is considering to launch its own cryptocurrency
Support Our Threat Intelligence
Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
