 Do Son
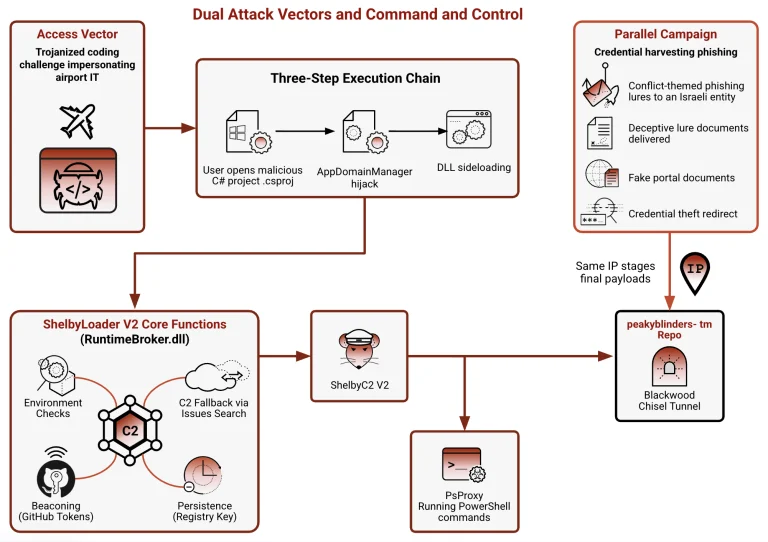
The Blinder Tunnel campaign used a fake Dubai Airports coding test to drop ShelbyLoader V2 on an Iraqi target. See how it works and how to defend.
Iran
Discover why Iranian bank SSL certificates are failing. US sanctions force institutions to use backup domains and consider risky domestic root certificates.
Iran's IRGC claims cruise missiles destroyed the AWS Bahrain data center, but the site has been offline since March and no one has confirmed the strike.
Suspected Iran-linked Cavern Manticore APT hackers deploy a new modular C2 framework to target Israeli government and IT sectors.

Check Point Research uncovers an Iran-linked password spraying campaign targeting M365 to support kinetic missile strikes and damage assessment in the ME.
FBI Director Kash Patel’s personal Gmail was breached by the Iran-linked Handala Hack Team. Discover how "SpiderKash" footprints led to a major OSINT leak.

Starlink activates free service in Iran in Jan 2026 to bypass a 99% internet blackout, using firmware updates to defeat military-grade jamming.

Iran's nationwide internet blackout saw a brief 0.01% traffic surge from Tehran universities on Jan 9, 2026, signaling a new "whitelist" control strategy.

A massive leak exposes Iran's Department 40 (APT35). Discover how IRGC hackers build target packages for assassination squads and drone strikes.

Stormshield CTI uncovers ongoing APT35 phishing infrastructure impersonating video conferencing services to target organizations in Israel and other regions.

An Iranian state-aligned APT, Nimbus Manticore, is targeting European defense and telecom firms with sophisticated spear-phishing campaigns and new malware.
Group-IB reports on MuddyWater, an Iranian APT, shifting tactics from RMM tools to custom malware and spearphishing, using new backdoors like Phoenix.

An Iranian-aligned group abused a compromised Omani Foreign Ministry mailbox to send spear-phishing emails to diplomats and international organizations in a global campaign.

Lookout uncovers an evolved DCHSpy Android spyware linked to Iran's MuddyWater APT, targeting high-value geopolitical entities with new Starlink and VPN lures.

TRM Labs' analysis of the Nobitex hack reveals Iran's crypto exchange was engineered for sanctions evasion, featuring deep fiat integration and blockchain obfuscation to defy surveillance.
CISA, FBI, NSA, and DC3 warn of potential cyberattacks from Iranian-affiliated actors on vulnerable U.S. infrastructure and networks, urging vigilance despite recent ceasefires.
Middle East Cyberwar Escalates: GPS Spoofing, Fake Alerts, Crypto Hacks, & IP Camera Spying Revealed

Middle East Cyberwar Escalates: GPS Spoofing, Fake Alerts, Crypto Hacks, & IP Camera Spying Revealed
Group-IB reveals escalating cyber operations in the Middle East, including widespread GPS spoofing, fake emergency SMS, the Nobitex crypto hack, and IP camera exploitation.

Pro-Iranian group Cyber Fattah leaked thousands of sensitive Saudi Games participant records, including PII and bank data, in a political information operation targeting Saudi Arabia.

Iran has drastically cut internet connectivity to 3% nationwide, citing Israeli cyberattacks. The blackout includes international calls, affecting millions amid rising tensions.

ESET uncovers BladedFeline, an Iran-aligned APT group, targeting KRG, Iraq, and Uzbekistan in a sophisticated cyberespionage campaign.

Meta's Q1 2025 report details the takedown of covert influence campaigns from China, Iran, and Romania, utilizing AI and fake accounts to manipulate public discourse.

Municipal Water Authority of Aliquippa (MWA) in western Pennsylvania was targeted by an Iranian-backed cyber group known as CyberAv3ngers