 Do Son
A Keystone wallet data breach via Shopify API exposed customer shipping addresses, raising physical wrench attack concerns for crypto holders.
cryptocurrency
An unpatched Electrum wallet vulnerability allowed malicious servers to manipulate RBF fee bumps, redirecting bitcoin payments to attacker addresses.
DOJ officials announced a Cambodia crypto scam extradition after Zheng Zhao allegedly helped launder $36.9M stolen from 174 US victims via USDT.
The Binance Pool shutdown arrives November 10, ending cloud mining and transaction acceleration. See what miners must do before then.
The Revolut data breach leaked passports, selfies, and crypto records of wealthy users, raising the risk of real-world wrench attacks. Details here.

A devastating ColdCard wallet hack has cost investors nearly $100 million. A critical firmware flaw allowed hackers to drain Bitcoin funds effortlessly.

North Korea's ClickFake Interview campaign targets crypto pros with fake skill tests, dropping the PylangGhost RAT on Windows and GolangGhost on macOS.

Microsoft discovered a new Windows crypto clipper malware. This Tor routed cryptocurrency stealer uses USB drives to spread and steal wallet addresses.
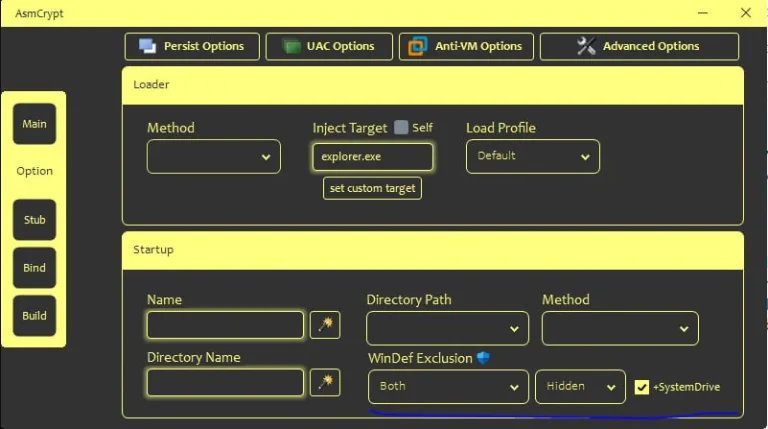
SilabRAT malware, aka SnappyClient, is a $5K/month MaaS RAT flagged as HijackLoader. It uses HVNC and cracks crypto wallets, per Group-IB.

The alleged mastermind behind the massive "Versus Project" dark web market has been extradited to the US. He faces life in prison for cybercrime and drugs.
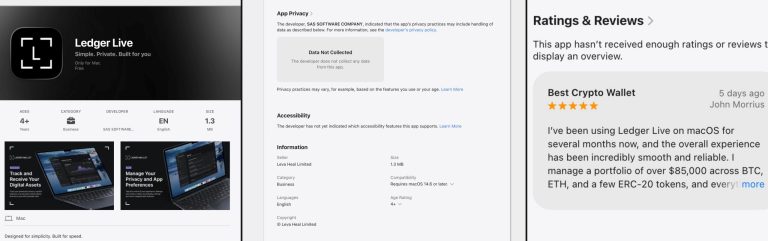
A malicious fake Ledger Live app on the Mac App Store has stolen $9.5M from users. Learn how the scam bypassed Apple's security and why your seed phrase is at risk.
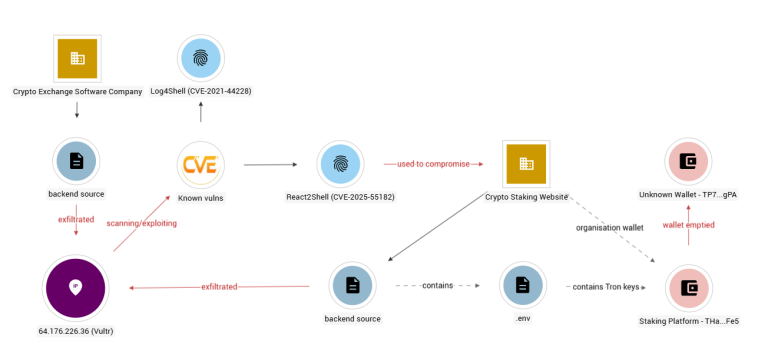
Ctrl-Alt-Intel exposes a suspected DPRK campaign using an 'Amazon Kill Chain' and React2Shell to systematically breach crypto exchanges and steal code.

Moonlock Lab uncovers a North Korean-aligned malware campaign targeting Web3 pros. Attackers use fake VC profiles and ClickFix CAPTCHAs to deploy malware.

Critical dYdX supply chain attack: Compromised npm & PyPI packages steal seed phrases & deploy RATs. Remove @dydxprotocol/v4-client-js immediately.

KONNI APT targets APAC developers with AI-generated malware disguised as crypto projects. The "polished" backdoor steals wallets & credentials.

Bitfinex hacker Ilya Lichtenstein released early in Jan 2026! He credits Trump’s First Step Act and vows a new career in cybersecurity research.

PayPal seeks an industrial bank charter in Utah to cut reliance on partners, fund small businesses directly, and consolidate its growing cryptocurrency and PYUSD stablecoin operations.

A dangerous new Android malware called SeedSnatcher targets crypto users with overlay phishing on MetaMask/Trust Wallet. It uses BIP 39 validation to steal seed phrases and supports remote command execution for total device control.

A malicious Rust package (evm-units) was live on Crates.io for 8 months, hiding RCE in a version check function. The loader uses VBScript and checks for Qihoo360 to compromise crypto developers on Windows/Linux/macOS.

The new infostealer Acreed is rapidly gaining market share post-Lumma takedown. It uses BNB Smart Chain and Steam profiles for C2, with a focus on crypto theft.

A Steam game, BlockBlasters, was compromised with malware in an update, which is stealing crypto and credentials from unsuspecting gamers.

The Lazarus Group is using a new campaign to steal crypto by exploiting a vulnerability (CVE-2025-48384) with fake interviews and poisoned code repositories.