
 Do Son
MoonPay CEO Ivan Soto-Wright lost $250K in a crypto scam where perpetrators impersonated a Trump Inaugural Committee co-chairman, highlighting executive-level deception.
cryptocurrency

The DOJ unsealed an indictment against OmegaPro founders for a $650M global crypto Ponzi scheme. They face charges for defrauding investors with fake forex trading promises.

Socket uncovers a sprawling network of malicious Firefox extensions, masquerading as games, VPNs, and tools, to hijack affiliate links, steal OAuth tokens, and reroute traffic.

TRM Labs' analysis of the Nobitex hack reveals Iran's crypto exchange was engineered for sanctions evasion, featuring deep fiat integration and blockchain obfuscation to defy surveillance.

North Korean APTs are using "NimDoor," a new Nim-based macOS malware, to target Web3/crypto startups via fake Zoom meetings, stealing browser, Keychain, and Telegram data with novel persistence.

A new macOS information stealer, a potential AMOS variant, targets crypto users and Ledger Live accounts, stealing passwords and wallet data using stealthy daemonization and local admin prompt tactics.

Europol and allies arrested 5, dismantling a global crypto investment fraud ring that laundered €460M from 5,000+ victims, exploiting Hong Kong banking networks.

CYFIRMA uncovers "Odyssey Stealer," a new macOS malware using fake App Store prompts & typosquatting to steal crypto wallets, passwords, and browser data from Western users.

Notorious hacker "IntelBroker" (Kai West) has been arrested, traced by the FBI through his crypto transactions. He's charged with stealing and selling data, causing $25M in damages.

Taiwan's BitoPro exchange confirms North Korea's Lazarus Group stole $11.5M in crypto via phishing an employee and bypassing MFA on AWS infrastructure.

Kaspersky uncovers SparkKitty mobile spyware, which infiltrates Android/iOS via TikTok mods and crypto apps, using image recognition to steal sensitive photos like crypto seed phrases.
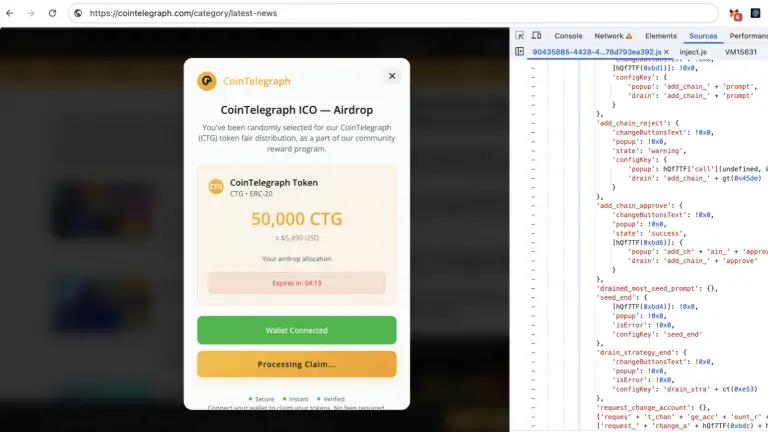
CoinTelegraph was hacked on June 22, 2025, with attackers injecting malicious JavaScript to display fake CTG airdrop pop-ups, stealing crypto by draining connected wallets.

CoinMarketCap suffered a client-side attack on June 20, 2025, using a fake "doodle" graphic to deliver Inferno Drainer, stealing over $43,000 from user wallets.

The Prometei botnet is back with a stealthy Linux variant, actively mining Monero and stealing credentials. It uses DGA, custom UPX packing, and sophisticated anti-analysis techniques.

North Korean APT BlueNoroff (TA444) exploited deepfakes in Zoom calls to trick a crypto foundation employee into installing custom macOS malware for digital asset theft.

A new campaign, "Stargazers Ghost Network," weaponizes Minecraft mods on GitHub to distribute a multi-stage infostealer, targeting user credentials and crypto wallets.

North Korean APT Famous Chollima (Wagemole) is using a new Python-based RAT, PylangGhost, in fake job interviews to target crypto professionals and steal credentials.

KimJongRAT is back with new PE and PowerShell variants, using LNK files and CDNs to steal browser, email, and over 30 crypto wallet details from victims.

Malicious phishing apps are bypassing Google Play Store security, tricking users into revealing crypto wallet seed phrases and draining funds. Beware and never share your seed
Attackers are hijacking expired Discord invite links, redirecting users to malicious servers that deploy AsyncRAT and crypto-stealing Skuld Stealer via clever social engineering.

ViperSoftX, a stealthy malware, is actively spreading via fake software to steal cryptocurrency and enable remote control, affecting users globally.