 Do Son
Attackers are hijacking expired Discord invite links, redirecting users to malicious servers that deploy AsyncRAT and crypto-stealing Skuld Stealer via clever social engineering.
cryptocurrency

ViperSoftX, a stealthy malware, is actively spreading via fake software to steal cryptocurrency and enable remote control, affecting users globally.

K7 Labs details an evolved PowerShell malware, ViperSoftX 2025, featuring enhanced modularity, stealth, and persistence for advanced attacks.
Coinbase suffered a data breach impacting 69,000 customers, linked to a third-party contractor. Personal info was leaked, raising security concerns.

Mozilla's Firefox Add-ons now auto-detects malicious crypto wallet extensions, enhancing user security and preventing theft.

Crocodilus, a rapidly evolving Android banking trojan, now targets global users, stealing crypto seed phrases and bypassing defenses.

Socket discovers 4 malicious npm packages designed to drain crypto wallets on BSC & Ethereum, downloaded over 2,100 times.

BitoPro confirms $11.5M hot wallet cyberattack after investigator @zachxbt exposed the theft. User funds are safe, but initial silence raises concerns.

BitMEX security team infiltrates Lazarus Group's infrastructure after a phishing attempt, exposing their tactics and even a hacker's real location.

A sophisticated PyPI supply chain attack, "cappership," steals Solana private keys by monkey-patching, leveraging transitive dependencies and blockchain exfiltration.

Katz Stealer, a new MaaS infostealer, targets browsers, crypto wallets, and Discord using advanced evasion and UAC bypass techniques.

Deceptive VS Code extensions like 'solaibot' are stealing crypto wallet credentials, disabling Defender, and deploying persistent spyware on Windows.

An Alabama man faces prison for a brazen SIM swap attack that hijacked the SEC's X account, falsely announcing a Bitcoin ETF and crashing crypto markets.

A malicious PyPI package named 'solana-token' targeted Solana developers to steal code and secrets. Learn how it worked and how to stay safe.

Massive FreeDrain crypto phishing campaign uses Google SEO and free hosting to steal wallets. Trezor, Ledger users beware!

Watch out! Sophisticated Facebook ads lure crypto users to download malware via fake platforms and celebrity endorsements. Bitdefender warns of data theft.

German authorities shut down the crypto-swapping platform eXch, a hub for laundering illicit funds, and seized €34 million in cryptocurrencies after tracing stolen Bybit funds.

Inferno Drainer returns stronger than ever, using Discord phishing and blockchain obfuscation to steal millions in crypto.

Silent Push uncovers Lazarus Group's campaign using fake crypto job offers to spread malware (BeaverTail, InvisibleFerret, OtterCookie), targeting job seekers.
Malicious open-source packages are stealing crypto wallet credentials! Learn about the threat and how to protect your seed phrases and private keys.

EU & US sanctions hit Garantex, Russia's crypto exchange, freezing $30M in USDT. Russia now seeks a domestic stablecoin to bypass restrictions.
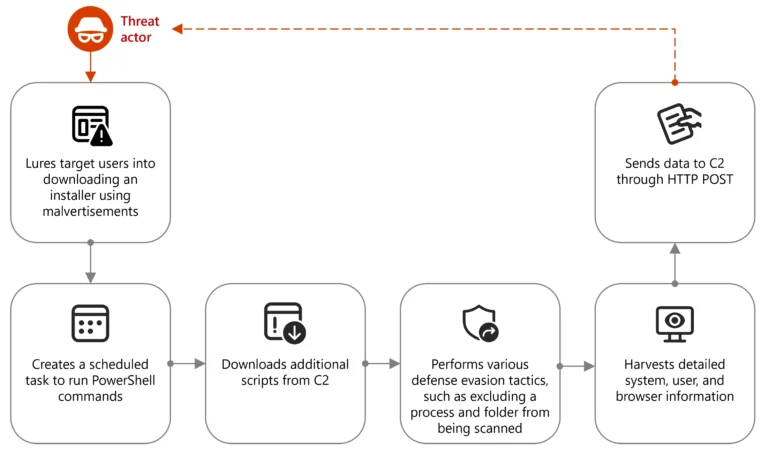
Threat actors abuse Node.js in malvertising campaigns to steal data and deliver malware via fake crypto installers and stealthy PowerShell scripts.