
 Do Son
A massive fire at an AWS facility in Bahrain highlights a dangerous shift toward kinetic strikes on cloud infrastructure. Is your multi-region strategy ready?
geopolitics

A new Data Abyss report reveals how PRC-affiliated entities systematically exploited U.S. IARPA research to advance China's military capabilities.

Recorded Future’s Insikt Group warns of a two-year escalation in Russian hybrid warfare. From cyber sabotage to airspace incursions, NATO faces a new doctrine.
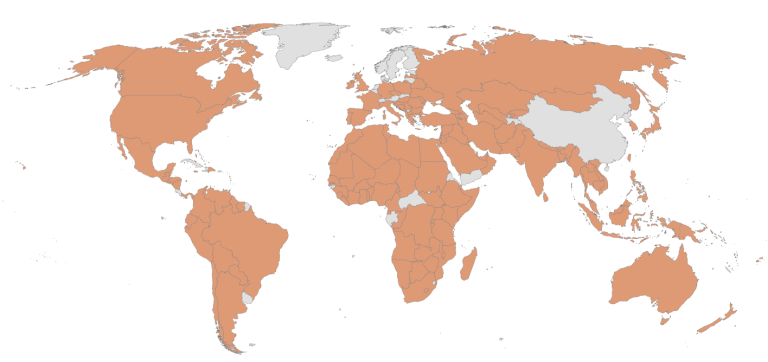
TGR-STA-1030 (UNC6619) hits 70+ orgs in 37 countries. The Asia-based group uses the new ShadowGuard eBPF rootkit to hide in Linux kernels.

NCSC warns of Russian group NoName057(16) targeting UK sectors with DDoS attacks. Defenders must ensure scalability and plan for graceful degradation.

TSMC’s 2nm is fully booked! Samsung’s Taylor, Texas fab aims to steal the lead in 2026 as AMD, Google, and Tesla seek an American-made 2nm alternative.
China's SAMR launched an antitrust probe into Qualcomm for acquiring Autotalks without filing a mandatory "operator concentration declaration," violating the Anti-Monopoly Law.

NVIDIA's CFO has stated the company will not pay the U.S. government a 15% revenue share on China sales unless the agreement is formally codified into law.

The U.S. government has converted a portion of Intel's subsidies into a direct equity investment, acquiring a 9.9% stake in the company for $8.9 billion.

NVIDIA has ordered suppliers to halt production of its H20 AI chip for China, a move that highlights how technology has become a central battleground in global politics.
ShadowSyndicate’s Global Ransomware Empire Blurs Lines Between Cybercrime and Geopolitical Espionage

ShadowSyndicate’s Global Ransomware Empire Blurs Lines Between Cybercrime and Geopolitical Espionage
A new report exposes ShadowSyndicate, a sophisticated cybercrime group tied to top-tier RaaS affiliates, bulletproof hosting, and suspected geopolitical influence operations, blurring lines between cybercrime and espionage.

A new report traces China's cyber power to the "Red Hackers" of the 1990s and 2000s, who laid the groundwork for its sophisticated state-backed operations.

The FCC will vote on August 7 to ban Chinese tech in US undersea cables, aiming to boost national security after the 2024 "Salt Typhoon" cyberattack and curb China's digital influence.

Iranian-backed "Pay2Key.I2P" ransomware resurfaced on I2P, offering 80% profit for attacks on Western targets. Linked to Fox Kitten & Mimic, it merges cybercrime with geopolitical motives.

TRM Labs' analysis of the Nobitex hack reveals Iran's crypto exchange was engineered for sanctions evasion, featuring deep fiat integration and blockchain obfuscation to defy surveillance.
CISA, FBI, NSA, and DC3 warn of potential cyberattacks from Iranian-affiliated actors on vulnerable U.S. infrastructure and networks, urging vigilance despite recent ceasefires.

Russia has begun systematically blocking Cloudflare, throttling internet connections to 16KB after the initial download, impacting vast numbers of websites and other major hosting providers.
Canada has ordered Hikvision to shut down nationwide, citing national security concerns. The ban prohibits government use of its products, but Hikvision calls it baseless and biased.

Pro-Iranian group Cyber Fattah leaked thousands of sensitive Saudi Games participant records, including PII and bank data, in a political information operation targeting Saudi Arabia.

Iran has drastically cut internet connectivity to 3% nationwide, citing Israeli cyberattacks. The blackout includes international calls, affecting millions amid rising tensions.

Proofpoint reveals TA397 (Bitter APT) is an India-aligned state-backed group conducting long-term espionage campaigns globally, targeting rivals and partners.

North Korean threat actor TA406 intensifies cyber espionage against Ukraine, using phishing and malware to gather political intelligence.