 Do Son
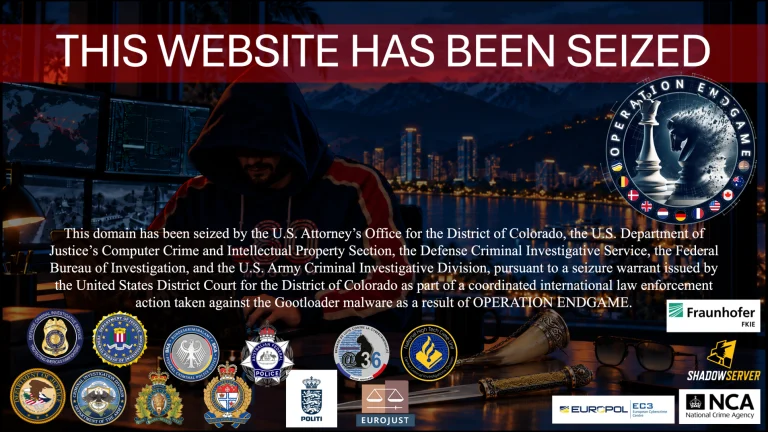
The DOJ and FBI executed a Gootloader malware takedown, wiping the botnet from 100+ WordPress servers after 25,000 infections and $28.8M in losses.
wordpress
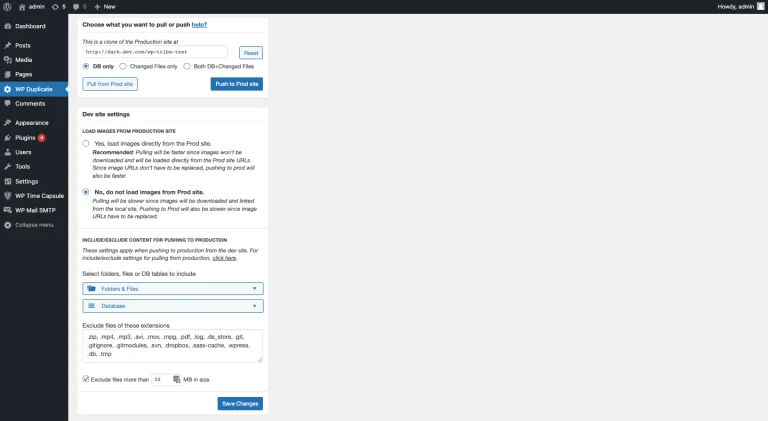
WP Duplicate vulnerability CVE-2026-123751 is exploited in the wild, letting attackers upload files and run code. No patch exists, so remove the plugin.
Our weekly CVE report for Nov 2-8, 2026 tracks 3,570 new CVEs and 10 exploited vulnerabilities, including Siemens and Zyxel flaws not in CISA KEV.
A critical WordPress Core vulnerability is exploited in the wild. Update to WordPress 7.1.4 immediately to fix the unauthenticated race condition RCE.
WordPress 7.1.4 security release fixes 17 issues, including a core update race condition RCE and ten stored XSS bugs. Update your sites now.
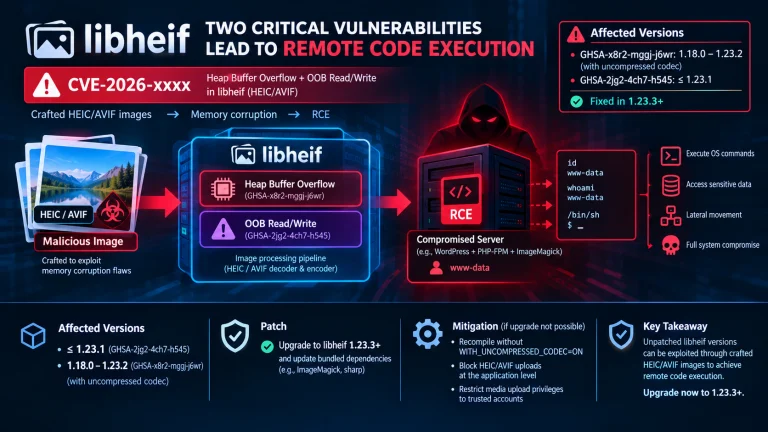
Details and PoC exploit code are out for critical libheif vulnerabilities GHSA-x8r2-mggj-j6wr and GHSA-2jg2-4ch7-h545. Upgrade to 1.23.3 now.
Hackers exploit YOOtheme Pro vulnerability CVE-2026-102785 (CVSS 10) for remote code execution, dropping webshells. Update to 5.0.53 now.
Update the Duplicator WordPress plugin to 5.0.0 to fix CVE-2026-82814, a high-severity PHP Object Injection flaw risking RCE and site takeover.
UpdraftPlus data breach exposed customer data and keys now used in an UpdraftCentral backdoor campaign. Update to 1.26.12 and check your sites.
Update Rank Math SEO PRO to 3.0.124 now. CVE-2026-111862 is a critical supply-chain compromise actively exploited in the wild via embedded malware.
Update the Backuply WordPress plugin to 1.5.9 to fix CVE-2026-93953, a high-severity SQL injection vulnerability impacting 600,000 sites.
An active WordPress XSS campaign exploits Ninja Forms flaw CVE-2026-94504 and CVE-2026-93836 to plant hidden admin accounts. Patch now.
The WordPress 7.1.3 security update is a WordPress security release that fixes stored XSS, SQL injection and more. Update your site now.
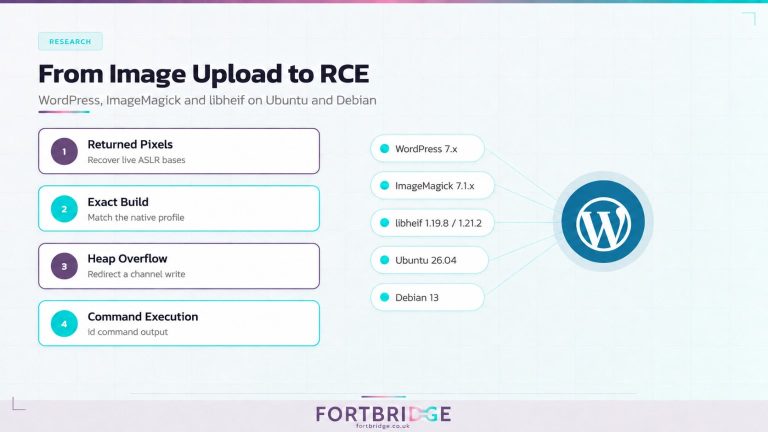
A WordPress libheif RCE chain and its PoC are now public. The libheif vulnerability turns an HEIC upload into code execution. Patch to 1.23.3.
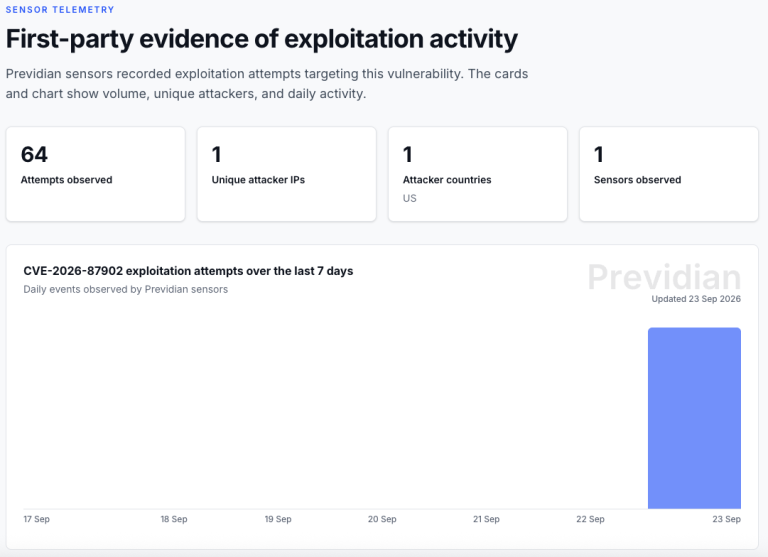
An exploited WordPress RCE vulnerability (CVE-2026-87902) is under attack. Details and PoC exploit code are public. Patch your sites now.

Details and PoC exploit code for a critical WordPress stored XSS are public. Learn how CVE-2026-93485 enables RCE and patch WordPress today.
WordPress 7.1.2 patches a critical WordPress RCE vulnerability (CVE-2026-87902). Update your site to prevent conditional remote code execution.
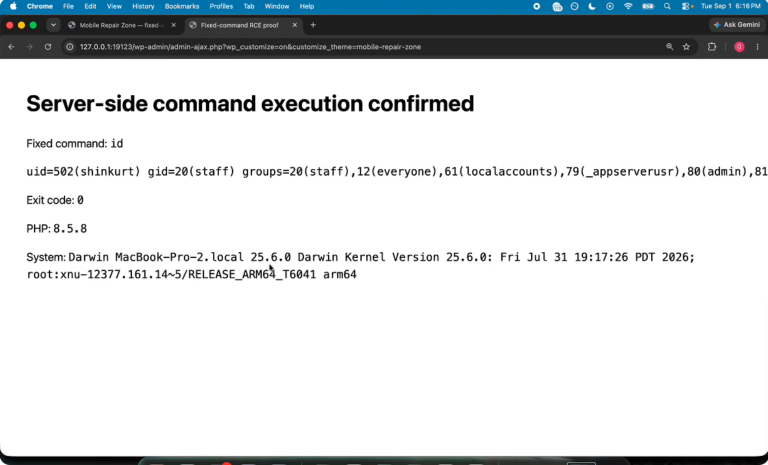
The WordPress Click2Shell vulnerability enables remote code execution via theme preview injection. Learn how this flaw works and update to version 7.1.1.
The WordPress 7.1.1 security release fixes 11 flaws, including stored cross-site scripting and path traversal. Update your sites immediately.
A critical The Events Calendar vulnerability is exploited in the wild. Patch The Events Calendar vulnerability now to stop remote code execution.
Attackers are actively exploiting a critical WooCommerce Wholesale Lead Capture vulnerability. Patch WooCommerce Wholesale Lead Capture now.
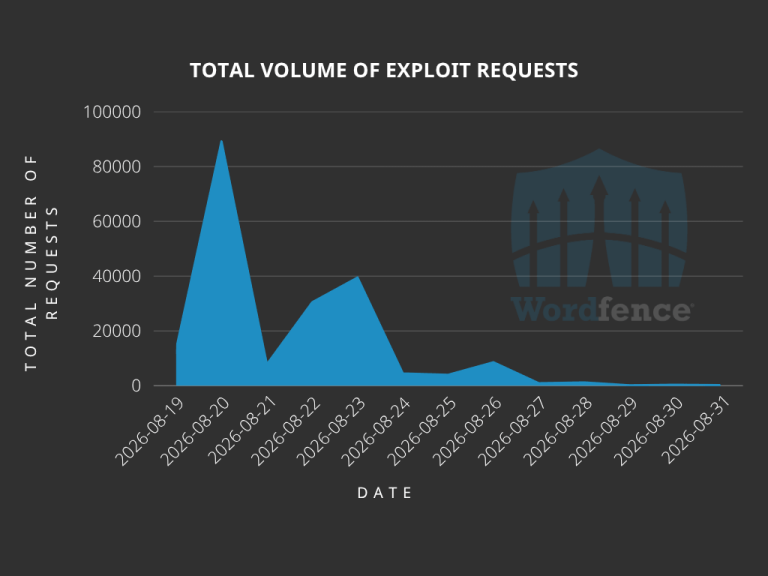
Attackers exploit a critical Elementor Pro vulnerability (CVE-2026-32475) in the wild. Patch this Elementor Pro vulnerability to prevent site takeover.