 Do Son
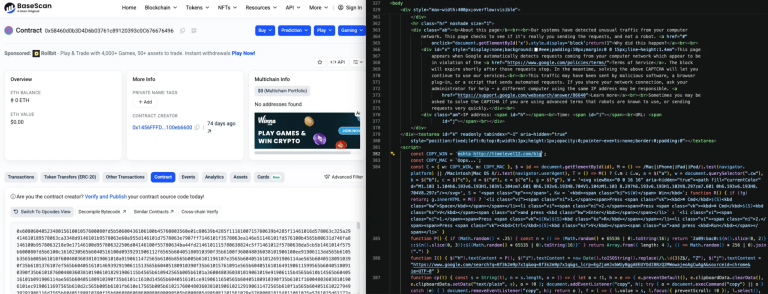
A new Amatera password stealer campaign abuses WordPress and EtherHiding. Learn how this Amatera password stealer infects browsers.
wordpress
CVE-2026-19598 (CVSS 9.8) in the Pods WordPress plugin enables complete site takeover. Wordfence is blocking attacks in the wild. Update now.
CVE-2026-32475 (CVSS 9.8) is an Elementor Pro arbitrary file upload flaw risking complete site compromise across 6 million WordPress sites. Update to 4.2.2.

CVE-2026-18051 (CVSS 10) is an unauthenticated arbitrary file write in W3 Total Cache, exposing 900k+ WordPress sites. Update to 2.10.5.

CVE-2026-15748, a CVSS 9.8 flaw in Forminator Forms, lets unauthenticated attackers upload PHP files for pre-auth RCE. Update to 1.56.2 now.

WordPress 7.0.4 patches CVE-2026-65640, an Author-level remote code execution bug on sites using Imagick and Ghostscript. Update now.

WordPress 7.0.3 fixes CVE-2026-64638, a pre-auth XSS on the login screen that can escalate to remote code execution. CVSS 8.9. Update now.

Active exploitation of CVE-2026-18072, a CVSS 9.8 video embedder backdoor, grants attackers full administrative control over 20,000 WordPress sites.

CISA added four flaws to its KEV catalog, including WordPress RCE (CVE-2026-63030) and Langflow RCE (CVE-2026-0770). All are exploited in the wild.
Cloudflare deploys emergency WAF rules to block the critical WordPress wp2shell vulnerability. Update your site now to prevent severe RCE security risks.
WordPress pre-auth RCE CVE-2026-63030 chains a REST batch bug with SQL injection. Details and a public PoC are out. Update to WordPress 7.0.2 now.
Australia's ACSC warns of a large-scale CMS exploitation campaign. Attackers exploit WordPress and CMS bugs to plant webshells on websites.
ErrTraffic malware powers ClickFix attacks on hacked WordPress sites, using EtherHiding on the blockchain to hide its C2 and spread infostealers.
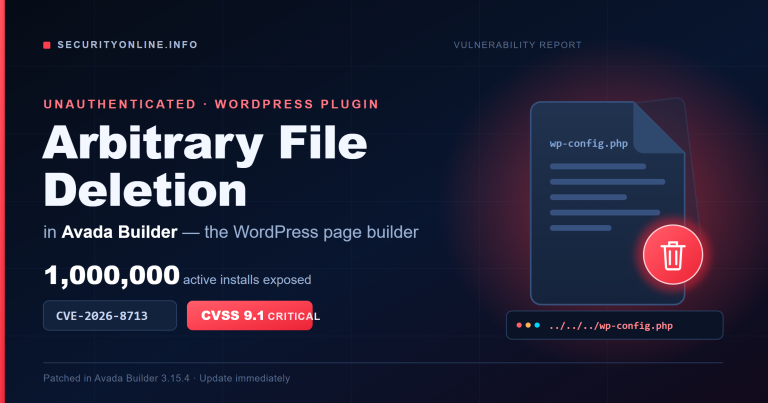
CVE-2026-8713 is a critical Avada Builder vulnerability enabling unauthenticated arbitrary file deletion on 1M WordPress sites. Update to 3.15.4 now.
Attackers are actively exploiting a critical Gravity SMTP vulnerability (CVE-2026-4020) causing sensitive information exposure. Update your plugin now.
A ShapedPlugin supply chain attack (CVE-2026-10735) injected malware into WordPress Pro plugins. Discover the impact and how to protect your site today.
The Uncanny Automator breach exposed customer data and pushed a backdoored plugin build (7.3.0.5). Here's what happened and how to secure your site.
A critical UpdraftPlus CVE-2026-10795 vulnerability threatens 3 million sites. Hackers are exploiting this UpdraftPlus authentication bypass in the wild.
A critical 9.8 CVSS vulnerability in the Temporary Login plugin puts 40,000+ WordPress sites at risk of account takeover. Patch to version 1.1.0 now!
A critical 8.1 CVSS flaw in Perfmatters (200k+ installs) allows unauthenticated attackers to delete wp-config.php and hijack sites. Update to 2.6.0 now!
WordPress.com launches a Persistent AI Assistant to handle CSS, font styling, and image editing. Turn natural language into a professional site design instantly.

New "directory shadowing" malware creates physical folders to hijack WordPress URLs. It feeds gambling spam to Googlebots while staying invisible.