
 Do Son
Week of April 7-13 saw critical Ivanti, WordPress, & Windows vulnerabilities exploited, plus major data breaches impacting millions.
wordpress

A critical vulnerability in the Everest Forms WordPress plugin allows unauthenticated attackers to inject PHP Objects. Update to version 3.1.2 immediately to protect your site.

A critical vulnerability in the InstaWP Connect WordPress plugin allows unauthenticated attackers to include and execute arbitrary files. Update to version 0.1.0.86 immediately.

A critical vulnerability (CVE-2025-3102) in the SureTriggers WordPress plugin allows unauthenticated admin account creation, potentially exposing over 100,000 sites to full takeover. Update to version 1.0.79 immediately.

CVE-2025-2075 exposes over 50,000 WordPress sites to attacks. Learn how this vulnerability affects your website's security.

Explore CVE-2025-2563, a critical vulnerability in the User Registration & Membership plugin that can allow unauthorized access.

Learn about CVE-2025-2505, a critical vulnerability in the Age Gate plugin for WordPress that allows remote code execution.

Learn about CVE-2025-1661, a critical vulnerability in the HUSKY plugin that puts over 100,000 WordPress stores at risk.
Learn about CVE-2025-26776, a critical vulnerability in Chaty Pro that can lead to website takeover for over 18,000 users.

Learn about CVE-2025-0912, a severe security vulnerability in GiveWP affecting over 100,000 WordPress sites.

Discover the serious security flaw CVE-2025-24752 in Essential Addons for Elementor that threatens millions of websites.
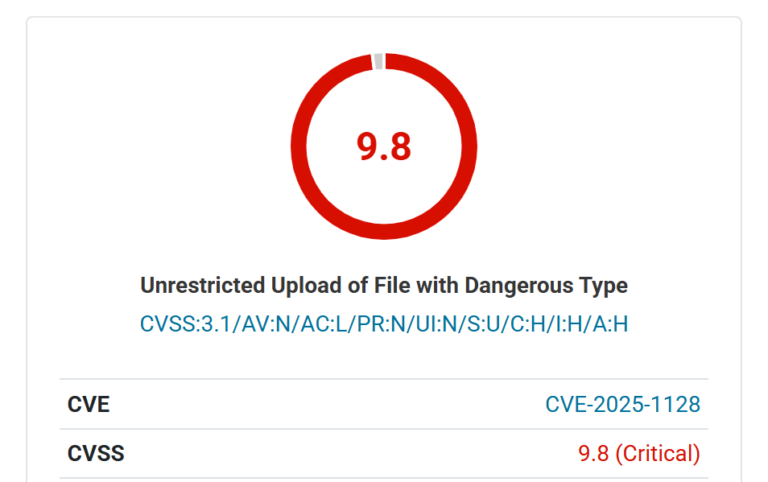
Urgent: CVE-2025-1128 affects Everest Forms. Find out how to prevent site compromise by updating to the latest version.

Learn about CVE-2024-12562, a critical vulnerability in s2Member Pro that exposes millions of WordPress sites to risk.

CVE-2024-10960 poses a severe risk for WordPress users. Discover how this vulnerability affects site security.

Learn about CVE-2024-13365, a critical vulnerability affecting WordPress that could compromise over 30,000 websites.

Protect your WordPress site from critical security vulnerabilities in the Real Homes theme and Easy Real Estate plugin. Learn how to secure your site from CVE-2024-32444 & CVE-2024-32555.

Learn about the critical security flaw found in the W3 Total Cache plugin and how it puts over a million WordPress websites at risk (CVE-2024-12365).

Protect your WordPress website from the WP3.XYZ malware attack. Learn how to detect and prevent unauthorized admin accounts, malicious plugins, and data exfiltration.

Discover the latest cyberattack on GroupGreeting.com. Learn about the sophisticated JavaScript injection techniques used in the “zqxq” campaign.
Stay informed about the latest credit card skimming malware targeting WordPress checkout pages. Learn how this sophisticated malware evades detection and steals sensitive payment details.

Beware of PhishWP: a dangerous WordPress plugin that disguises itself as a legitimate tool but actually steals your sensitive information.

Find out how the CVE-2024-10957 vulnerability in the UpdraftPlus Backup & Migration plugin exposed WordPress sites to potential attacks.