
 Do Son
Get the latest on the WordPress.org suspension. Learn about the impact on users and developers and the ongoing negotiations.
wordpress

Uncover the severe WordPress vulnerability, CVE-2024-11972, allowing attackers to bypass permission checks and install plugins directly from the repository.
CVE-2024-10542 and CVE-2024-10781 could allow unauthenticated attackers to compromise websites by installing malicious plugins & executing arbitrary code

Learn about the CVE-2024-9511 vulnerability in FluentSMTP WordPress plugin, which could lead to remote code execution on vulnerable websites.
Discover the sophisticated PHP reinfector malware affecting WordPress sites. Find out how it reinfects files, plugins, and critical database tables.

Critical vulnerability alert: Learn about CVE-2024-10924, an authentication bypass vulnerability found in the Really Simple Security plugin for WordPress

Discover the critical security flaw in LiteSpeed Cache plugin for WordPress. Learn about CVE-2024-50550 and how it can compromise your site's security

Critical vulnerability in wpDiscuz plugin (CVE-2024-9488). Learn how unauthenticated attackers can hijack user accounts in WordPress.

Be aware of the PHP Object Injection flaw (CVE-2024-9634) in GiveWP plugin. Protect your website and donor data from potential exploitation.

Learn about the recent Jetpack vulnerability and the urgent need to update. Safeguard your website from potential security risks today.
Stay alert! Over 100,000 websites at risk due to CVE-2024-43917 in TI WooCommerce Wishlist. Learn how to mitigate the risk and secure your site.

Uncover the critical vulnerabilities in Jupiter X Core WordPress plugin. Learn how these flaws can put your website at risk and how to mitigate them.
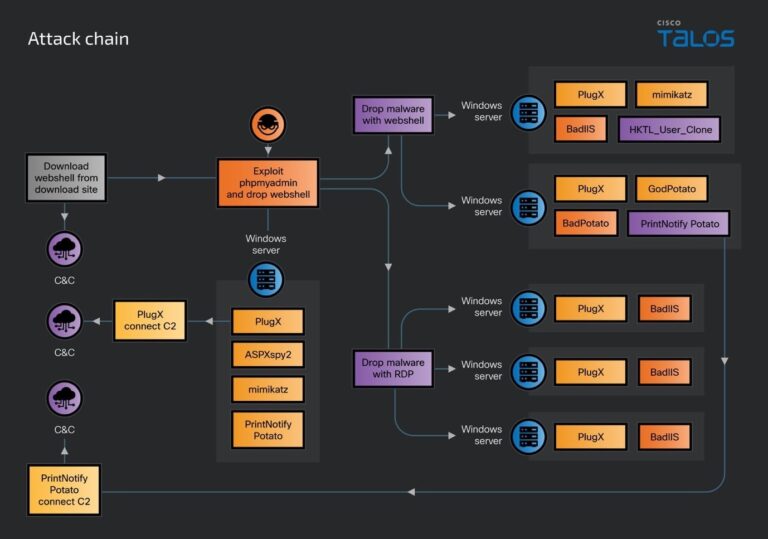
Learn about DragonRank, a Chinese threat actor specializing in SEO manipulation and cyberattacks. Find out how this group compromises websites and manipulates search engine rankings.

Uncover the advanced malware campaign known as DarkCracks. Learn how it exploits vulnerabilities in GLPI and WordPress websites for stealthy control.

Discover the severe security flaw in LiteSpeed Cache plugin for WordPress (CVE-2024-44000) and its potential implications for your site's security.

Learn about the severe security flaw (CVE-2024-6386) in WPML plugin for WordPress and its potential risks to over one million websites.

Optimize your vulnerability management with Vuls, an automated solution designed to streamline the process of identifying and patching vulnerabilities.

CVE-2024-6457 leaves over 100,000 WooCommerce-powered online stores susceptible to unauthorized data breaches
Security researcher John Castro has uncovered a critical vulnerability (CVE-2024-6695) in Profile Builder, a widely used WordPress plugin

A severe vulnerability (CVE-2024-5441) has been discovered in the widely used WordPress plugin Modern Events Calendar

A critical vulnerability tracked as CVE-2024-5488 has been discovered in SEOPress, a popular WordPress plugin with over 300,000 active installations

WordPress has released a critical security update to address three vulnerabilities that could potentially expose millions of websites to cyber attacks