 Do Son
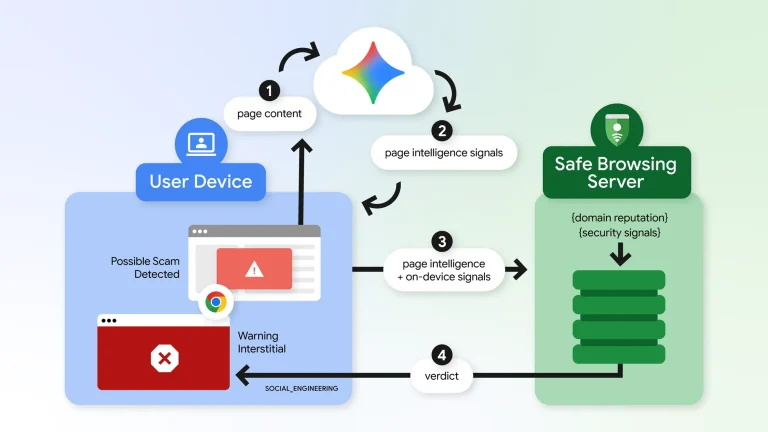
Chrome ClickFix protection in Enhanced Protection flags risky clipboard commands and uses cloud Gemini AI to block scam sites.
powershell

Discover why Microsoft is deprecating slmgr.vbs and learn how to transition your Windows activation PowerShell workflows for future system management.
Microsoft warns of rising ACR Stealer attacks using ClickFix lures to steal browser credentials and tokens from enterprises. Two chains detailed.

BlueNoroff uses a "self-reinforcing" deepfake pipeline to target crypto CEOs. Fake Zoom meetings and stolen footage lead to a 5-minute system compromise.
Rapid7 uncovers a fake Claude AI installer using ClickFix techniques to bypass AMSI and inject shellcode. Stay safe from this sophisticated AI-themed threat.

Proofpoint monitors a 30-day supply chain attack using "signing-as-a-service" to bypass Windows security. Protect your load boards and fleet payments now.

Microsoft has officially raised the FAT32 formatting limit to 2TB in Windows 11. Say goodbye to the 32GB restriction and third-party tools like Rufus.

Kaspersky reveals a fileless Trojan campaign targeting Proxifier searches. Learn how this "ClipBanker" hijacks crypto wallets via search engine poisoning.
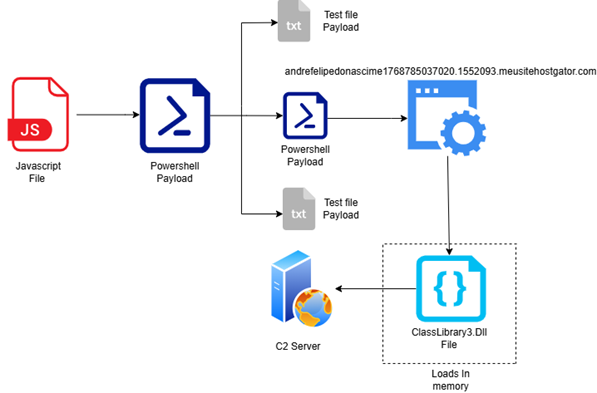
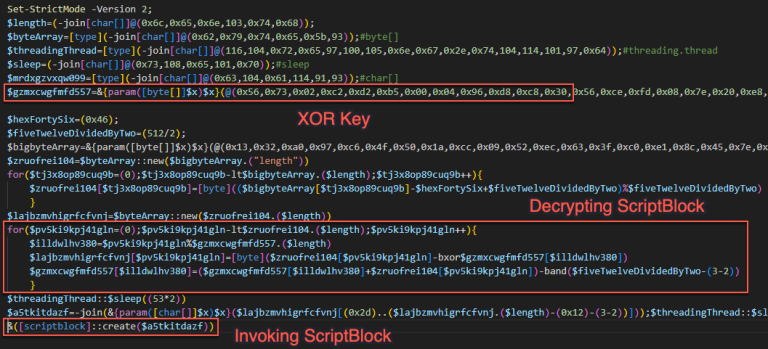
Lat61 Team uncovers DesckVB RAT, a stealthy 2026 Trojan using in-memory .NET loaders & JS obfuscation to hijack systems and evade AV. Learn how it works.
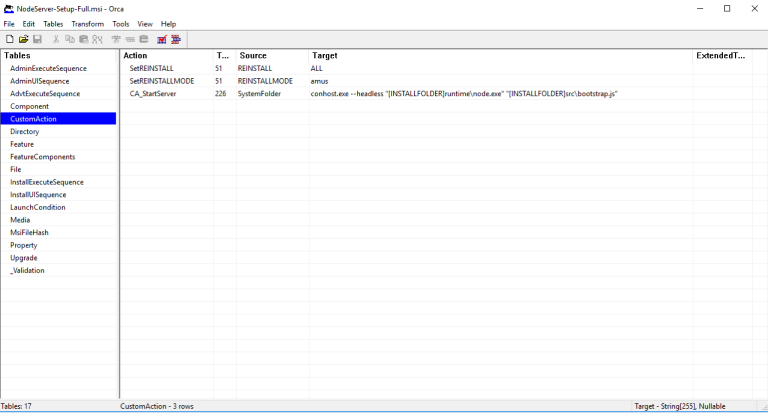
Netskope uncovers a Node.js-based ClickFix campaign using gRPC over Tor for stealthy crypto theft. A leaked file exposed their entire MaaS backend.
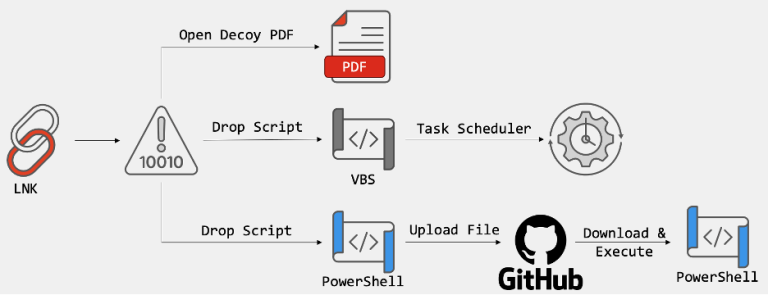
FortiGuard Labs unmasks a South Korean espionage wave abusing the GitHub API for C2 and using LNK files to stay invisible. Protect your network from LotL.

ASEC uncovers Kimsuky’s evolved LNK-to-Python chain abusing Dropbox for stealthy persistence. Learn how to detect this complex multi-stage backdoor.
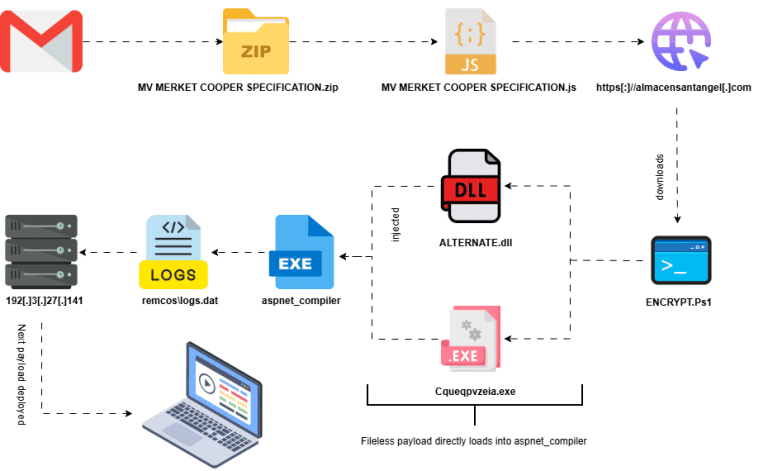
Researchers unmask a fileless Remcos RAT campaign using obfuscated JS and LOLBins to hijack systems in-memory. See the technical breakdown from Lat61.

LevelBlue SpiderLabs unmasks the PhantomVAI framework: a multi-stage, fileless attack hiding XWorm and Remcos RAT inside obfuscated VBS and PNG files.

Apple’s macOS Tahoe 26.4 introduces a "Paste Block" to stop terminal-based phishing. Learn how this 2026 security feature thwarts malicious PowerShell scripts.

Elastic Security Labs uncovers SILENTCONNECT, a stealthy loader using Cloudflare and Google Drive to deliver RMM tools for "hands-on keyboard" attacks.
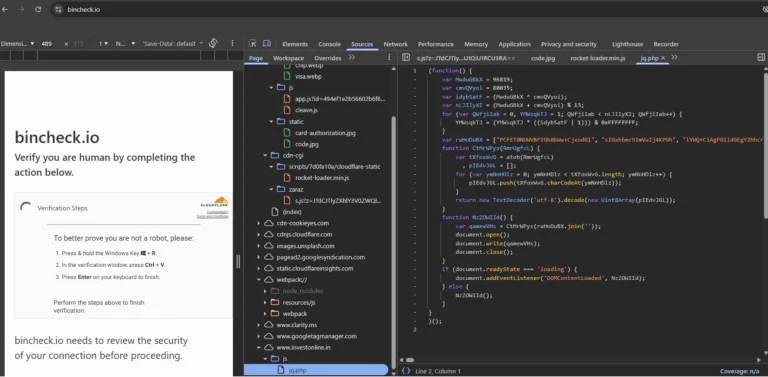
Elastic Security Labs uncovers a ClickFix campaign turning human helpfulness into a weapon. Fake verifications deploy the fileless MIMICRAT via PowerShell.
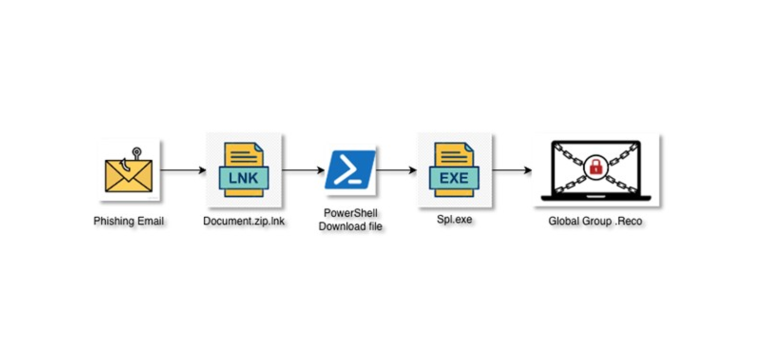
Phorpiex botnet returns in "Your Document" phishing campaign. Attackers use malicious .LNK files and hidden extensions to trick users.
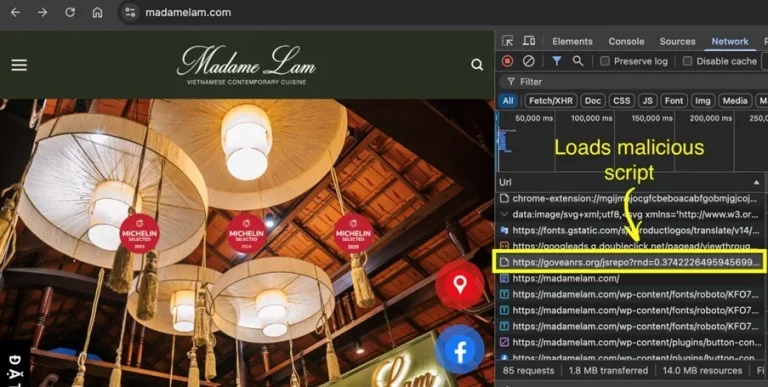
LevelBlue warns of StealC malware using "ClickFix" fake CAPTCHAs. Users are tricked into running fileless malware via PowerShell. Stay alert.

Phishing emails use malicious Excel files to deploy XWorm RAT. The fileless attack exploits CVE-2018-0802 to steal data & control systems.

IClickFix malware hijacks 3,800+ WordPress sites with fake Cloudflare CAPTCHAs. This watering hole attack tricks users into running malicious PowerShell.

New Fake CAPTCHA campaign uses Google Calendar & steganography to drop Amatera Stealer. See how this attack exploits legitimate Windows tools to stay hidden.