
 Do Son
Securonix reveals SHADOW#REACTOR: A stealthy framework using "text-only" fragments to deploy Remcos RAT in memory via MSBuild. Avoids disk detection.
powershell

Microsoft Defender's new FakeMas filter is erroneously blocking the official MAS activation script due to a typosquatted domain war. Learn the fix.

Attackers are using a fake MAS domain (get.activate.win) to deploy Cosmali Loader and XWorm RAT via PowerShell. Verify your command before running it!

MAS is ditching Batch for PowerShell! Discover how the new roadmap optimizes Windows 10 & 11 activation while maintaining a legacy branch for older systems.

Gen Digital uncovers AuraStealer, a new infostealer using TikTok "Scam-Yourself" tactics to trick users into infecting their own Windows PCs.

Phantom v3.5 info-stealer targets passwords and crypto via a fake Adobe installer. It uses SMTP to exfiltrate data directly to attackers.

A critical OS Command Injection (CVE-2025-68154) in the systeminformation Node.js library risks RCE on Windows. Affects 16M+ users. Upgrade to v5.27.14.

A movie torrent scam uses a DiCaprio film lure to infect PCs with Agent Tesla RAT. The attack chain uses LNK files and malicious code hidden in a subtitle file to achieve fileless execution via LotL tools.

Microsoft patched 72 flaws, including three zero-days. Fixes target a Cloud Files UAF exploited for SYSTEM privileges and an RCE in GitHub Copilot. PowerShell gets a new security prompt.

The JS#SMUGGLER campaign uses "Junk Code" JavaScript and fileless PowerShell executed via mshta.exe to bypass EDR. This multi-stage attack silently installs the NetSupport RAT.

eSentire exposed the Amatera Stealer campaign using ClickFix social engineering to deliver multi-stage PowerShell. The malware patches AMSI in memory and deploys NetSupport RAT for remote access.

Unit 42 exposed Airstalk, a suspected nation-state malware that abuses VMware AirWatch (MDM) APIs for a covert C2 dead drop. The tool is used to steal credentials and browser data in supply chain attacks.

Trend exposed the Water Saci worm, a self-propagating campaign that hijacks WhatsApp Web using Selenium/PowerShell. It uses a stealthy IMAP email C2 channel with HTTP fallback.
NetSupport RAT Campaign Abuses ClickFix to Infect Hosts; 3 Threat Clusters Use RMM for Covert Access

NetSupport RAT Campaign Abuses ClickFix to Infect Hosts; 3 Threat Clusters Use RMM for Covert Access
eSentire exposed a surge in NetSupport RAT campaigns using the ClickFix social engineering tactic. Three threat clusters leverage a PowerShell loader to bypass AV and gain full remote access via the RMM tool.

SentinelLABS exposed PhantomCaptcha, a ClickFix campaign targeting Ukraine NGOs. It uses a fake Cloudflare CAPTCHA to deploy a multi-stage PowerShell WebSocket RAT and a parallel Android spyware attack.

Expel uncovered a phishing attack using Cache Smuggling to deliver malware. The technique uses a fake Fortinet lure and PowerShell to execute a payload staged in the browser's cache, bypassing network detection.

A new campaign uses a malicious LNK shortcut sent via Discord to deploy a multi-functional RAT that hijacks legitimate Windows binaries to evade detection.

Microsoft has permanently removed the outdated and insecure PowerShell 2.0 from Windows 11, a move that enhances security but may affect some enterprise scripts.

A new report from Cisco Talos details PS1Bot, a modular PowerShell-based malware campaign using malvertising to steal data and maintain stealthy persistence.

A targeted phishing campaign against Israeli organizations uses a PowerShell-based RAT and compromised internal emails for delivery, making detection difficult.
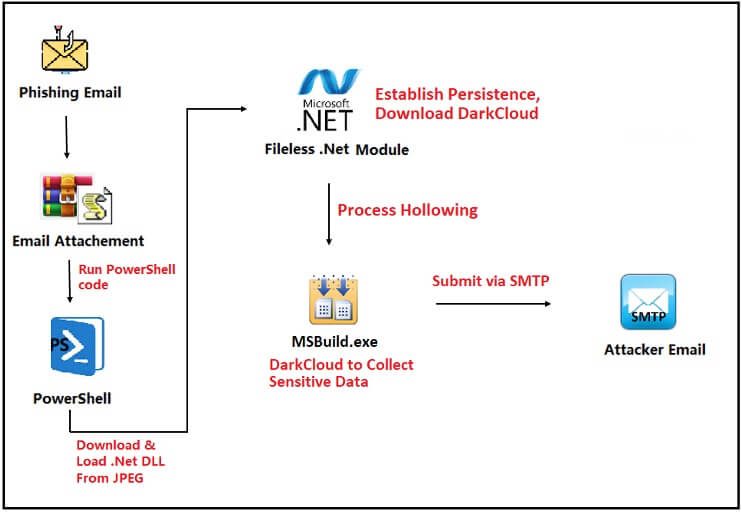
Fortinet uncovers a new DarkCloud stealer variant using a fileless, multi-stage attack chain with obfuscated PowerShell and process hollowing to evade detection and exfiltrate data.

Unit 42 uncovers DarkCloud Stealer's new evasion tactics, including heavily obfuscated JavaScript/WSF loaders and a final VB6 payload that injects into RegAsm.exe to bypass detection.