
 Do Son
Threat actors are using the PyBitmessage protocol as a stealthy C2 channel to hide a Monero coinminer and backdoor, evading detection.
powershell

Horabot malware targets Latin America with fake invoices, hijacking Outlook to spread phishing emails and steal data via stealthy scripting.

Beware! Cybercriminals are using fake CAPTCHA pages to trick you into running commands that install the dangerous Lumma Stealer malware.

Netskope Labs details a complex infection chain used by the DOGE Big Balls Ransomware, involving PowerShell scripts, exploits, and lateral movement tactics.

Kimsuky revives PebbleDash malware using spear-phishing and patched RDP DLLs for stealthy access and control, warns new ASEC March 2025 report.
FOG ransomware campaign spreads via phishing and stealthy loaders, targeting tech, education, and manufacturing sectors with obfuscated payloads.
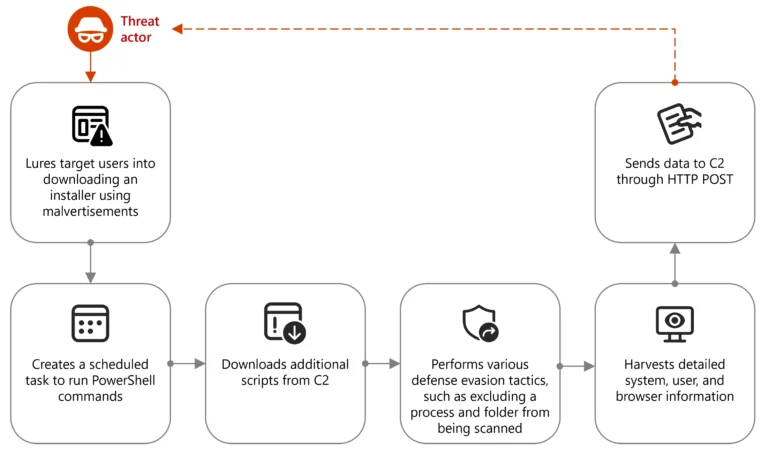
Threat actors abuse Node.js in malvertising campaigns to steal data and deliver malware via fake crypto installers and stealthy PowerShell scripts.

ViperSoftX malware is being used by Arabic-speaking attackers to target South Korea, according to ASEC. This malware uses PowerShell and spreads through torrents, delivering PureCrypter and Quasar RAT

Explore the dangers of Konni RAT, a sophisticated Remote Access Trojan targeting Windows systems with multi-stage attacks.

Discover how Arcane Stealer exploits gamers by distributing malware via fake game cheat videos on YouTube.

Uncover the latest variant of ClearFake malware, EtherHiding, exploiting Web3 features for advanced malicious tactics.

Explore CVE-2025-27636, a crucial vulnerability in Apache Camel that could lead to severe security risks and remote code execution.

Uncover the details of the Phantom Goblin malware campaign that uses social engineering to steal browser credentials.

Explore EncryptHub's attacks and discover how EncryptRAT utilizes trojanized applications to compromise systems effectively.

Learn how YouTube is being exploited to spread malware through deceptive links shared by YouTubers and hackers.

Learn about the ISP Infostealer Campaign and its severe impacts on ISP infrastructure through brute force and data exfiltration.

Discover the latest cyber threat: RedCurl APT group. Learn about their sophisticated techniques and targeted cyber espionage campaigns.

Uncover the stealthy techniques threat actors are using: LNK files and SSH commands in advanced cyberattacks.

Find out how the NodeStealer infostealer has evolved to target Facebook Ads Manager and collect crucial financial information using Facebook’s Graph API.

Learn about a complex PowerShell campaign that employs advanced techniques to infiltrate networks, maintain persistence, and evade detection.

Discover the rise of cyberattacks by Earth Simnavaz. Find out how this Iranian-linked group targets the energy sector in the Gulf region.

Uncover the details of a sophisticated AsyncRAT campaign utilizing Bitbucket. Learn how attackers distributed malicious payloads and evaded detection.