
 Do Son
eSentire exposes Interlock, a new ransomware group using multi-stage payloads and the ClickFix social engineering technique to deploy ransomware and backdoors via compromised websites.
powershell

Cisco Talos' Q2 2025 report reveals phishing is the top access method. Ransomware, including Qilin, dominated, with a surprising trend of attackers abusing PowerShell 1.0 to evade security.

Trellix uncovers 0bj3ctivityStealer, a sophisticated info-stealer using phishing, custom PowerShell, and steganography to evade detection and exfiltrate sensitive data.

A new stealthy campaign uses Windows LNK files to deploy the REMCOS backdoor via multi-stage PowerShell commands, bypassing antivirus and gaining full system control.

Trend Micro uncovers BERT ransomware (Water Pombero) deploying multi-threaded variants against Windows, Linux, and ESXi systems, showing code similarities to REvil's Linux variant.
Splunk exposes a campaign weaponizing Inno Setup installers to deploy RedLine Stealer, using obfuscated Pascal scripts and HijackLoader to steal browser/crypto data.

XMRig cryptojacking is surging, leveraging LOLBAS techniques, PowerShell, and Scheduled Tasks to mine Monero undetected, with a 45% rally in XMR price driving the attacks.

ASEC uncovers XwormRAT delivered via phishing emails using steganography, hiding sophisticated .NET malware within JPG images for stealthy execution and full system control.

North Korean APT Kimsuky is evolving its ClickFix tactics, using deceptive social engineering, fake job portals, and obfuscated PowerShell to compromise targets via spear-phishing campaigns.

North Korean APT Kimsuky is using GitHub private repos, Dropbox, and XenoRAT malware via spearphishing to compromise victims and conduct cyber-espionage.

KimJongRAT is back with new PE and PowerShell variants, using LNK files and CDNs to steal browser, email, and over 30 crypto wallet details from victims.

A fileless AsyncRAT campaign, dubbed "Clickfix," targets German-speaking users, luring them into executing obfuscated PowerShell payloads via fake verification prompts.
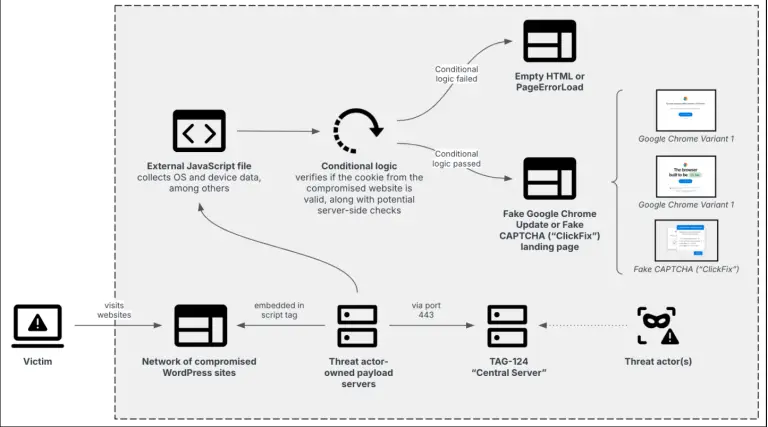
GrayAlpha, linked to FIN7, escalates tactics with fake browser/7-Zip updates and TAG-124 TDS, spreading NetSupport RAT in a multi-pronged infection campaign.

Katz Stealer, a new stealthy MaaS, is actively stealing data from browsers, crypto wallets, and apps, using advanced evasion tactics like steganography and Discord hijacking.

A sophisticated "ClickFix" phishing campaign uses fake Booking.com CAPTCHAs to deliver RATs and info stealers to the hotel and travel industry.

ViperSoftX, a stealthy malware, is actively spreading via fake software to steal cryptocurrency and enable remote control, affecting users globally.
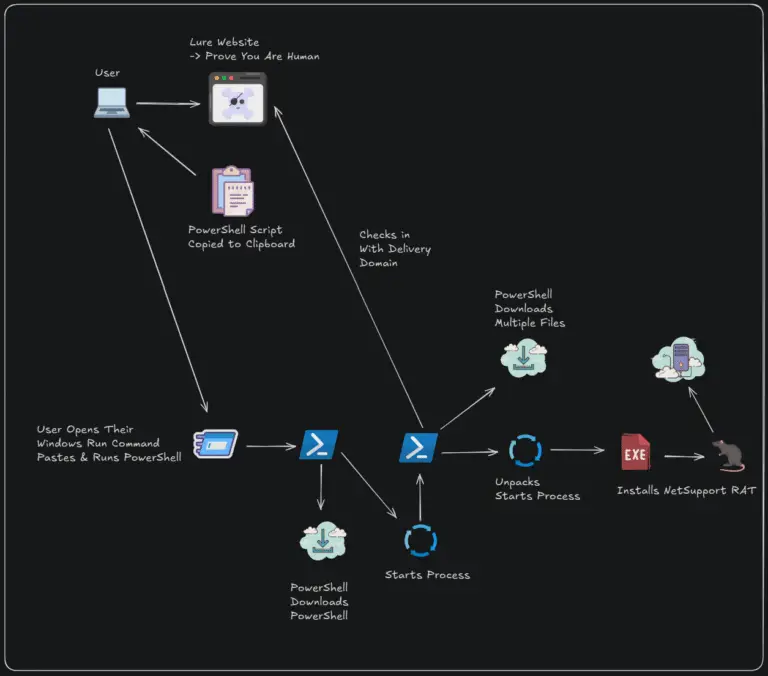
A new campaign uses fake DocuSign & Gitcodes pages to trick users into manually installing NetSupport RAT, gaining remote control.

K7 Labs details an evolved PowerShell malware, ViperSoftX 2025, featuring enhanced modularity, stealth, and persistence for advanced attacks.

Microsoft's "Edit" command-line text editor is set to be pre-installed in Windows 11, offering simple text file manipulation.

The Catena malware loader is using trojanized app installers (QQBrowser, LetsVPN) to deploy the memory-resident Winos v4.0 RAT.

A fake Google Meet page on compromised WordPress sites tricks users into manually running PowerShell commands, delivering remote access malware.

AI-generated TikTok videos are instructing users to run PowerShell commands, leading to the delivery of Vidar and StealC infostealer malware.