 Do Son
BRONZE SANDCASTLE uses Sandboxie DLL sideloading to run a modified Meterpreter backdoor in memory against targets in Asia and Africa.
backdoor
UpdraftPlus data breach exposed customer data and keys now used in an UpdraftCentral backdoor campaign. Update to 1.26.12 and check your sites.
An active WordPress XSS campaign exploits Ninja Forms flaw CVE-2026-94504 and CVE-2026-93836 to plant hidden admin accounts. Patch now.
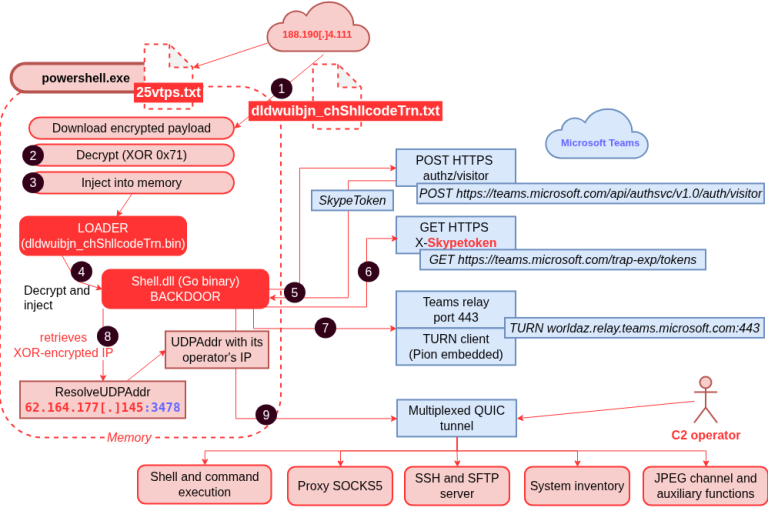
A new DragonForce backdoor hides in Microsoft Teams TURN relays and falls back to MQTT. See how it works and how defenders can spot it.
Microsoft details NeedyMantis malware, a modular backdoor that uses DLL sideloading to keep long-term access in telecom, academic, and government networks.

GEEKOM's official site served backdoored AMD mini PC drivers since December 2024 via a compromised legacy support page still indexed by Google.

A Head Mare TrueConf attack chains two zero-days to install the PhantomCore backdoor via a trojanized client.

Active exploitation of CVE-2026-18072, a CVSS 9.8 video embedder backdoor, grants attackers full administrative control over 20,000 WordPress sites.
GoSerpent backdoor drives a patient cyber espionage campaign against Southeast Asian governments, stealing files and credentials since at least 2021.

Symantec found Daxin malware active in Taiwan in May 2026, alongside a new Stupig backdoor that runs commands from the Windows logon screen.

Microsoft exposes the GigaWiper backdoor, a destructive tool that bundles disk wiping malware, fake ransomware, and remote control in one implant.
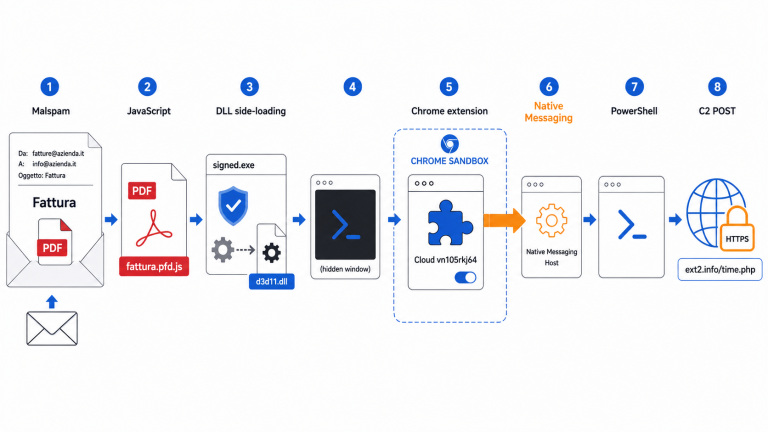
A Native Messaging backdoor pairs a malicious Chrome extension with a local host to run PowerShell, escaping the browser sandbox, says D3Lab.

Critical: Cemu 2.6 Linux binaries were backdoored via a developer's stolen GitHub token. If you downloaded Cemu for Linux between May 6–12, audit your system now.
Sophos X-Ops uncovers a fake Claude AI site (claude-pro.com) distributing an undocumented backdoor via DonutLoader. Protect your team from AI-themed lures.

Cisco Talos uncovers the FIRESTARTER backdoor in Arcane Door's latest attack on Firepower devices. Patch CVE-2025-20333 now to stop state-sponsored espionage.

Google warns of a massive Axios supply chain attack. Versions 1.14.1 & 0.30.4 deploy the WAVESHAPER.V2 backdoor via a hijacked NPM account. Patch now!
95M-download LiteLLM library hijacked on PyPI. TeamPCP's backdoor steals cloud tokens and hijacks Kubernetes clusters. Check for version 1.82.8 now.

Trend Micro reveals the BoryptGrab info stealer campaign using SEO-optimized fake GitHub repos to deploy the TunnesshClient reverse SSH backdoor.

Critical backdoor CVE-2026-0920 in LA-Studio Element Kit is being exploited in the wild. Former employee planted the code. Update to v1.6.0 immediately.

Arctic Wolf warns of automated FortiGate SSO attacks stealing configs and creating backdoors. Disable admin-forticloud-sso-login immediately.

Trust Wallet hit by an $8.5M heist after Shai-Hulud hackers poisoned the NPM supply chain. Binance is fully compensating affected version 2.68 users.

Koi Security uncovers lotusbail, a malicious npm package with 56k downloads that functions perfectly while stealing WhatsApp credentials and chats.