
 Do Son
Kaspersky warns of Webrat malware targeting researchers via fake GitHub PoCs for CVE-2025-10294 and other high-CVSS flaws to install a backdoor.
backdoor

Intezer reveals EchoGather, a new Paper Werewolf backdoor using XLL files and AI-generated decoys to target Russian defense and high-tech firms.

NANOREMOTE, a new Windows backdoor, leverages the Google Drive API for covert C2 and data exfiltration using OAuth 2.0 tokens. The malware shares a hard-coded AES key with the FINALDRAFT family, linking it to seasoned espionage actors.

A malicious Go package typosquat (bpoorman/uuid) operated for four years, using a hidden Valid function to silently encrypt and exfiltrate sensitive data to dpaste.com.

A malicious Rust package (evm-units) was live on Crates.io for 8 months, hiding RCE in a version check function. The loader uses VBScript and checks for Qihoo360 to compromise crypto developers on Windows/Linux/macOS.

Threat actors are actively exploiting a new WSUS RCE flaw (CVE-2025-59287) to gain SYSTEM shells and deploy the dangerous ShadowPad backdoor. Patch immediately!

Sekoia details PolarEdge, a Rust-based backdoor using a custom mbedTLS server for C2 on Cisco, QNAP, and Synology devices. The backdoor uses XOR 0x11 for config obfuscation and attempts to delete system utilities to block rivals.

WARMCOOKIE has resurfaced post-Operation Endgame with new execution handlers, a MaaS model, and evasive techniques like disguised scheduled tasks using company names.

The malicious PyPI package SoopSocks masqueraded as a SOCKS5 proxy but secretly installed a Go-based backdoor with SYSTEM privileges, leaking system data to a Discord webhook.

GTIG reveals BRICKSTORM, a stealthy Go backdoor linked to China-nexus UNC5221, targeting US legal/SaaS firms to steal IP and establish long-term espionage access.

Security researcher Puja Srivastava from Sucuri uncovered two malicious files designed to guarantee persistent attacker access by...

Cisco Talos uncovers a long-running espionage campaign using a new PlugX backdoor. The malware shows strong links to Chinese APT groups Naikon and BackdoorDiplomacy.
Zscaler ThreatLabz has uncovered a new backdoor malware, YiBackdoor, that shares extensive code with IcedID and Latrodectus and is being tested for ransomware ops.

A new report reveals a ToneShell backdoor from Mustang Panda. The malware targets Myanmar and uses anti-analysis tricks to evade detection.

A new report reveals a sophisticated XWorm backdoor campaign that uses .lnk files and a multi-stage infection chain to gain stealthy and persistent control of Windows systems.

A new RAT, disguised as an AI assistant, is using social engineering to infiltrate a role-playing community. The malware provides attackers with full remote control over infected PCs.
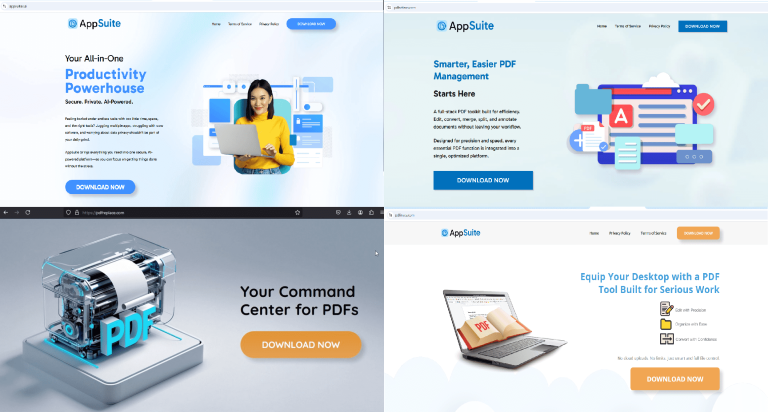
A new report reveals that the AppSuite PDF Editor is a Trojan horse that functions as a backdoor. Its developers even submitted it to AV vendors to get it whitelisted.

A new report reveals MystRodX, a stealthy backdoor that uses passive wake-up triggers and multi-layer encryption to operate undetected in networks for months.

Following U.S. intervention, the UK government has reportedly dropped its demand for Apple to install a backdoor in iCloud, which could restore Advanced Data Protection.

A new Kaspersky report reveals the PipeMagic backdoor has resurfaced, now tied to the exploitation of a Microsoft zero-day and targeting organizations in Brazil and Saudi Arabia.

NVIDIA states its GPUs have no backdoors or kill switches, arguing such controls are a security risk and would be a "gift to hackers," referencing the failed Clipper Chip.
Mustang Panda, a China-aligned APT, is using the ToneShell backdoor to target government and military sectors with phishing and DLL sideloading, masquerading as a legitimate Chrome component.