
 Do Son
A new stealthy campaign uses Windows LNK files to deploy the REMCOS backdoor via multi-stage PowerShell commands, bypassing antivirus and gaining full system control.
backdoor

The UK government is reportedly reconsidering its secret demand for an iCloud backdoor after US criticism and Apple's decision to disable Advanced Data Protection for UK users.

LAB52 uncovers a sophisticated phishing campaign delivering DeedRAT, a modular backdoor by Chinese APTs, targeting Southeast Asian governments via vulnerable AV software.

Kaspersky Labs reveals GhostContainer, a sophisticated backdoor targeting Microsoft Exchange infrastructure in Asia's government and high-tech sectors, using advanced evasion tactics.

The Rainbow Hyena threat cluster is unleashing PhantomRemote, a new backdoor, in phishing attacks against Russia's healthcare and IT sectors, leveraging compromised emails.

Unit 42 uncovers HazyBeacon, a novel backdoor using AWS Lambda URLs for stealthy C2. It's deployed via DLL sideloading, targeting Southeast Asian govts for trade documents.

A supply chain attack injected backdoor malware into Gravity Forms plugin downloads from the official website. The backdoor allows RCE and creates admin accounts.

AMOS malware just leveled up—now a backdoor, it poses a serious threat to macOS with persistent access and remote command execution.

China-aligned Hive0154 is using phishing lures themed around Tibetan issues to deploy the Pubload backdoor. Campaigns target the Tibetan community, US military

Confucius APT has a new modular backdoor, "Anondoor," delivering espionage payloads and evading sandboxes in targeted attacks on South and East Asian governments.
NCSC reveals "UMBRELLA STAND" malware targeting Fortinet FortiGate 100D firewalls. It establishes stealthy backdoors for long-term cyber-espionage

A C++ backdoor named Pickai is actively exploiting ComfyUI servers, compromising nearly 700 AI image generation hosts and posing a supply chain risk

Kimsuky APT is using HWP documents and stealthy AnyDesk backdoors in a new phishing campaign to infiltrate systems under the guise of academic collaboration.

Two malicious npm packages, express-api-sync and system-health-sync-api, act as remote-controlled time bombs, wiping entire directories with a single POST request.

Sophos X-Ops found a backdoored Sakura RAT targeting hackers and cheaters, spreading info-stealers via hidden scripts in open-source projects.

Earth Lamia, a China-linked APT, is targeting critical industries worldwide using SQL injection, CVEs, and custom backdoors like PULSEPACK.

Critical NETGEAR flaw (CVE-2025-4978) allows full admin access via hidden backdoor. Exploit details and PoC analysis inside.


A nearly three-year intrusion at SK Telecom compromised 27 million users, stealing IMSI, USIM keys, and texts, prompting SIM card replacements.

Zscaler reveals TransferLoader: a stealthy malware using IPFS and obfuscation to drop ransomware and backdoors. A new threat in the wild since 2025.

Arctic Wolf exposes Venom Spider’s More_eggs campaign, where fake resumes and polymorphic JavaScript target HR to deploy a stealthy backdoor.
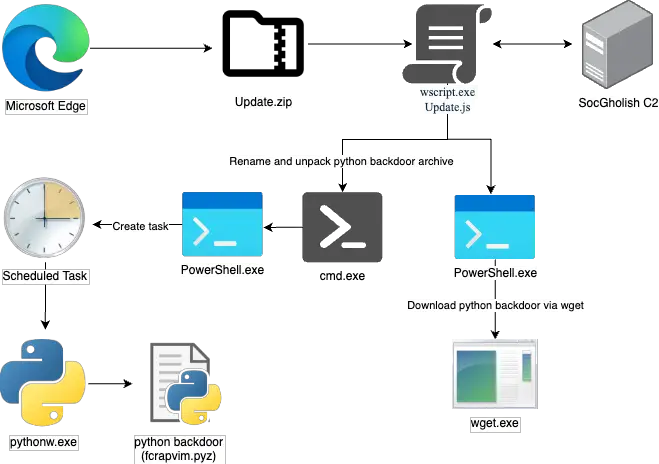
eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.