 Do Son
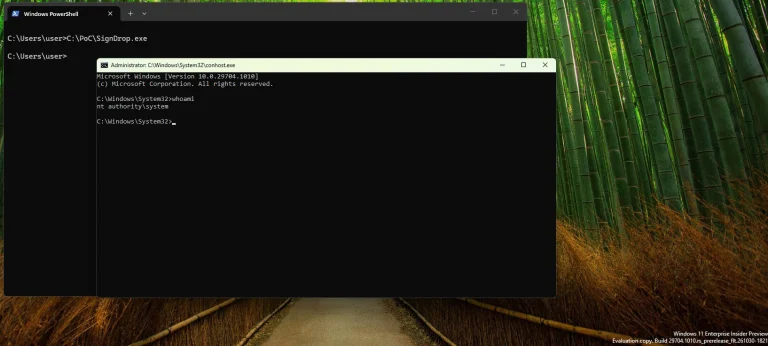
SignDrop, an unpatched Windows CLFS zero-day, now has a public proof-of-concept exploit that gives standard users SYSTEM privileges. No patch yet.
windows
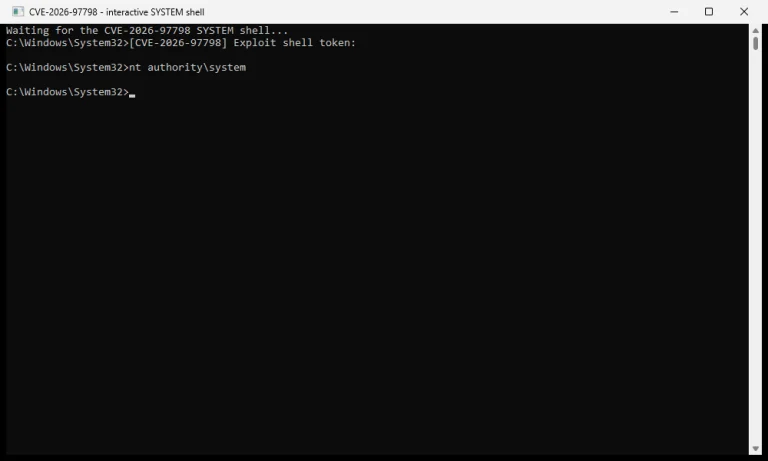
A proof-of-concept exploit for CVE-2026-97798, a Windows Error Reporting vulnerability, gives a SYSTEM shell. Install the October 2026 update now.
The Arc browser shutdown arrives December 22, 2026. Export your data now and move to Dia before accounts are deleted.

Gemini for Windows is here as a native desktop app for Windows 10 and 11, summoned with Alt + Space to take on Microsoft Copilot head-on.
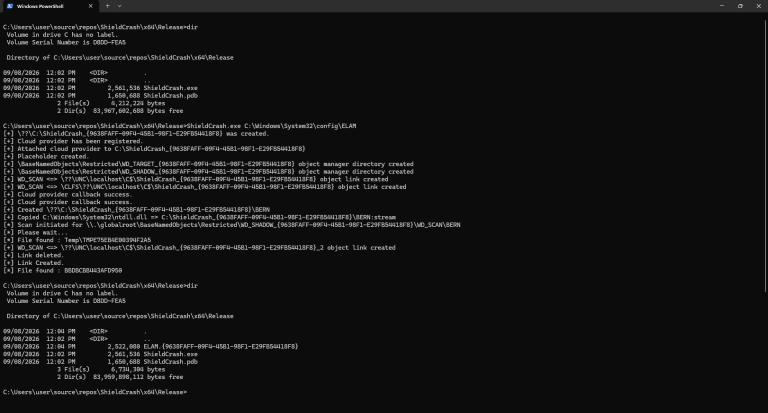
A Windows Defender 0day, CVE-2026-69414, has public PoC exploit code. ShieldCrash reads files as SYSTEM on all supported Windows versions.
Microsoft's September 2026 Patch Tuesday fixes two zero-day flaws, CVE-2026-81963 and CVE-2026-85880, both exploited in the wild.
Microsoft will require a Windows driver SBOM and VEX statement for signing from March 2027, aligning WHCP with the EU CRA.

Apple will finally develop a universal iPhone Windows copy paste feature due to EU regulations. Microsoft successfully petitioned for seamless clipboard sync.

CVE-2026-49176 is a Windows WalletService elevation of privilege flaw. Full details and a public PoC exploit are out, so patch Windows now.

LG monitor adware installs itself via Windows device metadata and pushes McAfee pop-ups. Learn how a Group Policy tweak blocks the unwanted software.
Zoom vulnerability CVE-2026-53412 (CVSS 9.8) allows unauthenticated account takeover over the network. Update Zoom Workplace for Windows to 7.0.0 now.
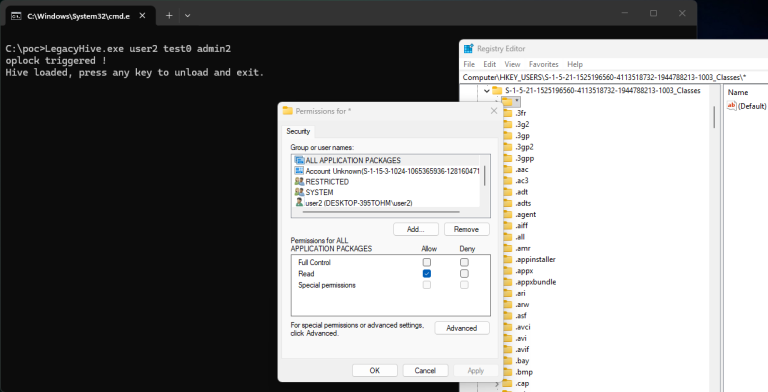
LegacyHive exploit code is public. This unpatched Windows privilege escalation flaw from Nightmare-Eclipse defeats the July 2026 patch.
WinFsp vulnerabilities CVE-2026-3006 and CVE-2026-7162 enable local privilege escalation to SYSTEM on Windows. Update to WinFsp 2026 Beta2 now.

StatCounter corrects flawed June 2026 data after reports falsely claimed Windows market share plunged to 56%. The anomaly stemmed from tracking errors.

Cursor AI editor found storing API keys and tokens in an unprotected SQLite database, allowing extensions to steal credentials silently. CVSS 8.2. No patch yet.

Python’s asyncio on Windows faces a high-severity RCE (CVE-2026-3298). A missing boundary check in ProacterEventLoop risks memory corruption. Update now.

Microsoft’s April 2026 Patch Tuesday fixes two "wormable" CVEs (9.8 & 8.1 CVSS). Secure your network against zero-click RCE and lateral movement now.

Adobe is bypassing Chrome security by quietly editing your hosts file to track Creative Cloud installations. Learn how this stealth telemetry works in 2026.

Google Chrome 145 patches 11 security flaws, including 3 high-severity bugs in CSS & Codecs. Update to v145.0.7632.45 now to stay safe.

Microsoft Excel's Agent Mode is now on Windows and Mac! Switch between GPT-5.2 and Claude 4.5 to automate complex workbooks and live web data.

Chrome 144 fixes high-severity flaw CVE-2026-1504 in Background Fetch API. Malicious sites could abuse downloads. Update immediately to stay safe.

A critical OS Command Injection (CVE-2025-68154) in the systeminformation Node.js library risks RCE on Windows. Affects 16M+ users. Upgrade to v5.27.14.