 Do Son
Patch CVE-2026-76418 now. This high-severity Cisco Secure Firewall vulnerability is exploited in the wild to trigger SSL VPN DoS reloads on ASA and FTD.
cisco
Cisco fixes 13 Snort 3 vulnerabilities, including CVE-2026-20043 and denial of service flaws affecting FTD, Meraki MX and IOS XE.
Review the latest Cisco security advisory to patch 10 Cisco Expressway vulnerabilities, including critical 9.8 CVSS root RCE flaw CVE-2026-76466.
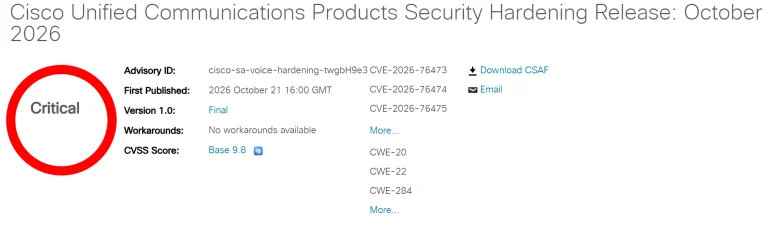
Cisco's security hardening release fixes Cisco Unified CM vulnerabilities, including CVSS 9.8 flaws CVE-2026-76473 and CVE-2026-76474.
Our weekly CVE report for Oct 12-18, 2026 tracks 5,499 new flaws and 12 exploited vulnerabilities, with CISA KEV trailing by up to 8 days.
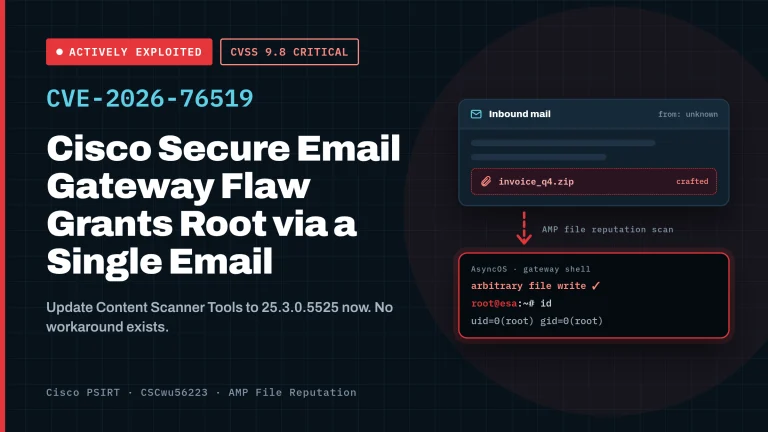
Attackers are exploiting CVE-2026-76519 (CVSS 9.8), a critical Cisco Secure Email Gateway vulnerability allowing root RCE via attachments. Patch right now.
A Cisco Finesse vulnerability, SSRF flaw CVE-2026-20362, has been publicly disclosed. Fixes arrive in early 2027, with no workarounds.
Cisco License On-Prem vulnerabilities include CVSS 10 flaw CVE-2026-76482 and password reset bug CVE-2026-20328. APIC and Meraki also patched.
Cisco NX-OS vulnerabilities fixed, including critical NX-API RCE flaw CVE-2026-76471 and CVE-2026-76455, across Nexus, MDS and UCS gear. Patch now.
Four critical Cisco Nexus vulnerabilities, including CVE-2026-76485 and CVE-2026-76465 (CVSS 9.8), allow root RCE on NX-OS switches. Patch now.
Attackers exploit CVE-2026-76504, a 9.8 authentication bypass in Cisco SD-WAN Manager that grants admin API access. Patch now.
Cisco patched 18 Secure Firewall vulnerabilities in FMC, ASA, and FTD, including critical unauthenticated root remote code execution flaws. Update now.
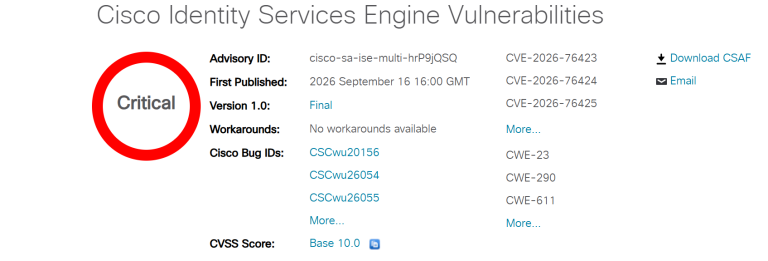
Cisco patched critical Cisco ISE vulnerabilities. Install updates to fix Cisco ISE vulnerabilities and prevent remote code execution and root takeovers.
An exploited Cisco ISE vulnerability (CVE-2026-76460) allows remote root access. Patch this critical Cisco ISE vulnerability to secure networks.
Cisco patched critical Cisco Secure Email vulnerabilities. Update to fix Cisco Secure Email vulnerabilities and prevent unauthorized system access.
CVE-2026-76461 (CVSS 9.8) is a Cisco Secure Email Gateway vulnerability exploited in the wild. SQL injection grants root command execution. Patch now.
Cisco Talos warns of Cisco FMC vulnerabilities actively exploited in the wild. Attackers chain CVE-2026-20079 and CVE-2026-20316 to deploy ransomware.
Details and PoC for a Cisco Secure Boot bypass vulnerability are public. Learn how this Cisco Secure Boot bypass affects UCS servers and appliances.
A public announcement exists for the Cisco Secure Email vulnerability pair in S/MIME decryption, plus a Cisco phone SIP denial-of-service flaw.
Cisco fixed critical Cisco IOS XR vulnerabilities discovered by AI models. Update systems to patch Cisco IOS XR vulnerabilities.
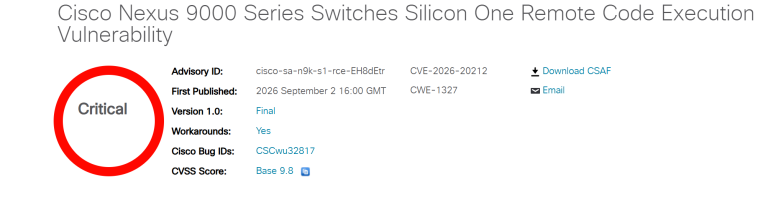
CVE-2026-20212, a critical Cisco Nexus 9000 vulnerability, lets an unauthenticated attacker gain remote code execution with root privileges. CVSS 9.8.
Cisco disclosed seven ClamAV vulnerabilities that let a remote attacker crash scanning via crafted files. Details are public. Patch now.